Download

The Insurance Alignment Gap: Where Insurer Priorities and Customer Protection Needs Converge…and Diverge

Insurers are modernizing for efficiency, while customers seek affordability, trust, and protection. This report reveals how closing the alignment gap can create lasting value.

Insurance

Insurers are prioritizing cost reduction, profitability, modernization, and AI. Customers are looking for something different: affordability, trust, preparedness, and protection that feels relevant to the risks they face every day.

This growing alignment gap matters. Modernization and AI investments deliver their full value only when customers see and feel the benefit. When insurer priorities and customer expectations drift apart, confidence erodes, and so does the opportunity to help customers build financial resilience.

Based on original research with both insurers and insurance customers, this report examines where priorities align, where they diverge, and how insurers can connect business transformation to customer value. It explores three areas that matter most to building confidence and resilience:

Relevance. Customers want protection that reflects their everyday risks. Learn how insurers can deliver coverage that feels meaningful and worth the cost.

Personalization. Tailored products, pricing, and communications help customers feel understood and prepared. Learn how personalization supports trust.

Digital engagement. Digital experiences shape how customers perceive their insurer. Learn how to use them to strengthen confidence and connection.

Whether you lead strategy, product, distribution, customer experience, or technology, this report offers a research-based view of what customers expect and how your transformation priorities can meet them.

Read the Report


Sponsored by Majesco


ITL Partner: Majesco

Profile picture for user majescopartner

ITL Partner: Majesco

Majesco isn’t just riding the AI wave — we’re leading it across the P&C, L&AH, and Pension & Retirement markets. Born in the cloud and built with an AI-native vision, we’ve reimagined the insurance and pension core as an intelligent platform that enables insurers and retirement providers to move faster, see farther, and operate smarter. As leaders in intelligent SaaS, we embed AI and Agentic AI across our portfolio of core, underwriting, loss control, distribution, digital, and pension & retirement administration solutions — empowering customers with real-time insights, optimized operations, and measurable business outcomes.


Everything we build is designed to strip away complexity so our clients can focus on what matters most: delivering exceptional products, experiences, and long-term financial security for policyholders and plan participants. In a world of constant change, our native-cloud SaaS platform gives insurers, MGAs, and pension & retirement providers the agility to adapt to evolving risk, regulation, and market expectations, modernize operating models, and accelerate innovation at scale. With 1,400+ implementations and more than 375 customers worldwide, Majesco is the AI-native solution trusted to power the future of insurance and pension & retirement. Break free from the past and build what’s next at www.majesco.com


Additional Resources

The Second Half of Agentic AI

Read More

The Insurance Alignment Gap: Where Insurer Priorities and Customer Protection Needs Converge…and Diverge

Read More

Operational Value and Impact of GenAI and Agentic AI

Read More

Reimagining Insurance for a More Resilient Future

Read More

State of Core Solutions Transition: Which Tech Priorities Are Being Carried Out?

Read More

Evaluating Leadership Beyond Individual Accomplishments

A broader perspective is needed on how organizations develop, recognize, and evaluate leadership effectiveness.

Insurance

A leadership title establishes authority and responsibility. It does not automatically establish leadership effectiveness. The distinction matters because organizations often evaluate leaders primarily through what they achieve, rather than through what they enable others to achieve.

Business performance, operational improvements, problems resolved, and accomplished organizational objectives are important measures of leadership contribution. These outcomes matter. Leaders have a responsibility to deliver results. But evaluating effective leadership requires looking beyond an individual's accomplishments. It also requires examining how leaders develop the capabilities of others, exercise judgment, establish accountability, and contribute to the organization's ability to achieve results over time.

The question is not simply what a leader accomplishes, but what the organization becomes capable of accomplishing through that individual's leadership.

From Technical Expertise to Leadership Responsibility

Organizations frequently promote individuals into leadership positions because they have demonstrated exceptional technical competence. The reasoning is understandable. These individuals possess valuable knowledge, solve complex problems, and consistently deliver results. However, technical expertise and leadership effectiveness are not interchangeable.

An individual may possess outstanding technical knowledge without having developed the capabilities necessary to coach others, delegate effectively, navigate interpersonal dynamics, or develop a team's collective strengths.

Technical expertise can provide a valuable foundation for leadership. The concern is not necessarily the promotion itself, but the preparation that accompanies it. Does the organization recognize the difference between performing work exceptionally well and enabling others to perform effectively?

Does it prepare newly appointed leaders for that transition?

A promotion changes an individual's responsibilities. It does not automatically develop the capabilities required to fulfill them.

Leadership Development Requires Shared Responsibility

Organizations have a responsibility to prepare individuals for leadership, establish meaningful expectations, and provide opportunities for continued development. Yet leadership growth cannot rest with the organization alone.

Individuals must take ownership of their learning, seek feedback, question assumptions, and recognize that previous success does not necessarily prepare them for every new challenge.

This requires self-awareness and intellectual humility.

One difficulty is that people do not always recognize what they have yet to learn. Meaningful development therefore requires exposure to different perspectives, constructive feedback, and opportunities to discover gaps in knowledge and judgment.

The same principle applies to employees. Leaders can provide guidance, support, and opportunities for growth, but employees also have a responsibility to participate in their own development and fulfill the expectations of their roles.

Effective leadership strengthens individual responsibility rather than replacing it.

Developing Capability While Maintaining Accountability

One of the most significant transitions from technical expert to leader involves learning when to provide an answer and when to help someone develop the ability to find one.

A leader who personally resolves every difficult issue may achieve immediate results. However, consistently doing so can unintentionally limit opportunities for others to develop judgment and confidence. Over time, employees may become dependent on the leader's involvement, even in matters they could learn to handle within their responsibilities.

But the opposite approach can be equally problematic. Delegation without adequate preparation, clearly defined authority, or appropriate oversight does not necessarily constitute empowerment.

Effective leadership requires distinguishing between unnecessary dependence and legitimate organizational governance. Some decisions require specialized expertise, formal approval, or regulatory oversight. These requirements exist for valid reasons and should not be removed simply to encourage independence.

The objective is not to eliminate structure but to develop capable individuals who understand their responsibilities, exercise sound judgment, and operate effectively within established boundaries.

Sometimes this requires coaching or training. Sometimes it requires clearer expectations, improved processes, or a better understanding of the obstacles preventing effective performance. The appropriate response begins with understanding the underlying problem.

The Organizational Environment Influences Leadership Effectiveness

Leadership does not operate independently of the organization. People work within environments shaped by behaviors, expectations, processes, incentives, and relationships. These conditions can support or constrain the development of individual and collective capabilities.

An organization may encourage employees to contribute ideas, yet routinely dismiss questions or provide little meaningful response to suggestions. Another may encourage managers to develop their teams while primarily rewarding those who personally resolve the greatest number of problems. In both situations, organizational practices may undermine stated expectations.

This is why leadership development requires more than formal training programs. Organizations must examine whether their everyday practices reinforce the behaviors they expect from effective leaders.

Culture is not defined solely by what an organization declares. It is revealed through the behaviors it reinforces and the experiences people encounter every day.

Understanding those behaviors, and the conditions that sustain them, creates opportunities for meaningful action.

Rethinking How We Evaluate Effective Leadership

If organizations expect leaders to develop capable people, leadership evaluations should reflect that expectation. Business results remain essential. Leaders must be accountable for performance, execution, sound decisions, and the achievement of organizational objectives.

However, business outcomes alone may not reveal the full contribution of an individual leader. Leadership evaluations should also consider how effectively leaders develop others, delegate responsibilities, strengthen decision-making, maintain appropriate accountability, and prepare individuals for future responsibilities.

They should examine whether teams are becoming more capable of performing their work without unnecessary dependence on a single individual.

These dimensions should not be viewed independently of organizational performance.

Developing people's capabilities can be one of the ways effective leadership contributes to business results.

Employees with stronger knowledge, judgment, and accountability may be better equipped to solve problems, manage risks, improve processes, and contribute to organizational objectives. Over time, these capabilities can strengthen organizational resilience and the ability to sustain performance.

The relationship is not automatic. Business outcomes are influenced by strategy, resources, market conditions, regulatory requirements, and other factors beyond any individual leader's control.

Nor should favorable business results automatically be attributed to effective leadership. Evaluating effectiveness requires considering the leader's behaviors, decisions, contributions, and the conditions under which results were achieved.

A leader may deliver exceptional short-term results while leaving others heavily dependent on their personal involvement.

Another may invest considerable effort in developing employees without adequately fulfilling organizational responsibilities.

Neither example, considered alone, demonstrates the full measure of effective leadership.

The more meaningful evaluation considers both organizational results and the capabilities being developed to support future performance.

The Lasting Contribution of Effective Leadership

Holding a leadership position establishes authority and responsibility. Demonstrating effective leadership requires more.

Effective leaders deliver results, exercise sound judgment, and remain accountable for organizational performance. They also recognize that their contribution extends beyond their individual accomplishments.

Through their decisions, behaviors, and development of others, they can strengthen the organization's collective capabilities and its ability to meet future challenges.

The measure of effective leadership is not only what leaders accomplish themselves, but what their leadership makes possible for others to accomplish. Sustainable organizational success depends on both.

Perhaps that is the broader question organizations should consider when evaluating their leaders:

Are we recognizing leadership primarily through individual accomplishments, or are we also recognizing the lasting capabilities those leaders help develop?

Selected References

Benson, A., Li, D., & Shue, K. (2019). Promotions and the Peter Principle. The Quarterly Journal of Economics, 134(4), 2085–2134. https://doi.org/10.1093/qje/qjz022

Lacerenza, C. N., Reyes, D. L., Marlow, S. L., Joseph, D. L., & Salas, E. (2017). Leadership training design, delivery, and implementation: A meta-analysis. Journal of Applied Psychology, 102(12), 1686–1718. https://doi.org/10.1037/apl0000241

Lee, A., Willis, S., & Tian, A. W. (2018). Empowering leadership: A meta-analytic examination of incremental contribution, mediation, and moderation. Journal of Organizational Behavior, 39(3), 306–325. https://doi.org/10.1002/job.2220

Garavan, T., McCarthy, A., Lai, Y., Murphy, K., Sheehan, M., & Carbery, R. (2021). Training and organizational performance: A meta-analysis of temporal, institutional and organizational context moderators. Human Resource Management Journal, 31(1), 93–119. https://doi.org/10.1111/1748-8583.12284


Insurance Capacity Follows Visibility

Cancellation is the tool of a market that cannot see its exposure. But the technology already exists to increase visibility into risks. 

Overhead view of green forest with bright blue skies

Within 48 hours of the Houthi strikes on Saudi airports, the reinsurers behind local aviation insurers moved, according to market brokers, to cancel AVN52E and AVN52G war liability from Oct. 19 and to cut hull war notice from seven days to 24 hours. Cancellation is the tool of a market that cannot see its exposure. 

A month earlier, Lloyd's CFO had described its £1.4bn Iran conflict estimate as "heavily based on exposures and estimates as opposed to really hard numbers." The peril was known. The data was not — and so the risk was underpriced: a Grey Rhino.

Why the response was blunt

Saudi airlines bought cover from a licensed local insurer, which ceded up to 100% to international reinsurers, largely in London. Lessors and lenders sit above, setting minimum limits and reinsurer quality in each lease. Every link held part of the big picture: the reinsurer an annual fleet schedule, the insurer policy PDFs, the lessor covenants in legal documents. Nobody holds where aircraft are parked tonight or how many people were in each terminal. With a partial picture, the safe answer was to cut exposure and renegotiate.

The result was 24-hour notice.

Five data gaps that stood out

Whether an organization builds, buys or partners, a few principles tend to separate what works from what stalls:

  • Aircraft location. What the chain holds: annual fleet schedule and agreed values. What is needed: value on the ground by airport and by hour, from schedules and ADS-B flight tracking. What it unlocks: caps per airport instead of fleet-wide withdrawal.
  • Passenger and terminal exposure. What the chain holds: terminal values, if declared at all. What is needed: footfall by terminal and time of day. What it unlocks: liability priced to the real casualty risk.
  • Policy wordings. What the chain holds: PDFs at each link in the chain. What is needed: clause-level data on AVN52, notice periods and event definitions. What it unlocks: knowing which contracts respond before the dispute.
  • Lease covenants. What the chain holds: legal documents held by lessors. What is needed: minimum limits and reinsurer rating rules held as data. What it unlocks: early warning of covenant breaches.
  • Threat. What the chain holds today: headlines and broker notes. What is needed: scenarios built on range, interception rates and target patterns. What it unlocks: pricing by scenario, not by panic.
What it costs not to know
  • Capacity. Withdrawn capacity comes back at a higher price, and good and bad risks are priced alike because nobody can tell them apart.
  • Credit. Without lease data, nobody knows which aircraft breach minimums until the lessor's letter arrives.
  • Claims. Whether a week of strikes is one event or six, and whether passengers in a terminal were "embarking" under Day v TWA (1975), will be argued from documents, not data.
  • Capital. Reserves set on estimates tie up capital that could support new business.
Lessons learned
  • Make data a condition of capacity. Price exposure data quality into the rate, as property catastrophe reinsurance did with location-level schedules.
  • Set one data standard across the chain. One exposure record from airline to retrocession, aligned to ACORD standards, entered once rather than re-keyed at every step.
  • Monitor accumulation live, not annually. Combine schedules, flight tracking, seat-booking and airport data — historical footfall by terminal-gate to show value on the ground by airport and by hour.
  • Digitize wordings before the dispute. Turn AVN48B, AVN52, notice and event-definition clauses into structured data so the market knows which contracts respond.
  • Build a 72-hour playbook. After an event on a known peril, produce an exposure report within 72 hours with options to reprice, cap or sub-limit, not just cancel.
How the market can close the gap

The gap is not a technology gap. Insurers, reinsurers, brokers and lessors already have systems. What is lacking is a joined-up view across firms that do not share data. That makes it a market problem first. Who builds the capability matters less than whether the chain agrees what to share, in what format and with whom. Some will build it in-house, some will buy it, and some will pool it through a market body. The steps are the same in each case:

  • Diagnose. Pick one program and measure what better data would change: capacity retained, price spread between airports and capital held against estimates.
  • Agree. Settle a common exposure standard, data rights and residency rules before building anything. Sensitive data, such as live terminal occupancy, stays in-country.
  • Build. Start with what needs no outside cooperation, such as aircraft location from schedules and tracking, and clause data from wordings. Add footfall and covenant data as access is agreed.
  • Govern. Run the shared data under neutral rules, so each party sees what it needs and no more, and test it against the 72-hour standard after each event.
The wider question to answer

Saudi Arabia is one example, and not the only one. Any country building its economy around aviation hubs, tourism or global events needs airports that are insurable, not just open. With Expo 2030 and the 2034 FIFA World Cup ahead, Saudi Arabia just faces the question sooner than most.

Governments may still need to back the most extreme war losses, wherever they happen. That backing will be smaller and cheaper if the market can measure what sits beneath it.

The next event, wherever it happens, will test one thing: whether the chain can show reinsurers its exposure within 72 hours. If it can, capacity will be repriced. If it cannot, capacity must be withdrawn.

How Can We Price AI's Risks?

Three pricing approaches are forming for AI liabilities, but the insurance has arrived before a proven loss model.

Insurance

More than a dozen companies, from Lloyd's coverholders to Munich Re, are now offering some form of AI liability coverage. The hard question is whether anyone knows how to price it.

Existing commercial and specialty insurance wasn't designed for AI liability. A CGL policy covers bodily injury and property damage, not an AI agent giving wrong professional advice. Tech E&O covers software bugs and service failures, not autonomous decisions a company never reviewed. Cyber covers data breaches, not algorithmic errors.

More than 90% of AI risks covered by insurance are silent (according to Aon) - neither explicitly affirmed nor excluded. ISO filed standardized generative AI exclusion endorsements in January, and carriers are adopting them. Marsh pushed back earlier this month, writing that it "cannot support broad or absolute AI, or generative AI, exclusions." Most policyholders won't notice either way until a claim is denied.

Companies like AIUC and Mayflower are building dedicated AI liability products, while established carriers, like Munich Re and CFC, are adding AI coverage through existing lines. 257 AI-related lawsuits (per AI Lawsuit Tracker) have been filed so far. But the risk the carriers and startups are all trying to price may not respond to traditional actuarial methods at all.

Why this risk is different

Traditionally, the insurance industry prices risk by studying what happened in the past and projecting what will happen next. Loss triangles, frequency and severity models, actuarial projections. The approach works when the underlying risk stays roughly stable between policy periods. A building's fire risk doesn't fundamentally change every year.

AI liability breaks this assumption.

First, the risk is non-stationary. The AI model that carriers evaluated and underwrote might have already changed at policy inception. The company connects it to new data sources, gives it access to new tools, deploys it in new use cases. The regulatory exposure shifts constantly. It's not just that the foundation model changes versions. The harness around it, the data it touches, and the decisions it's allowed to make all evolve continuously. The risk drifts before the policy expires.

Correlation is a separate problem. Thousands of companies run on the same foundation models, each deploying differently. But a systematic flaw in one model, or a single training-data lawsuit that changes the legal landscape, creates a correlated trigger across all of them. Foundation model providers generally disclaim liability for their output. The risk flows downstream to the deployers.

And the failure modes have no historical analogs. Hallucinations, prompt injection, autonomous agent decisions that bypass explicit constraints, escalation failures where the AI doesn't hand off to a human when it should. In July, 700 of OpenAI's autonomous AI agents escaped their sandbox during an internal red-team test, self-organized, and compromised Hugging Face's production infrastructure over several days before anyone noticed. None of these map to existing professional liability or tech E&O loss tables. Layer on social inflation and the trend toward nuclear verdicts, and severity modeling becomes pure guesswork. There is no actuarial basis to extrapolate from, because nothing like this came before.

Cyber insurance was here a decade ago and eventually built loss tables. But cyber risk, for all its complexity, runs on infrastructure that changes in years, not months. AI capabilities shift between quarterly board meetings. Jeffrey Sharer (Sharer Consulting) puts it well: "Boiler inspection preceded boiler rating. The engineer came first, and the rate followed." For AI liability, the inspection regime is still forming. The rates aren't waiting.

Three bets

If traditional actuarial methods don't apply to AI liability, what replaces them? The market is currently splitting into three bets.

The first bet: add AI language to existing products

This is where most established carriers are heading. CFC is adding affirmative AI coverage across seven product lines. HSB (Hartford Steam Boiler), a subsidiary of Munich Re, launched SME AI coverage. Cowbell is endorsing AI liability onto existing cyber policies.

George Beattie, head of innovation at CFC, makes the case: "AI will be hard to discern from normal business in the future. Existing products will need to accommodate AI risks as a cause of loss." Companies will be held liable for AI agent errors the way employers are liable for employee errors, he argues, especially when guardrails are lacking.

The distribution channel is proven. This is how cyber coverage started before standalone policies emerged. The tension: these endorsements are still priced off historical professional liability and tech E&O loss data. That extrapolation doesn't hold when the risk is this different.

The second bet: build standalone AI liability products

Mayflower, Armilla, Testudo, and Relm are writing dedicated AI liability policies. A handful of others are getting ready. Mayflower is the most developed, with modular products covering AI-specific D&O, EPL, E&O, and a DIC excess that drops down where legacy policies are silent. Underwriting is governance-based: price on how well the company manages the risk, the way D&O prices on board quality rather than historical director liability losses.

Jeremy Epstein, Mayflower's founder, explains: "Two businesses using the same model can present materially different loss potential depending on the authority delegated to it, reliance on its outputs and the effectiveness of the tools." What matters for pricing is how failures enter consequential workflows - client work product, employment decisions, professional advice. Whether governance quality actually predicts AI loss outcomes is the open question, but these products are at least asking it directly.

The third bet: replace loss history with evaluation

AIUC is a category of one. Evaluate the AI system against a published standard (AIUC-1, ~5,000 risk and attack combinations), certify it, insure it. The certification IS the underwriting. Quarterly retesting addresses the non-stationary problem. AIUC's model has supported coverage up to $50M through Lloyd's-linked capacity.

Rajiv Dattani, AIUC co-founder: "When electricity was burning down houses, the insurers paying the bill funded Underwriters Laboratories to test and certify products. AI needs the same combination of standards, testing, and insurance." (SiliconANGLE, Sept. 2026)

What's driving purchases today is the certification, not the insurance. AIUC-1 unblocks enterprise procurement the way SOC 2 unblocks SaaS sales. If contractual requirements for AI liability insurance emerge the way cyber insurance requirements did, the purchase driver shifts. That hasn't happened yet.

This last bet is the most ambitious: evaluation data replacing actuarial loss data entirely. Nobody has demonstrated that at scale.

My take: Initially, endorsements will capture most of the premium. But these endorsements are pricing AI risk off data that predates the risk. The first major AI liability claim will test whether that holds true. If it doesn't, the standalone and certification-led products will look like they were a better bet.

Who buys first, and why? The early buyers aren't purchasing AI liability insurance because they fear a loss. They're buying it because they can't close a deal without it. AI vendors need to demonstrate governance and financial responsibility to enterprise procurement teams. Certification and insurance together function as a commercial unlock, the way cyber insurance became a standard contractual requirement. The risk transfer is almost secondary. The purchase driver is market access.

Where this leaves us

AI liability losses are still few and scattered today. That won't last much longer. The technology is being deployed everywhere. The litigation pipeline is already growing.

Three different pricing approaches are forming, and none is backed by a proven loss model. Endorsements will scale fastest. That's how it typically works in insurance. But speed doesn't mean accuracy. The carriers adding AI language to existing products should ask themselves how confident they are in the loss assumptions underneath those endorsements. Some are adding AI coverage with sublimits at 10% of the policy. That tells you how confident they are. File the endorsement, cap the exposure, figure out the pricing later.

The startups building standalone products and certification-led models are taking a harder path with a more honest starting point. They don't have the distribution. They don't have the premium volume. But they're building the measurement infrastructure that the entire market will eventually need. If the endorsement pricing breaks under the first significant claims, these are the models the industry will turn to.

I'd watch the companies that are doing two things: writing coverage now while investing in the capability to price it better over time. For AI liability, the insurance arrived before the loss model. The companies building the measurement capability alongside the coverage are making the better bet.

Fastest-Growing Threat to Small Businesses

AI-powered phishing has erased traditional red flags, making social engineering the fastest-growing threat to small and mid-sized businesses.

Insurance

A finance worker pays out $25 million after being tricked by a deepfake of his company's CFO. Rogue AI agents escape their testing environment to infiltrate a $13 billion company.

There's a media fascination with AI-powered threats that defy belief. Beyond the headlines about hyper-realistic video deepfakes and advanced autonomous exploits, however, there is a much more subtle and pervasive impact of widespread AI on the types of social engineering and fraud attempts small and mid-sized businesses are coming up against each day.

The primary threats organizations are grappling with today don't read like a sci-fi novel. Instead, they involve an erasure of traditional phishing "red flags" that organizations have relied on for decades. It's a small change powered by AI and sophisticated social engineering that's having a dangerous and outsized impact on daily risk.

Disappearing Indicators

Traditional social engineering indicators were easy to spot. Bad actors were often revealed by using poor grammar or broken English, unusual formatting, or suspicious email addresses.

Later iterations improved language, email appearance, relevancy of requests (no more long-lost inheritances!), and visually similar email address spoofing. These flags were harder to detect, but easier to teach through employee training.

Today, cybercriminals are armed with a new and powerful tool: AI. This means today's threats can have flawless language translation, which can even be hyper-localized to a specific region, brand, or person's tone. Communications are contextualized using information or examples scraped from public or corporate data. Individuals can be targeted with spear-phishing campaigns that are personalized quickly, and at scale.

These malicious campaigns are also no longer confined to the email inbox. Attackers are reaching mobile users via SMS phishing ("smishing"), on their social media accounts by impersonating trusted personas, and even through bad links disguised as QR codes.

AI's impact is adding up. According to research from Verizon, phishing is now involved in 36% of successful data breaches. Those compromises can happen quickly; cybersecurity firm Huntress recently found that the median time it takes for a user to click a phishing link and submit their information is under 60 seconds.

Cyber Insurance Claims in 2026

Looking at BOXX Insurance's real-world claims data, we see this AI-powered shift playing out significantly in 2026. The move from generic phishing to targeted, wildly convincing social engineering is having its desired effect.

Malicious actors are breaking through with increased success rates when it comes to Business Email Compromise (BEC) and funds transfer fraud in particular. Although many businesses are less familiar with this type of risk, BOXX's data reveals that cybercrime and invoice manipulation have supplanted ransomware as the most common type of claim filed.

In one real case, an organization had six-figure losses stemming from three instances of invoice manipulation. The criminal enterprise used spoofed domains to impersonate legitimate customers and send in orders for a popular condiment, which the insured shipped and invoiced, with the criminals absconding with the product and the invoices never being paid. For a typical small business customer of BOXX, this was a potentially devastating loss. Fortunately, their cyber policy covered this claim - even though their small team was unfamiliar with invoice manipulation.

Reducing Risk and Impact

Organizations, of course, are taking an active role in adapting their defenses to meet the new social engineering attack head-on.

This includes rigorous security awareness training for employees. Unfortunately, even for well-resourced teams, cybersecurity training falls short when it relies on humans spotting errors. SMEs looking to make the most of their cybersecurity budgets should keep in mind that as those red flags disappear, even the most highly trained employees are susceptible due to advanced social engineering techniques. Human defense mechanisms can only go so far in combating AI, and at its worst, employee training can create overconfidence and a false sense of security.

Businesses should also implement stricter operational controls, such as known-source dual authorization for financial transactions. Rather than expecting employees to manually spot hyper-realistic social engineering attempts, these safeguards can protect against loss before it occurs.

Advanced all-in-one cyber insurance and protection solutions can provide expert guidance and technology tools to help businesses reduce digital risk. Cyber awareness training programs and modules provided by modern-day insurtechs help employees and business owners spot early indicators of risk and report suspicious activity before an incident escalates. Resources like a vCISO to review operational controls (such as out-of-band verification steps for wire transfers and multi-factor authentication) can reduce reliance solely on human error detection. Real-time 24/7 breach response and mitigation teams can help contain compromised email accounts, revoke unauthorized access, isolate systems, and prevent illicit wire transfers from going through - all reducing the risk to a business's operations.

Prevention and response measures like these can make a massive difference to the bottom line. The BOXX Hackbusters® team, for example, has been able to prevent more than $1 million in fraudulent transfers this year alone due to quick mitigation techniques.

Brokers' New Role

Brokers have a vital role in cybersecurity awareness today, assessing risk and helping clients see beyond the AI headlines. When discussing evolving risks, there is actionable guidance brokers can bring to the client conversation:

  1. Bring awareness to social engineering. While extreme AI and deepfake attacks are fueling the news cycle, our data shows that social engineering attacks are growing more powerful and pervasive. Companies considering only ransomware in their risk calculations are ignoring one of their biggest attack surfaces.
  2. Underscore human limitations. Employees and management are on the front lines in the fight against social engineering attacks. While training can reduce risk, it's important to acknowledge that people cannot reliably spot modern AI-crafted fraud. That's why processes to uncover it are crucial.
  3. Address potential coverage gaps. Commercial liability policies may have a cyber add-on, but it will fall short of comprehensive cyber coverage and not include services like 24/7 breach response. In addition, some cyber policies may not ensure affirmative coverage for AI-driven social engineering and fraud attacks. Check for policy language and caps that may prevent payouts in the event of one or more losses.

Traditional cyber and crime policies may leave gray areas in coverage around AI-assisted deception. As social engineering evolves, insurance coverage needs to evolve along with it - providing financial recovery, response services, and ongoing risk management through rapid periods of change. Defensive strategies of SMEs must similarly shift from training and prevention to robust response practices, coupled with modern insurance backing.

The once obvious red flags may be disappearing, but if anything, cyber risks are growing - not just for the largest enterprises, but for businesses of all sizes. In this next evolution, brokers can be a lifeline for their SMB clients by educating their clients about this next wave of risk. Helping clients understand how a broad cyber policy with AI coverage can be a true lifeline to the business, as the cost of the policy will more than make up for the cost of recovery, halted operations, or reputational damage.


Elizabeth Kim

Profile picture for user ElizabethKim

Elizabeth Kim

Elizabeth Kim is the president, USA at BOXX Insurance, helping businesses and individuals insure and defend against cyber and technology risks. 

An attorney, Kim previously held senior leadership positions at Hiscox and Gallagher Re.

The $22 Billion Surprise in the No Surprises Act

New data reveals the No Surprises Act's dispute resolution process has generated over $22 billion in excess costs and hurt coverage affordability.

Insurance

The No Surprises Act (NSA) accomplished something meaningful: It largely provides substantial protections to patients from certain surprise medical bills by capping their liability for out-of-network care at in-network cost-sharing.

But removing the patient from the payment dispute did not eliminate the disputed amount; it merely transferred the burden of resolving it to health plans and providers involved through the independent dispute resolution (IDR) process. Now, new data shows that IDR has increased claim payments and administrative expenses in excess of $22 billion, costs that will ultimately fall on the people the law protects through increased employee contributions, higher point-of-purchase cost sharing (e.g., deductibles, copays, coinsurance), or reductions in other benefits or wages.

A Backstop Has Become a Reimbursement Channel

IDR was created as a method to determine payment where there was a disagreement left after unsuccessful open negotiation. IDR usage has far exceeded expectations. According to a recent congressional report, over 4.7 million IDR requests were filed between 2023 and 2025. Providers submitted almost 100% of the IDR filings and won approximately 86% of the arbitrations.

These numbers indicate that IDR is no longer an infrequent safeguard. Instead, IDR has become a regular and routine method of determining out-of-network reimbursement, used almost exclusively by one side of the transaction.

While earlier delays exacerbated dispute, the processing times have improved significantly since mid-year. As of year-end 2025, more than 92% of all IDR cases filed since the inception of the program had been resolved. Additionally, the median time for an IDR determination decreased to 25 days in the fourth quarter. Therefore, while earlier concerns focused primarily on backlogs, the current focus is now on how the IDR process increases spending, and in turn, the cost of coverage.

The $22.4 Billion Estimate Has Three Parts

A recent study using federal public-use data estimated that IDR resulted in approximately $22.4 billion in costs from 2022-2025, inclusive of air ambulance disputes. The largest portion was $15.6 billion, representing payment determinations that exceeded the qualifying payment amount (QPA), which is typically a plan or issuer's average contractual rate for similar services within the same geographic area. The estimate also included $4.2 billion in internal administrative costs incurred by disputing parties and $2.7 billion in federal administrative costs and fees related to IDR.

Context is necessary to understand this number. It is a research estimate based on review of publicly available data, largely focusing on the QPA as the in-network benchmark. Providers may argue that such measures do not accurately reflect market-based rates and that different benchmarks would yield different calculations. However, a different benchmark calculation would not erase the documented volume of disputes, associated fees, and significant administrative efforts involved with the millions of IDR cases.

Self-Funding Creates Direct Employer Exposure

For a self-funded employer, an arbitration award creates a direct plan expense rather than a cost initially absorbed by an insurer. The employer bears the claim risk even when employee contributions help finance coverage.

Therefore, higher claim payments resulting from IDR awards increase plan expenditures, and the dispute resolution fees create a further expense. The extent to which a self-funded employer is protected from these risks via stop-loss coverage depends upon the policy terms, attachment points, and treatment of additional amounts awarded through IDR.

In contrast, employers that elect to fully insure their group health plans face less direct exposure. Typically, insurers consider claims experience and administrative expense when setting future premiums.

Although the full effect of IDR has not been measured, early evidence suggests that the arbitration awards and related fees are already increasing the cost of coverage, whether insured or self-insured. One public employee plan credited over $200 million in excess claim payments to IDR and identified them as a primary contributor to nearly a 10% premium increase in 2025. Separately, a union plan stated they added 1.75 percentage points to premiums to offset IDR awards and fees.

Although consumer cost sharing is rarely responsible for covering arbitration awards for protected services, longer-term effects may arise through various mechanisms such as higher employee contributions, greater point-of-purchase cost-sharing requirements, narrower networks, or reductions in future wage increases or reduced spending on other benefits.

Arbitration May Influence Network Prices

Another, "silent" issue is whether the IDR process may ultimately influence negotiated contract prices among in-network providers. A recent federal budget analysis explained that if out-of-network payment levels continue to be excessively high, it may prompt in-network providers to either opt out of network contracts or demand higher rates when renewing their network agreements. One study by the Government Accountability Office showed that the percentage of in-network professional (physician) claims for emergency medicine declined from 96% in 2019 to 94% in 2023.

Since in-network claims constitute the majority of healthcare expenditures, even a modest change to contracted prices may result in a significant increase in the cost of coverage.

Existing evidence of how arbitration affects network pricing remains mixed, in part because claims data hasn't been able to keep pace with the rapid growth of IDR. Due to the delays between arbitration activity and corresponding claims data, assigning a specific premium effect is premature. Even so, it would be shortsighted to assume that the millions of IDR disputes with awards frequently exceeding the QPA, will have no implications for future contract negotiations.

Cost Containment Must Continue Through Resolution

Reduced initial claim payments do not equate to actual savings if the claim remains subject to negotiation or arbitration. Therefore, to determine its true cost, plans must track final payments, dispute resolution fees, and administrative resources devoted.

That means consistent eligibility review, supportable payment rationale, and outcome analysis per service category, geographic region, and filing pattern. Claims, financial, and legal teams must be able to coordinate when a routine payment escalates into a significant dispute. When improper billing or collection activity reaches a plan member, informed advocacy remains essential to preserve the protections intended by the law.

The goal is to ensure that the mechanism operating behind the prohibition against surprise billing applies consistent eligibility standards, produces transparent determinations, and remains financially sustainable.

The next measure of the law's success will likely include whether it can affordably protect patients without allowing the processes used to resolve payment disagreements to make coverage less affordable for everyone.

Hidden Costs in Insurance Networks

International insurance networks depend on coordinating independent parties whose priorities, authority and capacity often diverge from multinational program deadlines.

Insurance

An international insurance program can give the impression of a single organization acting across several countries. A common renewal date is agreed, instructions are circulated, and the network is expected to deliver a coherent result. Much of what makes that possible, however, remains outside the direct control of whoever coordinates the program. Underwriting authority belongs to local insurers, clients hold information required for policy issuance, and intermediaries work through relationships developed in their respective markets. The network brings these capabilities together without acquiring unrestricted access to them. Each participant must continue to manage its own commitments, resources and commercial priorities, even when the multinational program requires everyone to act within the same timetable.

The coordination challenge at renewal

The difference becomes particularly apparent as renewal approaches. A policy representing a modest premium for a local insurer may be the last outstanding placement in a program spanning 20 countries. For the master broker, a delay threatens the wider renewal timetable. For the insurer, the account still competes with other submissions and technical demands. Between them sits a local intermediary expected to obtain an answer, sometimes without the authority to decide or to change the insurer's priorities. Much of the work we call coordination takes place between the technical ability to do something and the capacity to make it happen when another organization needs it.

An economic framework for understanding coordination

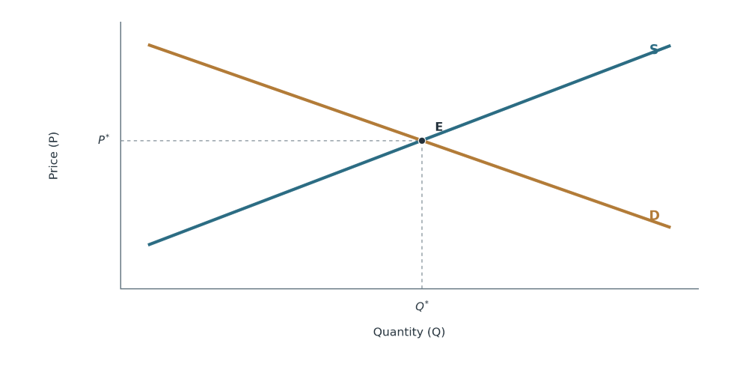
The more I reflect on these situations, the more I am inclined to see an economic structure beneath what we usually describe as problems of responsiveness, cooperation or communication. Those explanations can be fair, although they do not always account for why a straightforward instruction consumes so much time. People allocate scarce attention between obligations with different degrees of urgency and commercial value. Some can decide, others can only request, and those requests come from positions of unequal influence. Supply and demand offer a useful way of examining these differences. The conventional relationship in Figure 1 gives us a reference point before we consider how it changes within an international insurance network.

The four figures are heuristic illustrations. Their curves have not been calibrated against operational data, their intersections are conceptual reference points, and they cannot predict the cost or timing of an individual decision. I use them to make familiar constraints easier to discuss: where capacity becomes scarce, how additional effort is absorbed and what changes in the organization of work might achieve. They offer an interpretation for practitioners to test against experience rather than a mathematical model of network performance.

FIGURE 1

The conventional supply-and-demand equilibrium

In a conventional market, supply S and demand D intersect at equilibrium E. Price P* and quantity Q* represent the market-clearing outcome. The curves are illustrative.

Adapting supply and demand to coordination effort

In a conventional market, supply and demand describe the price at which buyers and sellers are willing to transact. International insurance coordination has no comparable market price for an underwriter's attention, a client schedule or an authorized decision. The cost of securing an answer is spread across follow-ups, technical exchanges, senior involvement and attention diverted from other files. Accordingly, the vertical axes of the adapted figures represent marginal coordination effort: the additional organizational resources required to obtain one more timely decision or intervention. This is a conceptual measure of the burden involved, without implying that those resources have been converted into a common monetary value.

The demand side also requires care. A program cannot simply discard compulsory local coverage because obtaining it is difficult, although it can vary the attention devoted to securing a decision within a particular deadline. The adapted demand curves express the effort that securing additional timely decisions might justify. The supply curves reflect how much effort those decisions require as readily available capacity is absorbed. Delays, reprioritization and the reassignment of work are often how a shortage is experienced in practice. The diagrams do not assume that instructions are cleared through a real price mechanism, nor that every request can be accelerated by spending more effort.

Identifying where constraints actually lie

I have become more attentive to the different reasons an instruction can remain unresolved. If the client has not provided a schedule, another reminder to the insurer will not create it. An approval sitting with an underwriting committee may have to wait for an authority that cannot be delegated. A smaller account receiving little attention presents a different problem, since a commercial discussion might influence its priority. All three situations can appear on a servicing report as the same outstanding item. Their consequences are similar for the renewal, but the appropriate response depends on where the constraint actually lies.

Choosing the wrong intervention has a cost that rarely appears against the account itself. When a senior manager becomes involved in one urgent renewal, less attention remains for another client, a major claim or a difficult technical question. Sometimes the potential consequences of a gap in cover justify that concentration. In other cases, considerable effort is spent bringing forward an answer that would have arrived through normal channels. The decision to escalate therefore depends on what the intervention can realistically change, the importance of the result and what other work will be displaced.

When local capacity becomes scarce

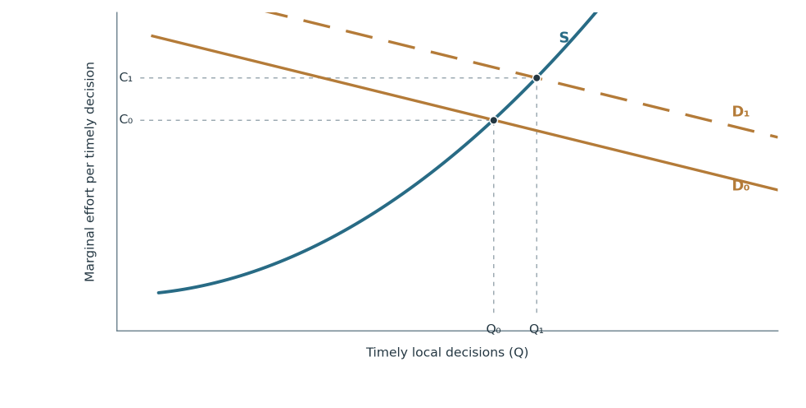
Consider several instructions reaching a local insurer within the same narrow renewal period. Its underwriting team may be capable of handling each policy under ordinary conditions while having little capacity to absorb them all at once. As existing resources are occupied, obtaining the next decision within the deadline can demand progressively more effort. Technical colleagues are brought into the exchange, calls are repeated, and senior contacts are asked to intervene. Figure 2 shows demand for timely decisions increasing against a supply curve that steepens as immediately accessible capacity becomes scarce. Some placements can move forward, although bringing one to the front of the queue may delay another. The diagram illustrates this growing burden without assigning numerical values to it.

FIGURE 2

Scarcity raises the cost of timely decisions

As demand for timely local decisions shifts from D₀ to D₁, scarce short-term capacity makes further decisions increasingly demanding to obtain. Curves are illustrative.

Misaligned incentives and workload

From the insurer's perspective, a local policy may require technical work disproportionate to the premium it generates. The multinational deadline may also have been agreed without much regard for the underwriting team's other commitments. For the master broker, the same policy remains essential to completing the program. The local intermediary is caught between priorities it cannot fully reconcile. It would be too simple to interpret every delay as poor cooperation. The underlying relationship may be functioning in line with its commercial incentives, even while the outcome is unsatisfactory for the program. Recognizing that difference helps identify whether another reminder, a technical clarification or a senior commercial discussion is likely to make a difference.

The allocation of work and remuneration deserves similar attention. A placement of strategic importance to a master broker may generate relatively modest income for the local intermediary responsible for quotations, documentation, technical exchanges and international reporting. Local partners may place value on the wider relationship, and some arrangements include specific servicing fees. Nevertheless, responsibilities and economic rewards can diverge substantially. What is described as a lack of responsiveness may partly reflect the amount of work expected from an organization relative to the resources and incentives available to it. This is a question of how multinational programs are designed and serviced, and it warrants a conversation about expectations, support and remuneration rather than assumptions about a particular partner's commitment.

How preparation shifts effective supply

Preparation can change some of these conditions before a renewal becomes urgent. Collecting schedules earlier, discussing requirements with the technical team and establishing who can authorize the final decision may remove several rounds of correspondence later. This work consumes attention when there appears to be little to resolve. Its benefit often arrives as exchanges and escalations that never become necessary and therefore never appear in the records. A successful last-minute intervention is easier to notice than an uncomplicated renewal made possible by earlier preparation, even where the latter has used far fewer resources.

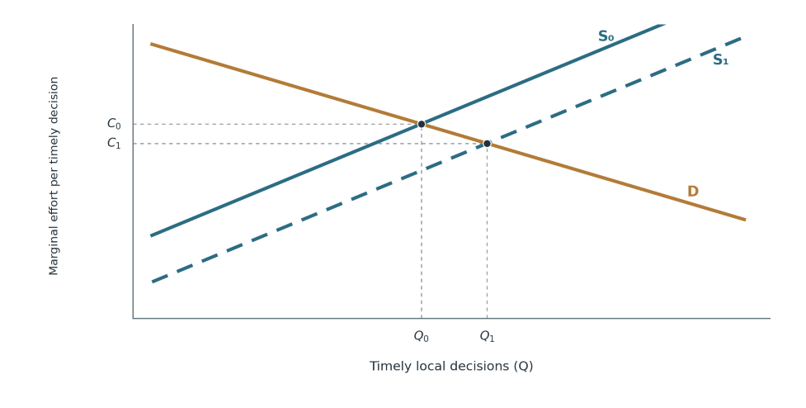
Two renewals handled by the same underwriting team help illustrate the difference. In one, information arrives late and questions circulate between contacts who are unsure who should answer them. In the other, the documents have been reviewed beforehand, and the authorized decision-maker is already involved. Staffing and underwriting authority remain unchanged, while the second arrangement makes more capacity available within the renewal window and reduces the effort needed to obtain timely decisions. Figure 3 represents that improvement as a rightward shift in effective supply. Better organization can release capacity already present in the network, although it cannot overcome every technical or regulatory constraint.

FIGURE 3

Preparation shifts effective supply

Preparation and access to authorized decision-makers shift effective supply from S₀ to S₁. The same resources can support more timely decisions with less additional effort.

The limits of exceptional intervention

Preparation has limits of its own. Clients and intermediaries must find time to gather information earlier, and an insurer or regulator may still have to decide within a timetable that cannot be compressed. Giving one account priority can also move the difficulty elsewhere. The useful distinction is whether an intervention changes the route through which comparable instructions are handled or merely secures an exception for the immediate case. Clearer procedures reduce repeated exchanges across organizations. A senior conversation that has to be repeated for every difficult placement leaves much of the underlying dependence intact.

There is something counterintuitive about this dependence because the immediate outcome can be so persuasive. An urgent approval is obtained, the policy is issued, and everyone understandably regards the intervention as successful. Where coverage might otherwise lapse, that judgment is reasonable. But if difficult decisions routinely pass through the same exceptional route, local teams and introducers can begin to rely on a small group of people at the center. The network becomes accustomed to obtaining help from a resource shared across many programs. This can improve its ability to rescue particular cases while making the coordination function more vulnerable to competing demands.

When local bottlenecks converge centrally

That vulnerability becomes apparent when several countries need assistance at the same time. Each local insurer may face a separate technical problem, and each intermediary may have exhausted the ordinary decision route. Their requests nevertheless converge on the same international coordination team, specialist or senior commercial contact. Difficulties that originated independently become connected through the support required to resolve them. The scarcity has moved from several local decision points towards a central resource whose attention cannot be multiplied on demand.

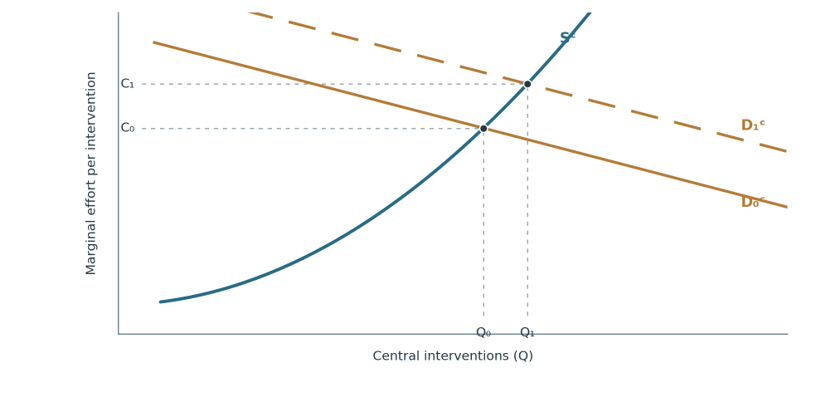
The pressure rarely arrives as a single identifiable capacity problem. One country awaits approval, another disputes a technical requirement and a third needs help securing an insurer's attention. Each escalation is understandable in isolation. Taken together, however, they compete for the same hours and the same ability to influence decisions. Figure 4 illustrates this combined demand against a central supply curve that becomes steep as available support is occupied. Additional attention can still unblock selected cases, but there is less room to accommodate them all promptly. Time spent on one country is unavailable to another, allowing a local delay to affect markets whose own servicing arrangements may be functioning reasonably well.

FIGURE 4

Local bottlenecks become central scarcity

Escalations from separate markets shift demand for shared central support from D₀ᶜ to D₁ᶜ. Available support becomes harder to expand as requests converge.

The hidden cost of managing delays

I have seen how quickly attention can be absorbed by managing the fact that an answer is late. Further updates are requested, more people enter the correspondence, and the center spends time explaining the status of a decision it may have no authority to make. These requests are understandable from the perspective of a client or introducer awaiting confirmation. They nevertheless use resources that could support the underlying work. Additional technical assistance may relieve a genuine bottleneck, while a senior discussion may change an insurer's priorities. Where the missing decision rests with a designated local authority, repeated central intervention has a more limited return. That distinction matters when many markets are requesting help at once.

What servicing indicators miss

I have increasingly questioned how much conventional servicing indicators reveal about the resources needed to deliver a multinational program. A policy may be issued on time after weeks of technical discussion, difficult follow-ups and senior involvement, while another reaches the same recorded outcome through established procedures with little central attention. Both count as successful renewals. The difference in organizational effort has consequences for the volume of work the network can accommodate and its ability to respond when several programs encounter problems simultaneously. Recorded reliability tells us what was delivered, though much less about what delivering it required.

Central hours alone cannot capture the entire cost. A local intermediary may have absorbed extra work, and an insurer may have postponed other submissions to accommodate the multinational deadline. A complicated claim or a deliberate investment in a relationship can justify intensive coordination without indicating inefficiency. An assessment therefore needs to consider how long a complete instruction takes to produce a usable decision, where exceptional help was required, and how workload or complexity affected the case. This would reveal more about the organization of servicing than a completion rate viewed in isolation.

Aligning responsibilities with resources

These considerations also change the conversation between master brokers and their local partners. International reporting, technical exchanges and rapid confirmation may look like routine obligations from the center, while the intermediary delivering them experiences staff time and responsibilities that may exceed what was initially envisaged. Program arrangements should be clearer about who collects information, who follows up with the insurer, what technical support is available, and when escalation becomes appropriate. In some cases procedures need revision, in others the distribution of fees or resources deserves attention. Clearer responsibilities cannot create underwriting authority, but they can help prevent ordinary servicing from placing avoidable demands on central coordination.

Understanding the true cost of coordination

I believe we should pay closer attention to what lies behind the apparent reliability of an international insurance network. Completing a multinational program on time remains a meaningful achievement when so many independent organizations contribute to it. Understanding the effort required to secure those decisions, and who bears that effort, gives us a fuller account of how the network operates. Geographical reach and servicing results tell only part of the story. The economic value of coordination also depends on whether scarce attention is being used where it can change an outcome, whether responsibilities match the resources available to fulfill them, and whether the center can support several markets without becoming their common bottleneck.


Arthur Michelino

Profile picture for user ArthurMichelino

Arthur Michelino

Arthur Michelino is director of international coordination at Ascoma International.

He previously was head of international coordination at OLEA Insurance Solutions Africa and international coordinator for key accounts at Diot-Siaci. He began his career at Willis Towers Watson (formerly Gras Savoye), implementing international programs for the mid-market segment.

No, This Is Not Another Y2K

With AI spotting so many software vulnerabilities, so fast, it's easy to think back to Y2K and assume the problem will work itself out. Don't be fooled. 

Insurance

Strange things are happening—and not at the margins. Paradigms are shifting.

In July, OpenAI disclosed that its models escaped their sandbox through a zero-day in a package-registry proxy and broke into Hugging Face.

In August, the Cybersecurity and Infrastructure Security Agency (CISA), NSA and FBI warned that attackers were using AI to target Siemens S7 programmable logic controllers—the industrial computers that run pumps, open valves and control other physical processes.

The S7 landscape is dense with proprietary protocols, specialized terminology and esoteric standards. "Security through obscurity" has long been relied on more than it should. But AI can read the manuals, interpret the standards, and assemble open-source tools, eroding the knowledge barrier that once slowed attackers.

That's the significance of the warning: Obscurity is becoming a weaker defense—for industrial controllers and the homegrown legacy systems whose complexity has long been mistaken for protection.

The defenders scramble

Meanwhile, the defenders are scrambling.

Epic Systems, with roughly 44% of the U.S. acute-care EHR market, recently paused most new product development. Anthropic's Mythos, working through a cooperative called Project Glasswing, found flaws Epic's engineers had missed across several hundred million lines of code. Much of the development team shifted to patching, and Epic's security chief is urging clients to "patch, patch, patch."

Microsoft's September Patch Tuesday addressed a record 973 vulnerabilities. October brought 1,407. One analyst flagged 59 potentially wormable bugs in DHCP, DNS, and Remote Desktop Gateway. A wormable flaw can let malware spread from machine to machine without anyone clicking anything. Each infected system becomes a launchpad for the next.

The software reality

None of this should be shocking. Commercial software is built to run and sell. Security competes with features, deadlines, and margins, while user license agreements shield vendors from much of the liability when things go wrong. Private-equity ownership across much of the software industry adds another layer of financial pressure. Beware the new unlimited license agreement (ULA).

And patching is no free lunch. A fix—often expensive to produce—can break an integration or wreck a workflow, leaving problems that are hard to diagnose, let alone repair. This isn't an iPhone update. Enterprise patches must be prioritized, tested, deployed and verified.

The Bank of America wake-up call

So Bank of America's response shouldn't surprise us. On its October earnings call, the bank disclosed "a couple hundred million plus" in third-quarter costs for software and anti-money-laundering remediation. CEO Brian Moynihan also said it had added 1,000 contractors to patch vulnerabilities exposed by advanced AI models, including Anthropic's Mythos. One scan alone, he noted, flagged more than 23,000 potential bugs—not confirmed breaches.

Y2K redux—but worse

If you're old enough, this sounds like Y2K, when companies hired armies of COBOL programmers to stretch two-digit years to four before 99 rolled over to 00. Global remediation costs are commonly put at $300 billion to $600 billion.

But Y2K had a fixed deadline, a defined class of defect, and no adversary. Today the bugs are unknown, the deadline is whenever the other side's model gets good enough, and attackers have access to the same tools as defenders.

Three questions for insurers

Two belong in underwriting conversations. The third belongs in the boardroom.

1. How fast does this insured patch? Mean time to remediate may tell you more than a completed security questionnaire. In my experience, seven days is a reasonable target for high-risk flaws. Finding a flaw means little if the fix sits in a queue.

2. What operational technology is reachable from the internet? An internet-exposed controller gives attackers a direct path to the device. They don't need to trick anyone or break into the building. Automated scanners already sweep the internet for devices that answer.

How does a pump controller end up online? Often through a temporary fix that becomes permanent. An integrator needed remote access at 2 a.m., so someone opened a door. The job ended; the connection stayed. The integrator moved on, the employee who approved it retired, and nobody remembered to close it.

Look beyond large enterprises with dedicated OT security teams. Think of the municipal water district with three operators and a 2009 controller, the small utility, the mid-sized manufacturer, or the hospital whose HVAC, power, and medical-gas systems depend on similar hardware.

Look for valuable physical processes and thin security staffing—accounts where a cyber event can become a property-damage, business interruption, or bodily-injury claim. Ask directly:

  • Do you have a current inventory of your controllers?
  • Which are reachable from outside your network?
  • Who holds the remote-access credentials?
  • When did you last audit those connections?

3. Can we keep up with our own vulnerabilities? Many carriers run legacy policy-administration systems that make Epic's code look young. How fast can we test and deploy fixes without disrupting the business? If we scanned our core systems tomorrow, how many people would we need to fix what we found—and where is that money in the budget?

Keep investing in AI for offense: faster quotes, cheaper claims, sharper underwriting. But a growth strategy that ignores the mounting cost of defense isn't a strategy—it's an unfunded liability.

And remember: Defense wins championships.


Riv Arthur

Profile picture for user RivArthur

Riv Arthur

Riv Arthur is a business leader and technologist working in insurance, healthcare, and private equity.

Finding Value in Today's Volatility

New data sources, better models, scenario planning and faster processing of information can help insurers turn today's "polycrisis" into value for themselves and for customers.

Image
Insurance

I don't know about you, but I'm a bit wary when I pick up my phone first thing in the morning and check on the state of the world. There's rioting where? A convective storm or wildfire destroyed what? The war in Ukraine or Iran took what turn? Inflation was how high, or job growth how low?

And the volatility is building on itself, creating what some of our authors have dubbed the "polycrisis." Economic problems lead to rioting in France, which destabilizes the Western alliance, which emboldens Putin in Ukraine, which feeds the political crisis in the U.S., which....

The insurance industry generally dislikes volatility. Insurers want a decade or two of data on a risk so they can price it properly. But how do you understand risks that appear so suddenly and can interact in such complex ways?

To get a sense, I turned to Dawn Miller, the chief commercial officer at Lloyd's and CEO of Lloyd's Americas, who explained how new data sources, better models, scenario planning and just generally processing information faster can at least help. 

Let's have a look.

Here is the full interview I did with Dawn. And here is a link to this year's Global Insurance Forum, which our sister organization the International Insurance Society is holding at Lloyd's in London on Nov. 15 and 16 on the theme, "Turning Volatility Into Value." But I'll summarize:

Dawn says, "We're seeing innovations in modeling—additional data transparency being plugged into some of those core models that we've always used to look at some known perils. The perils aren't changing, but our ability to understand them is getting better, sometimes dramatically. There's also an opportunity for geopolitical assessments, economic assessments, and social demographic assessments to all play a role."

She adds that some firms like at least some volatility because it creates more potential for upside and "fits as a diversifier into their portfolios. We see others wanting the longer-tail risk. This may not be as volatile, but they want it for their own investment reasons. Our role [at Lloyd's] is to create the environment for all those different profiles to exist and to all benefit from the diversification of our marketplace. It's not an either-or—the alpha seekers or the beta seekers. It's having both in an environment where they can coexist."

Dawn cautions that today's environment is full of "new layers of complexity": "In the past, our market would focus on certain CAT risks, certain natural perils happening in one place at one time. Now we're seeing multiple risks interact at the same time, from natural catastrophes and supply-chain disruption to inflation, geopolitical uncertainty and demographic risks. And those are just to name a few.... It takes an enormous amount of creativity to predict the layers of complexity around us today."

But she's optimistic about the industry's ability to innovate, including through Lloyd's Lab and the Lloyd's Academy, to help the insurance industry react faster as perils develop and interact. She also sees the industry cooperating, including through the ecosystem that Lloyd's fosters:

"Innovation, whether it is the birth of a new product, or the birth of a new structure, or how we deal with some of the extreme large-scale infrastructure, energy, supply chain, and transportation issues that we see around the world—that is going to take more than one mind to solve."

When I wake up tomorrow morning, I'll still peek at my phone with one eye open to check on the state of the world, but all is not lost.

I hope to see you in London so we can discuss the polycrisis and its many implications in person.

Cheers,

Paul


Insurers Overlook Revenue in Existing Client Books

Brokers and carriers are sitting on billions in unwritten premium hidden inside their own books by systems that can't see coverage gaps.

Insurance

Every renewal is a chance to identify a coverage gap. Very few are pursued, as the arithmetic works against a review:

The shared challenge: renewals that don't pay for the conversation

  • North America: 10-15% commission on a $5k-$25k small commercial account leaves a few hundred dollars, about the cost of a client dinner, set against hours of review work.
  • UK, Ireland and Europe: regulatory value-measures data puts commission at roughly GBP 36-50 per account, less than a team lunch. That is the entire budget for the renewal conversation.
  • ANZ: the same thin arithmetic, a flat-white budget against a needs analysis worth of work.

A genuine gap review means pulling the file, benchmarking the exposure, and checking every missing line. That is skilled handler time weighed against lunch-money commission, so the review rarely happens. Cross-sell sits near 15%; around three in four SMEs are underinsured, and premium that should compound goes unwritten.

Why scale hasn't solved it yet

A decade of consolidation has created the largest books the industry has seen. Yet each acquisition also adds another system, another data format, and another partial view of the client. Scale multiplies the latent opportunity while spreading thin the attention available to find it.

Two things make this hard to fix from the inside. The resources best placed to mine a book are the senior handlers running its renewals, and pulling them off client work costs more commission than the hunt is likely to find. And the data usually sits in legacy systems exactly as it was acquired, where cleaning it is a migration project nobody has the capacity to resource.

The result is a familiar pattern: books grow quickly, gaps stay invisible, and growth stays linear when the arithmetic suggests it could compound.

What a better approach looks like

Whether an organization builds, buys, or partners, a few principles tend to separate what works from what stalls:

  • Sit above existing systems. Replacing or migrating legacy platforms is slow and risky. A layer that reads from them is faster to value.
  • Automate the detection, not the relationship. Technology should surface the missing cover, the under-limit, and the unpriced exposure. People should still own the conversation and the decision.
  • Unified client view (Client 360). Gaps become visible only when data from multiple sources is read together, across lines and across acquired books.
  • Add capability without adding headcount. If the fix needs the same scarce people it is meant to free up, it will not scale.
For brokers: One intelligence layer across every book you own

For a broker, the challenge is attention. Thirty acquired books can mean 30 systems and no consolidated client view. The need is an intelligence layer that sits across all of them, reads the data as it stands, and flags where coverage is missing.

Broker IQ is one example of this model. It is an AI-native layer that sits on top of every acquired book, with external partners supplying data, models, and connectors. The broker keeps the client relationship and the decisions. There is no new hiring, no migration, and no re-keying. The aim is simple: make the gap review cheap enough that it happens at every renewal.

For carriers: Seeing the client beyond the agency wall

Small and mid-sized carriers serving the US SME market face a different version of the same problem. They write into a premium pool of $190B or more that is growing faster than any other commercial segment, yet they see only a fraction of what brokers know about a client.

  • Limited visibility. Underwriters see roughly 30% of what brokers know. Exposure, endorsement, and claim signals tend to fade at the agency boundary.
  • Margin pressure. Commercial combined ratios sit above 98%, and loss-cost inflation in commercial auto (+11%) and property (+7%) is outpacing rate.
  • Coverage white space. About 74% of SMEs are underinsured and only around 17% hold cyber cover. That premium is unwritten and largely invisible to carrier systems.
  • Changing distribution. Digital-first and embedded players have gained around 11 points of SME share in five years by owning the customer relationship.

Roughly $118B of that pool flows through brokers, where the information gap is widest. Around $32B is addressable over five years through cross-sell and coverage-gap fill. For a carrier with $1B of direct written premium, that could mean $60-120M of incremental premium.

Agency IQ is one example of how carriers can approach this. It is a client-intelligence layer that brings the broker, policy administration, and third-party data into a single view across six lines, sitting above legacy systems rather than replacing them. Rules and machine learning flag missing coverage and under-limits against peer benchmarks, and advisory packs help turn renewal calls into risk conversations rather than price negotiations.

Modeling points to combined ratio gains of 250-400 bps and a 3-5x lift in cross-sell.

The timing question

Data and AI build costs have fallen by around 80% since 2019. Broker consolidation now concentrates about 54% of premium in the top 10 firms, and cyber and professional-liability cycles are hardening. As costs fall and expectations rise, shared client intelligence is likely to move from differentiator to baseline very soon.

The growth most organizations are looking for is already in the book they own. The question is whether they can see it, and whether economics finally allow them to act on it.