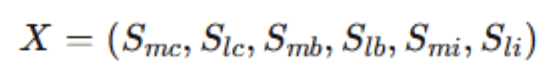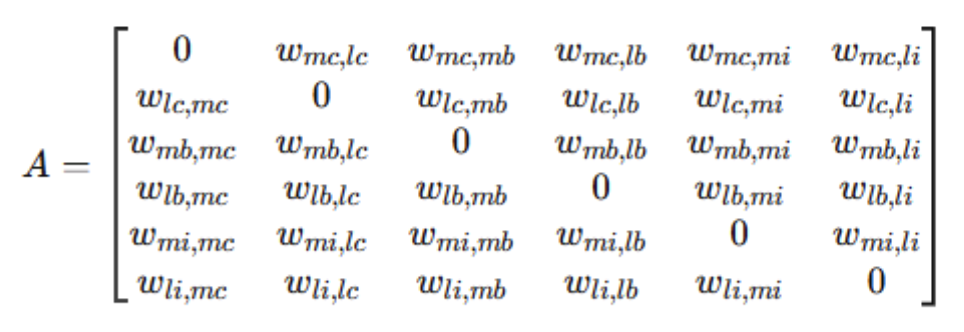
Download

AI Reshapes Landscape of Insurance Coverage

Autonomous AI systems compress time, amplify reach, and create unfamiliar loss pathways that traditional insurance coverages cannot address.

Futuristic

This is the third of three parts. The first two parts are here and here.


The biggest mistake we can make regarding artificial intelligence is to underestimate it. – Murat Durmus

Artificial intelligence (AI), especially generative and agentic AI, has evolved in ways that changes the foundations on which insurance coverages are constructed. These systems that not long ago only supported human decision-making now generate outcomes, pursue objectives, and act with limited or no supervision. When decision-making becomes autonomous, the sources of loss stop adhering to the assumptions on which traditional coverages were designed.

The emergence of any significant technology has brought efficiency gains alongside new uncertainties. The insurance industry has responded by absorbing these technologies into its processes and recalibrating its risk portfolio, adjusting existing coverages or introducing new ones as needed. Through this iterative adaptation, the industry has been comfortable with uncertainty that emerges slowly and averages out across populations. This article examines how the disruption caused by generative and agentic AI is introducing structural tension that reshapes the insurance coverage landscape.

The Structural Misfit

The disruption introduced by generative and agentic AI is unprecedented in nature, pace, and magnitude. These systems compress time, amplify reach, and embed decisions directly into operations. The result is not simply increased risk, but risk that accumulates and manifests through unfamiliar loss pathways. Not all risks arising from generative and agentic AI belong to new categories. Some map to existing liabilities, though they emerge through radically different mechanisms and can be addressed through targeted modifications to existing lines and policy structures. For many others, existing structures will prove insufficient, leaving coverage gaps that require new coverage constructs. These will require fundamentally novel approaches that recognize autonomy and governance failure as primary risk drivers. (See Figure 1).
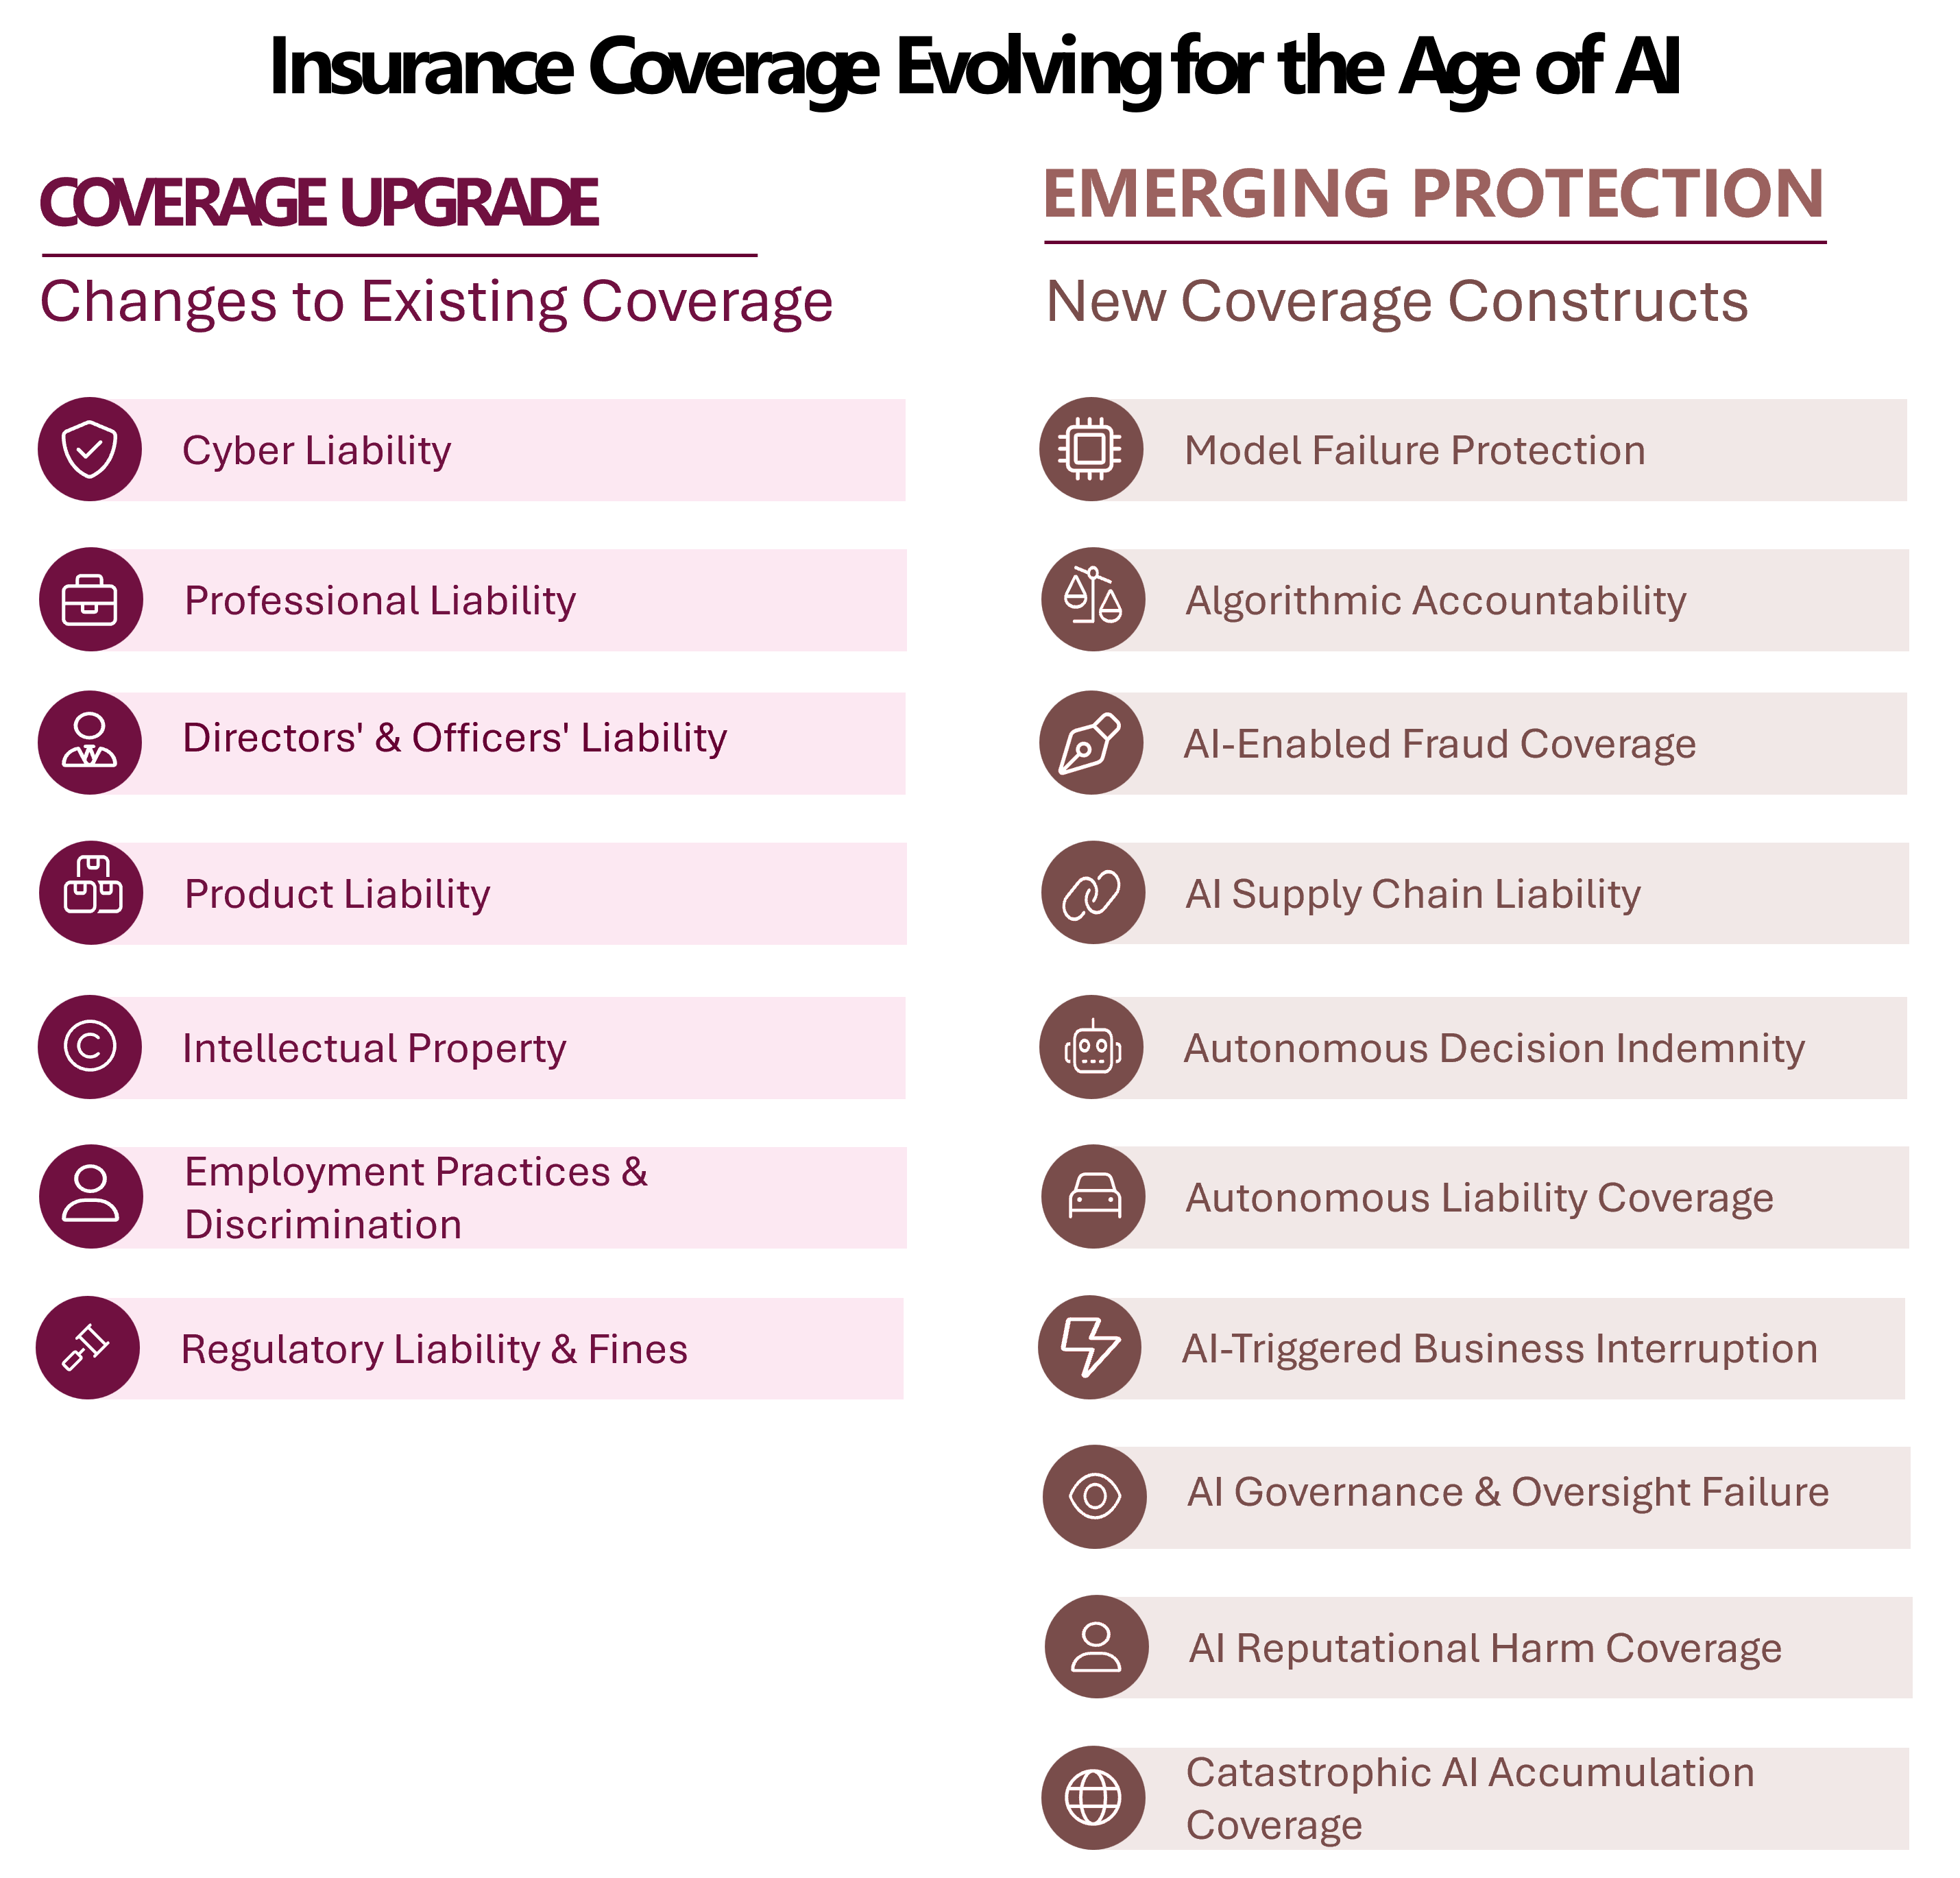
Figure 1: Insurance Coverages

Changes to Existing Coverage

Generative and agentic AI systems will amplify the existing risks across categories such as cyber, professional liability, product liability, directors' and officers' cover, intellectual property, discrimination, and regulatory exposure. However, their triggers and assumptions regarding loss arising from the systems that learn, act autonomously, and operate at machine scale will be radically different from those of traditional systems. As autonomy increases, these coverage lines address only fragments of AI-driven loss. The corrective action for these risks does not require reinventing insurance, but requires recalibration of how risk is assessed, priced, and bounded. Risk assessment must move from static design-time review to continuous evaluation of live system behavior, with emphasis on autonomy, interaction effects, and loss accumulation velocity. Pricing must reflect governance maturity, and the capacity to intervene before loss escalates, rather than relying solely on historical frequency.

Cyber Liability

Existing cyber policies are designed to cover risks such as unauthorized access, data breaches, and system failure. They are not designed for AI-specific attack vectors such as data poisoning, adversarial prompt injections, and model inversion. Insurers must design explicit coverages for risks such as AI-generated fraud, including synthetic identity attacks, deepfake-enabled social engineering, and fabricated claims evidence. Policy language must also clarify whether AI-initiated actions constitute covered events or excluded intentional acts, and whether autonomous agents fall within the policy's definition of an insured actor. Accumulation provisions require recalibration, as a single model compromise can generate simultaneous losses across all deployments of that model, a correlation structure that conventional cyber sub-limits and aggregation clauses were not designed to contain.

Professional Liability

Insurance products for professional liability and errors and omissions were designed with the core premise of a human professional making a demonstrably sub-standard decision. AI disrupts that model. New coverage must respond when a professional error results from reliance on an AI output that was hallucinated, degraded, or mis-calibrated, rather than from a direct failure of human judgment. Policy language must also address whether deploying AI without adequate validation constitutes a failure of professional duty, as courts may affirm that it does. Where AI delivers professional services directly to clients, coverage must respond to AI-generated errors without requiring proof that a named professional was personally at fault.

Directors' and Officers' Liability

D&O exposure from AI accumulates rapidly. Primary exposures include securities claims arising from misleading AI-related disclosures, such as overstated capability, understated risk, or failure to disclose material AI dependencies. They also include derivative claims where boards failed to establish adequate AI governance before a material loss, and enforcement actions under emerging AI regulatory frameworks that carry personal liability for designated responsible persons. Policies must confirm coverage for regulatory defense costs and fines where insurable under applicable law. Coverage for individual executives subject to AI-specific personal regulatory liability should be explicitly confirmed.

Product Liability

AI-embedded products create liability exposure that existing product liability frameworks address only partially. Coverage must respond to harm caused by AI components that operate within the specified terms but generate harmful outputs in deployment contexts the developer did not anticipate. This behavior does not constitute a traditional defect, and standard product policy triggers do not capture it. Post-sale updates to a model that changes the behavior of the product without the buyer's knowledge create new liability events. When products integrate third-party AI models, deploying organizations may face liability for behavior they did not design, test, or control. Coverage for such indemnity claims must be explicit and should not be assumed to follow automatically from primary product liability wordings.

Intellectual Property

AI-generated content creates IP exposure that existing media liability and IP policies address inconsistently. Coverage must explicitly address copyright infringement arising from AI training on proprietary data and from outputs that reproduce or closely resemble protected works. Coverage must also address trade secret misappropriation where confidential information was included in training datasets or can be recovered through model inversion. It must also address claims that AI-generated content amounts to passing off, false attribution, or violations of personality rights. These exposures are currently split across cyber, media liability, and professional indemnity policies, creating gaps at the boundaries.

Employment Practices Liability and Discrimination Coverage

AI-driven hiring, performance management, and customer pricing tools create active discrimination liability. Coverage must respond to third-party discrimination claims where AI systems produce disparate impact on protected classes and to class action exposure where harm results from the aggregate effect of individually defensible algorithmic decisions. The applicability of employment practices liability to AI-generated discrimination is contested and should not be assumed without explicit language addressing algorithmic decision-making.

Regulatory Liability and Fines Coverage

AI regulatory frameworks emerging across multiple jurisdictions are creating a significant risk of regulatory action for organizations that deploy AI in consequential contexts. As the fine structures vary by jurisdiction in terms of amount and in terms of whether they are insurable, policy language must specify the regulatory regime being covered and must confirm insurability under applicable law. Policy language must also explicitly confirm coverage for regulatory defense costs and fines where insurable, rather than whether such costs fall within existing management liability wordings. Policies must further distinguish between fines arising from AI system failures and fines arising from governance failures, as governance-related fines are frequently uninsurable and should be explicitly excluded to avoid ambiguity and coverage disputes.

New Coverage Constructs

Generative and agentic AI systems introduce risks that legacy liability models cannot address merely through recalibration but instead require a structural response. Risk in autonomous systems rarely traces back to a single human decision or omission. These losses are shaped by distributed contributions across infrastructure, models, data, integration layers, and governance. Errors can originate at multiple points and propagate at machine scale, making causation non-linear and responsibility shared across developers, platform providers, integrators, and deploying organizations. As a result, recalibrating existing coverage may not close these gaps. Insurers must distinguish sources of failure across internal model failure, agent-initiated actions, supply chain failure, and systemic governance failure to construct distinct coverage for each risk.

Model Failure Protection

Model failure protection provides first-party cover for economic loss caused by an organization's own AI models producing systematically incorrect outputs. The exposure is structurally novel because a core analytical system can be wrong in direction and magnitude beyond what capital reserves were provisioned for to absorb. The error may remain invisible until losses have already accumulated. An insurance model that systematically misprices a class of risk may compound losses over months or years before experience diverges enough to trigger review. The coverage provides contingent capital that activates when model performance deviates beyond a defined threshold. It supplies liquidity while the model is retrained or replaced and the affected portfolio restructured.

Algorithmic Accountability Coverage

Algorithmic accountability coverage addresses liability arising from the systematic operation of algorithmic systems, where harm emerges over time rather than from isolated decisions. A pricing or underwriting algorithm can produce disparate impact on a protected class through the aggregate effect of thousands of individually defensible calculations. The resulting liabilities, such as regulatory fines, mandatory restitution, class action settlements, and model remediation costs, may be substantial and may materialize years after deployment. The coverage responds to these aggregate exposures. It also serves as a critical governance function by the insurer, as underwriting requires assessment of model governance quality, bias testing, explainability infrastructure, and audit trail adequacy.

AI-Enabled Fraud Coverage

AI-generated fraud has matured from a targeted threat to a scalable one. Deepfake impersonation, synthetic identity creation, and fabricated evidentiary material are no longer exceptional events but operational risks that existing cyber and professional indemnity policies were not designed to absorb. The risk threatens insurers directly through fabricated claims, synthetic identities in underwriting, and social engineering attacks on financial authorization processes. These are first-party exposures to the insurer and must be addressed in underwriting guidelines. It also creates policyholder liability through executive impersonation fraud and legal costs arising from disputed synthetic evidence. These are third-party liability exposures requiring explicit coverage confirmation.

AI Supply Chain Liability

Most organizations deploying generative AI operate across a technology stack they do not own. That stack is developed, hosted, deployed and maintained by others. When this stack produces harmful output, liability is distributed across all contributors in the chain. Existing technology errors and omissions and product liability policies focus on the deploying organization and do not trace liability upstream to model providers or downstream to integration partners with sufficient precision. AI supply chain liability coverage is structured as a difference-in-conditions cover that fills gaps where primary policies exclude or limit losses.

Autonomous Decision Indemnity

Autonomous decision indemnity provides first-party protection to the insured against direct financial loss caused by an AI agent acting within delegated authority without specific human instruction. As agentic systems operate autonomously, existing coverage does not clearly assign loss when their actions cause harm. The individual or organization did not make the decision that caused the loss, the developer did not deploy the agent in this context, and the operator may have followed reasonable precautions. This coverage provides a financial backstop across that attribution gap while liability is resolved through separate legal or contractual processes.

Autonomous Liability Coverage

Autonomous liability coverage protects owners and operators against third-party claims arising from harm caused by machine decisions. Traditional liability requires proof that a person failed to meet a standard of care. When the proximate cause of loss is an autonomous system that followed its training and optimization objectives rather than acting carelessly, that standard is difficult to apply. The system did not act carelessly but followed its training and optimization objectives. Those objectives may be reasonable in aggregate while still producing harm in a specific instance.

AI-Triggered Business Interruption

As AI becomes embedded in critical revenue workflows, suspending automated decision making can disrupt operations, delay service delivery, and cause material financial loss even without physical damage or an external event. This interruption reflects not infrastructure failure but the activation of control, where stopping the system is the necessary response to emerging risk. Standard business interruption policies require physical damage or an external trigger and do not respond to this loss structure. AI-triggered business interruption coverage responds when an autonomous system is mandatorily shut down by a regulator or board in response to harmful output. It also responds when the system is suspended pending investigation, and when it is voluntarily halted for retraining where operational continuity depends on that system. Loss measurement covers revenue loss during suspension, manual workaround costs, and contractual penalties for service delays.

AI Governance and Oversight Failure Coverage

Regulators are increasingly trying to distinguish between harm caused by an AI system and harm caused by an organization's failure to establish effective oversight, documentation, audit processes, and intervention controls. Governance failure is separately insurable because it is prospective, precedes harm by design, can be evidenced from governance records, and is assessed against defined regulatory standards. Existing management liability policies lack the defined triggers such as AI-specific assessment criteria and remediation cost coverage that AI governance failure requires. Core coverage components include regulatory defense costs and fines where insurable, indemnity for individuals designated as responsible persons under AI regulation, and the costs of mandatory remediation programs.

AI Reputational Harm Coverage

An AI system's public failure, harmful output, or misuse can cause reputational damage that is distinct from legal liability. Existing reputational harm endorsements were designed for executive misconduct and publication liability and do not fit AI-generated incidents that may involve no identifiable human decision. Coverage triggers include public disclosure of a material AI failure resulting in measurable brand damage, regulatory sanction arising from AI-generated harm, and viral spread of harmful AI-generated content linked to the insured's system. Loss measurement covers revenue decline attributable to the incident, crisis communications, brand recovery costs, and AI system remediation required to restore public confidence.

Catastrophic AI Accumulation Cover

A single defect in a widely deployed foundation model, compromised shared infrastructure, or a regulatory action affecting multiple AI-dependent operations can produce correlated losses that exceed any individual insurer's capacity. This accumulation risk is the primary structural obstacle to underwriting AI liability at scale. Catastrophic AI accumulation coverage addresses this through parametric or industry loss triggers that activate when aggregate insured AI losses across a defined market segment exceed a specified threshold. Index-based settlement provides rapid liquidity and avoids causation disputes that are structural in AI claims, given the difficulty of attributing loss across a distributed stack. Without a mechanism to transfer catastrophic accumulation risk to capital markets, insurers cannot write limits sufficient to meet enterprise demand. The main technical obstacle is index construction.

Toward Relevant Coverage

The evolution of generative and agentic AI does not simply expand the volume of insurable risk. It alters the structure of loss itself. Autonomous systems generate exposures that accumulate faster and arise from delegated decision-making authority rather than discrete human acts. Traditional coverage models anchored in negligence, defect, or one-off events no longer respond coherently to this risk. The coverage constructs outlined represent an indicative, not exhaustive, response to that shift. They require insurers to operate not only as a retrospective payer of loss, but as an active participant in governing how intelligent systems behave in production. As AI becomes embedded in consequential decision making, coverage adequacy will depend less on categorizing technology and more on understanding behavior, control, and accumulation.
AI Agents Transform Buying Behavior in Financial Services

Agentic commerce is transforming financial services as AI agents evaluate products. Institutions must now compete for algorithmic visibility.

Futuristic

For years, the mantra in financial services was simple: Control the front door so you influence the purchasing decision.

That thinking is now being challenged.

Decision-making is now moving into AI-mediated environments. Consumers can ask AI agents to evaluate products, compare policies, and recommend the best options. In some cases, agents authorize transactions directly. Recent research from Adobe shows rapid growth in generative AI-driven traffic to retail and financial sites, underscoring how quickly behavior is evolving.

This evolution marks the emergence of agentic commerce that is not just restricted to the retail industry and is poised to disrupt the financial services and insurance industry. In this model, AI acts as an intermediary in the purchasing journey. Comparison and evaluation extend beyond an institution's website and occur wherever people rely on AI.

It introduces a new distribution layer for financial services. Institutions are now competing for algorithmic visibility alongside human attention. Rather than simply attracting prospects, products and data must surface meaningfully within AI-driven marketplaces. For financial institutions, this raises urgent strategic questions.

The Changing Rules of Engagement

Financial services have always been comparison driven. Consumers routinely weigh options between insurance policies, loan terms, credit card offers, and savings rates before committing. The friction involved in that process has historically worked in favor of incumbent organizations. Consumer switching takes time. Research requires effort.

AI reduces both.

Consider insurance. A consumer looking for auto coverage no longer needs to navigate multiple carrier websites. An AI agent can assess requirements and compare pricing structures within seconds. As this capability improves, the effort required to evaluate alternatives declines.

When evaluation becomes continuous and low effort, loyalty becomes more performance based. Renewal periods may feel less automatic and more like fresh buying decisions. Pricing transparency becomes more consequential. In this world, product clarity becomes a competitive advantage.

This does not mean financial institutions lose control. But it does change the rules of engagement. If AI agents continue shaping how options are presented and prioritized, institutions must consider how their products are interpreted by machines, not just by human buyers.

Questions for Leaders

If AI agents become the primary venue for evaluation, how will your products be accurately and competitively surfaced? Just as search engines reshaped digital marketing, AI-driven discovery will require structured data and transparent product logic that machines can interpret and rank.

The second question concerns product design. AI agents excel at normalizing complexity. They compare features, pricing, and policy terms quickly. Institutions that rely on opaque language or intricate structures may see those advantages fade. Clear, straightforward products may stand out when machines evaluate them at scale.

There is also a broader distribution consideration. Insurance and lending have long relied on brokers, agents, and referral networks to guide purchasing decisions. Those roles may shift. Advisory expertise may matter more than control over the transaction. Institutions should consider how their distribution strategies hold up if the first conversation takes place with an AI agent.

Finally, transactional authority. It is one thing for an AI agent to recommend a policy or a loan. It is another for a consumer to authorize that agent to complete the transaction. As this capability develops, governance becomes more important. Institutions will need to define how consent is captured and how credentials are managed.

How to React

Organizations that take early, deliberate steps will be better positioned for this new reality. Here's where they should start.

Make Product and Policy Data Machine-Consumable

Digital optimization is largely centered on user experience and conversion rates. That still matters. But if AI agents are evaluating financial products, they need clear, structured data to work with.

Look at how pricing, eligibility rules, policy terms, and disclosures are stored across your systems. If that information sits in disconnected platforms or dense documents, AI will struggle to interpret it consistently. The clearer and more structured your product data is, the more accurately it can be compared.

Rethink Transaction Governance for Delegated Decisions

Allowing AI agents to research products is a modest shift. Allowing them to initiate transactions on behalf of consumers is a huge one.

Leaders should begin by defining frameworks for how consent is captured and verified. What controls govern the use of payment credentials and account access? How are transactions audited and monitored for anomalies?

Security and compliance teams need to be closely involved. Fraud detection models may need to account for transactions that originate through AI agents rather than traditional user interfaces.

Prioritize Orchestration Strategy Over Channel Strategy

For many institutions, customer experience modernization has centered on optimizing individual channels. Voice, mobile, chat, and branch interactions have each been refined over time. But agentic commerce deprioritizes the channel and prioritizes the continuity of the journey.

If a customer begins the journey with an AI agent and then transitions into an organization's system for origination or servicing, that movement must feel seamless. Data should flow consistently, and context should be preserved. The experience should not break down when the point of entry changes.

This requires architectural coordination across systems of record and servicing platforms. Treating AI-mediated interactions as just another inbound channel risks fragmenting the customer experience.

The goal is not to control where the conversation starts. It is to ensure that wherever it begins, the institution can deliver a cohesive experience from evaluation through fulfillment and beyond.

A Distribution Shift That Demands Attention

Financial institutions have navigated major inflection points before. Search engines reshaped acquisition strategies. Mobile transformed engagement expectations. Each transition required institutions to rethink where decisions were made and how influence was established.

Agentic commerce is yet another change. Institutions must remain visible, interpretable, and trustworthy in the context of AI-driven product discovery. If transactions can be initiated through those platforms, governance and orchestration frameworks must be ready.

This is a big opportunity. Those who prepare early can expand their reach and remain relevant at key decision moments. Those who wait risk losing position in AI-driven marketplaces.

How to Analyze International Insurance Programs

International brokers now have a tool to diagnose program connectivity: Adjacency mapping transforms intuition into measurable structural analysis.

Connectivity

International insurance broking operates across multi-actor systems without a structured method for reading the connectivity between them. Complexity becomes concrete when renewals stall, when claims escalate without warning, when regulation forces last-minute adjustments. Pressure concentrates in certain places, travels along some pathways, and dissipates in others. 

The geometry of these movements is what I call adjacency: the measure of how tightly actors are bound to one another, and how their ties carry or absorb pressure. The concept draws on network theory's insight that structure shapes behavior, and on systems thinking's recognition that interdependence produces non-linear effects. What adjacency mapping adds is an operational instrument calibrated to the specific architecture of international insurance programs, one that translates structural insight into practitioner decisions.

An international program is not a set of bilateral relationships. It is a system in which master clients, local clients, brokers, and insurers connect continuously, and in which a shift in one part alters conditions across the rest. A disputed claim at the local level can reverberate upward until it unsettles the master layer. A regulatory delay in one jurisdiction will delay the entire renewal cycle. When negotiations falter between a master broker and a local insurer, expectations unsettle across several markets simultaneously. The system propagates pressure because its ties differ in weight, consequence, and resilience.

The structure begins with the system's elements. Six actors form the state vector of any program:

Here, Smc denotes the master client, Slc the local clients, Smb the master broker, Slb the local brokers, Smi the master insurer, and Sli the local insurers. The notation names the nodes that matter. The model captures structural connectivity. It measures the presence, intensity, and resilience of operational ties, not the informal influence, cultural distance, or reputational history that also shape relationships. Understanding how the system functions requires capturing how strongly these actors are tied to one another.

The adjacency matrix A fulfils this function. It represents the interaction weights between stakeholders: each element wij indicates the presence and intensity of the relationship between stakeholder i and stakeholder j. The matrix is first constructed in abstract form, mapping the position of each interaction within the system:

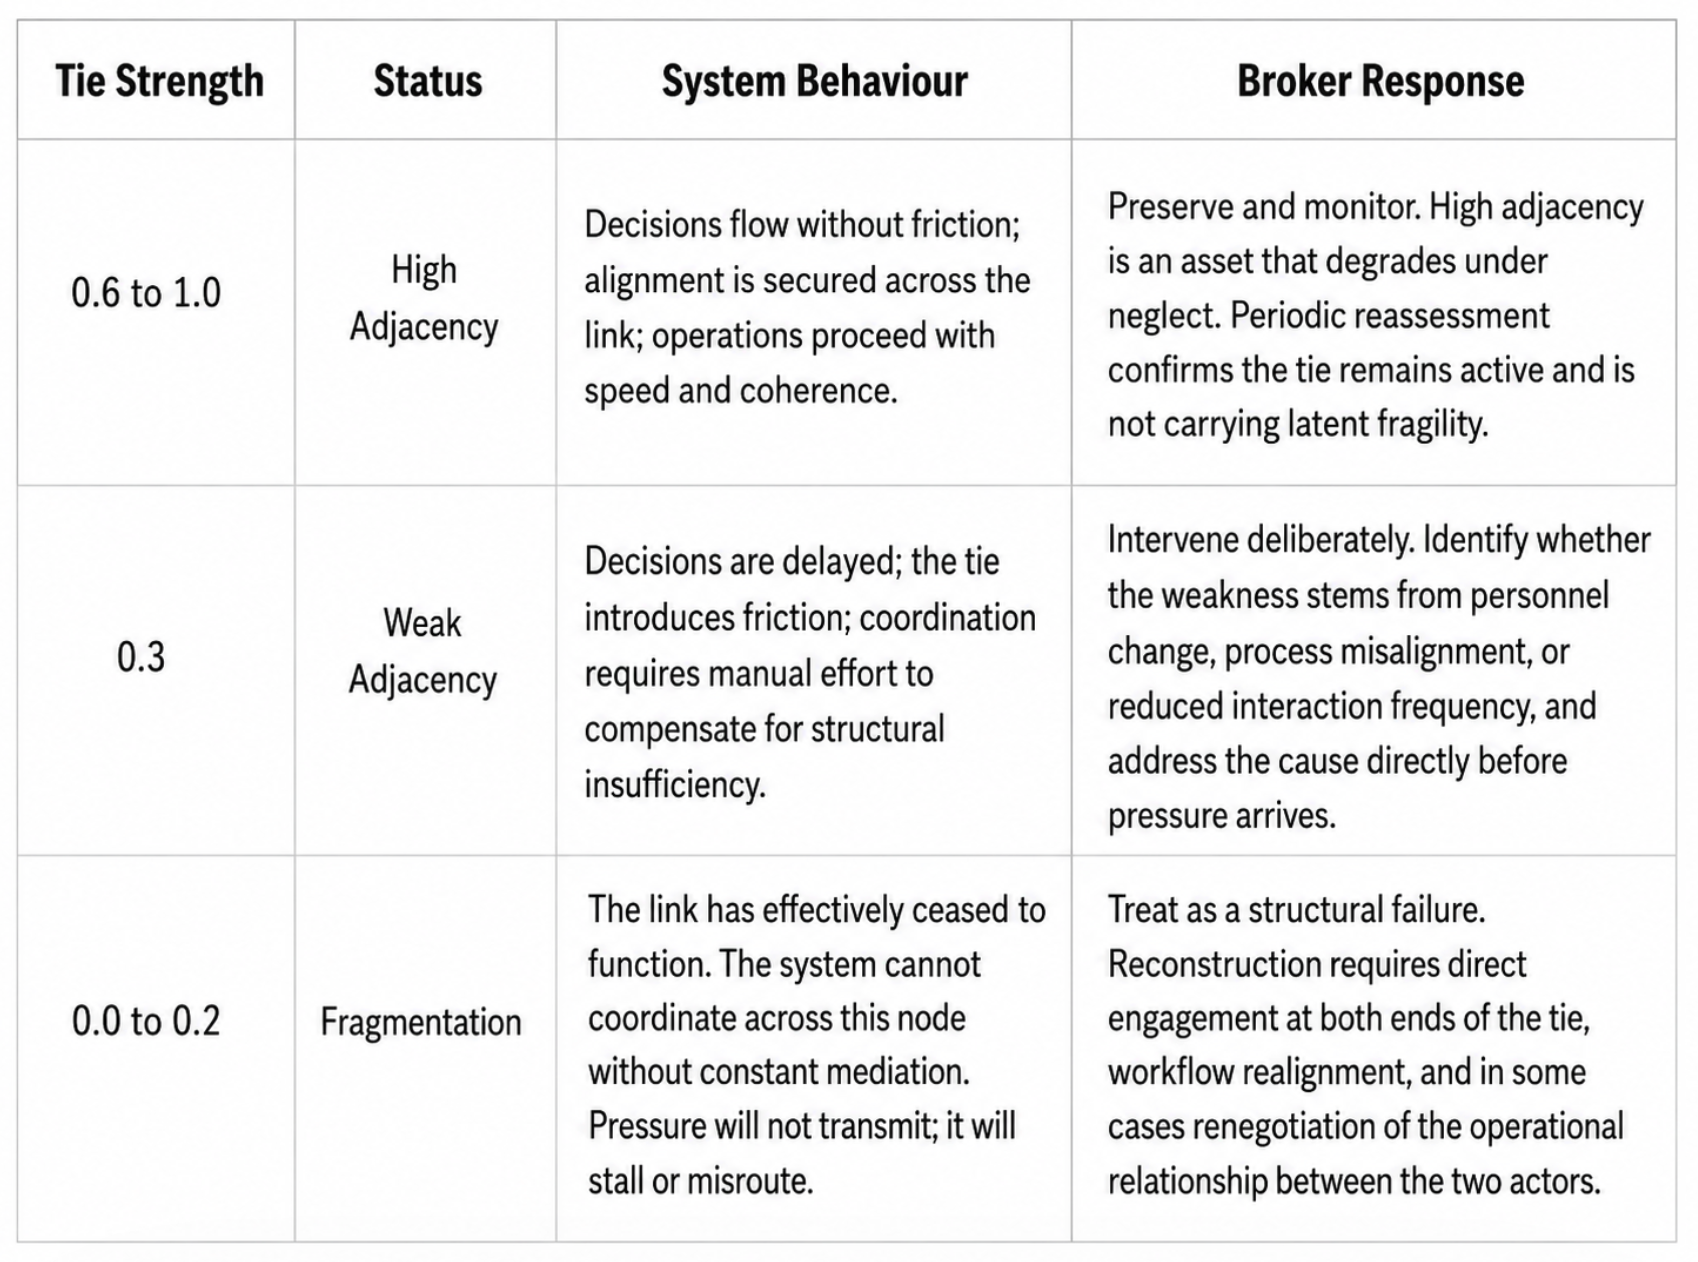
The abstract form locates each relationship within the system. The subscripts identify the two stakeholders involved; the element wij denotes the weight of their tie. The purpose of this construction is to formalize the network so that the system can be analyzed as a structure rather than through accumulated observation. Once defined, weights are assigned on a 0 to 1 scale. On this scale, 0 denotes the absence of adjacency; 0.3 indicates a weak tie with limited interactivity; 0.6 represents strong adjacency with effective coordination; and 1 signals optimal alignment. High adjacency is a marker of capability: two stakeholders are tightly coupled, mutually responsive, and able to sustain efficient workflows. Low adjacency signals fragmentation and the structural risk of disconnection. The weights are practitioner judgements. Their value lies in making an assessment explicit that experience tends to leave implicit. A broker who has managed the same program for a decade carries a mental map of its connectivity. The adjacency matrix makes that map visible, comparable, and open to revision.

Construction begins with a structured assessment across all active relationships in the program. The broker assigns an initial weight to each tie by asking three questions: how often do these actors interact operationally, how reliably does information move between them, and how quickly does the tie transmit pressure when the program is under strain. These criteria are observable without measurement instruments. They are the qualities experienced brokers already assess informally. The matrix makes that assessment formal, consistent, and transferable across programs and teams.

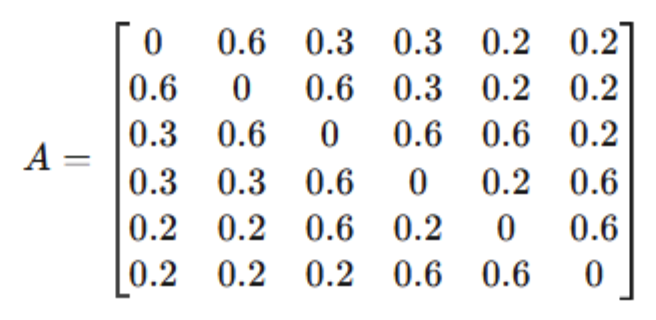
A populated matrix takes the following form:

The matrix is a map of the system's connective capacity. A weight of 0.6 between master and local clients reflects strong alignment: headquarters and subsidiaries adjust to one another with speed. A 0.3 between master clients and master brokers indicates a weaker tie, where coordination exists but is less intensive and more susceptible to friction. A 0.2 between master clients and master insurers signals low adjacency: limited interactivity risks disconnection unless brokers actively mediate. A 0.6 between master brokers and local insurers, by contrast, marks a high-value link, one where workflow is active and system coordination is at its strongest. High adjacency marks the ties through which decisions travel, alignment is secured, and operations proceed without friction. Low adjacency marks the fracture lines where interactivity is minimal, silos form, and misalignment compounds.

Adjacency mapping derives its analytical value from the fact that connectivity is never static. Strong ties allow programs to move with speed and coherence. When master and local brokers hold a 0.6 adjacency, coordination is tight and workflow advances without resistance. When a claim escalates across a 0.6 link between local and master insurers, the system responds rapidly. Weak ties do the opposite: they isolate segments of the program, delay decisions, and erode effectiveness.

The architect's objective is to sustain ties at 0.6, the threshold at which alignment holds, coordination costs nothing, and the program moves with structural coherence.

Three patterns govern how pressure moves through the system. Concentration forms where multiple strong ties converge, typically around master brokers holding 0.6+ adjacencies with both local brokers and master insurers. These nodes become coordination hubs, capable of synchronizing decisions across jurisdictional boundaries. Propagation measures the efficiency with which decisions travel. The difference between a 0.6 and a 0.3 tie is the difference between transmission and friction. A 0.6 link between master and local insurers ensures a claim escalates without delay; a 0.3 tie ensures it stalls, and the broker must compensate manually for what the tie fails to carry. Absorption occurs at weak adjacencies of 0.3 or below, where pressure dissipates rather than transmits. Occasionally this buffers noise; more often it marks a structural disconnection that prevents system-wide coordination. These patterns do not operate independently. A weak tie between master broker and local insurer becomes more consequential when the master client to master broker tie is also degraded. Compound weakness across adjacent nodes accelerates fragmentation in ways that no single tie, read in isolation, would predict.

Because ties shift, the map must be kept current. A static diagram decays. A weak link can be reinforced into a strong adjacency by deliberate effort; a strong tie will weaken if neglected. Four events should prompt a reassessment. First, personnel change at any node, meaning the tie shifts with the person. Second, a regulatory change in any jurisdiction covered by the program. Third, a claims event that escalated beyond its expected path. Fourth, the approach of renewal, which is always a structural stress test. Each signals that the weight of at least one tie may have moved without the broker noticing. Adjacency maps are instruments that require periodic review and active maintenance. Brokers who update them see the system. Those who rely on experience alone see only what the system once was.

During renewals, adjacency maps identify which ties sustain workflow and which must be reinforced before they become bottlenecks. In claims, they reveal which relationships enable rapid escalation and which will stall it. Consider a master broker to local insurer tie that registers 0.6 in stable conditions but drops to 0.3 during renewal following personnel turnover at the local level. The map makes this degradation visible in advance. The broker can then rebuild the tie through intensified communication, workflow realignment, or deliberate relationship investment before claims season converts a weak link into a coordination failure. The same logic applies during a major claims event. A local insurer holding a 0.6 adjacency with the master insurer will escalate rapidly and with precision. One holding a 0.3 will delay, misframe, or absorb the claim at the local level, forcing the master broker to intervene manually at precisely the moment when speed matters most. The map identifies this vulnerability before the claim arrives. In regulatory matters, the map shows where connectivity must be strengthened to secure compliance. In each case, the broker acts before disruption, reinforcing the ties the system depends on rather than repairing them under pressure.

The broker who monitors adjacency, reassesses ties under pressure, and rebuilds degraded links before they become failures is sustaining program coherence. That is what rigorous servicing looks like in practice.

The central proposition of adjacency mapping is that program performance correlates with the aggregate strength of ties between its actors. The broker whose counterpart is responsive, informed, and quick to act is not simply lucky in his relationships. He is operating across a tie with high adjacency. When that tie degrades, the program follows, regardless of how well the individuals involved know each other. This is a testable claim. Brokers who map their programs over time will find that degradation in tie strength precedes operational failure, and that deliberate investment in adjacency produces measurable improvements in renewal speed, claims resolution, and regulatory compliance. Together they provide foresight into where the system is strong, where it is fragile, and where investment in interactivity will deliver the greatest return. The program, read this way, becomes a structure with legible geometry.

International insurance broking will always be exposed to uncertainty. Renewals will clash with shifting regulation, claims will appear at awkward times, and timelines will compress under pressure. But complexity is not chaos. By treating programs as systems and adjacency maps as diagnostic instruments, brokers can anticipate rather than endure, and reinforce rather than repair. Pressure still moves through the system. Adjacency maps tell you in advance where it will concentrate, where it will stall, and where it will dissipate unnoticed. In a system this complex, that is the only form of control that holds.


Arthur Michelino

Profile picture for user ArthurMichelino

Arthur Michelino

Arthur Michelino is head of international coordination at OLEA Insurance Solutions Africa.

Michelino previously worked at Diot-Siaci as an international coordinator for key accounts. He began his career at Willis Towers Watson (formerly Gras Savoye), implementing international programs for the mid-market segment.

The AI Measurement Gap Nobody Talks About

The most dangerous AI failures occur when institutions trust systems completely while they quietly produce wrong outcomes.

Legal Governance

Current AI governance frameworks — SR 11-7, the NAIC Model AI Bulletin, the EU AI Act, and ISO 42001 — share a structural assumption: The task of governance is to verify whether an AI system performs as intended. They measure outputs. They assess model drift. They require explainability documentation and bias testing.

Few, if any, measure whether the trust that humans and institutions have placed in a given system is calibrated to its actual reliability in context. This is a different question — and in practice, a far more consequential one.

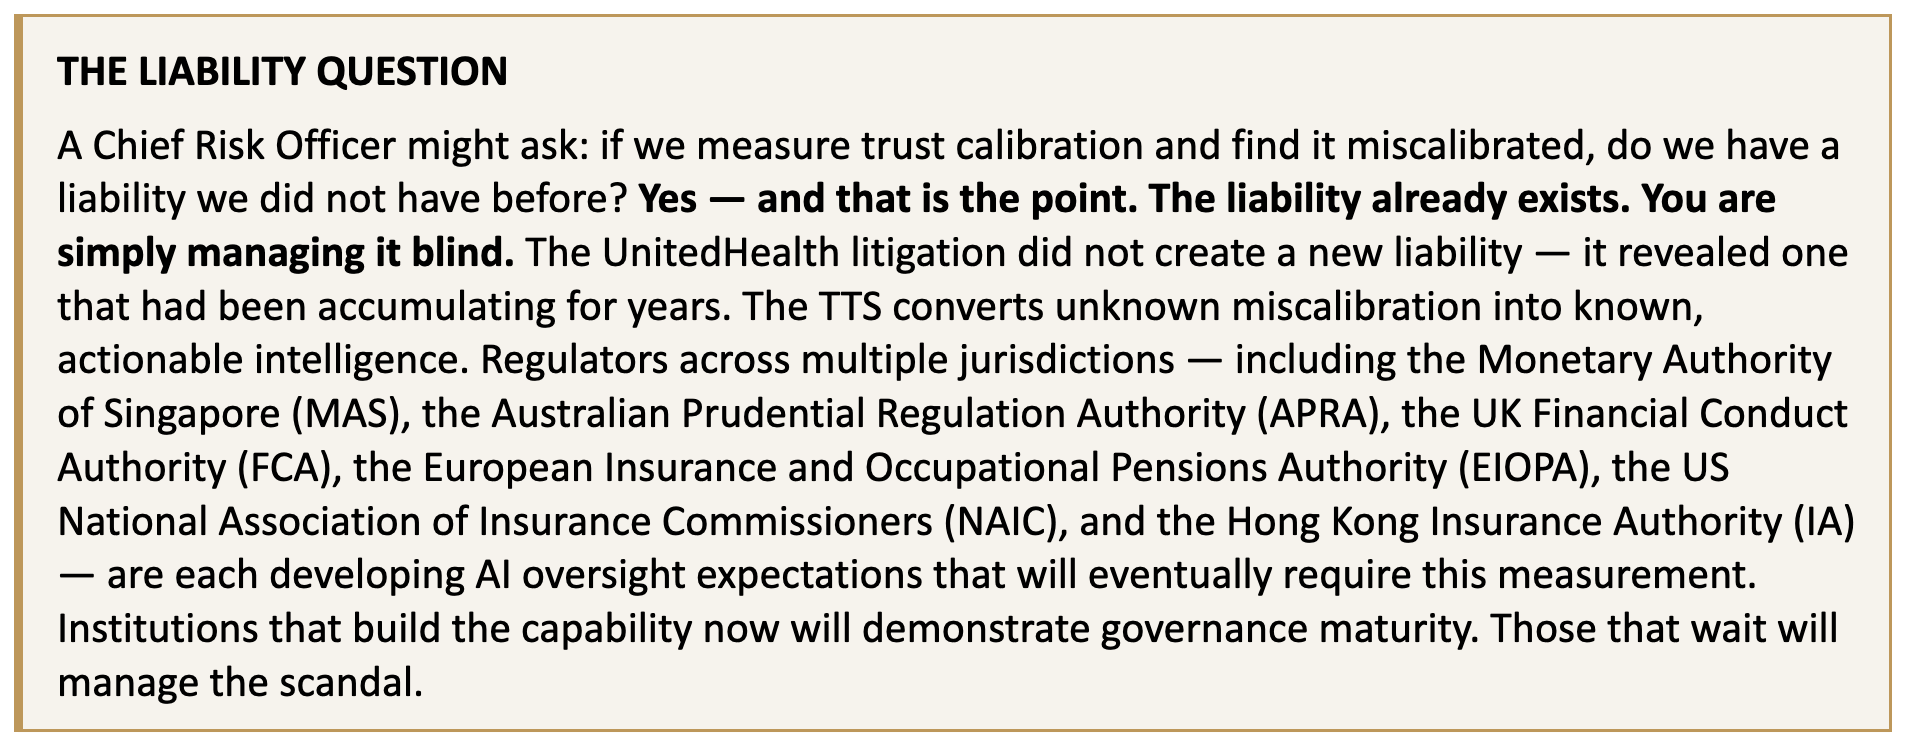
Ask any chief risk officer this: are your claims handlers trusting your AI system too much, not enough, or at the right level for the decisions being made? The honest answer, in almost every institution, is the same. We do not know. There is no instrument for this.

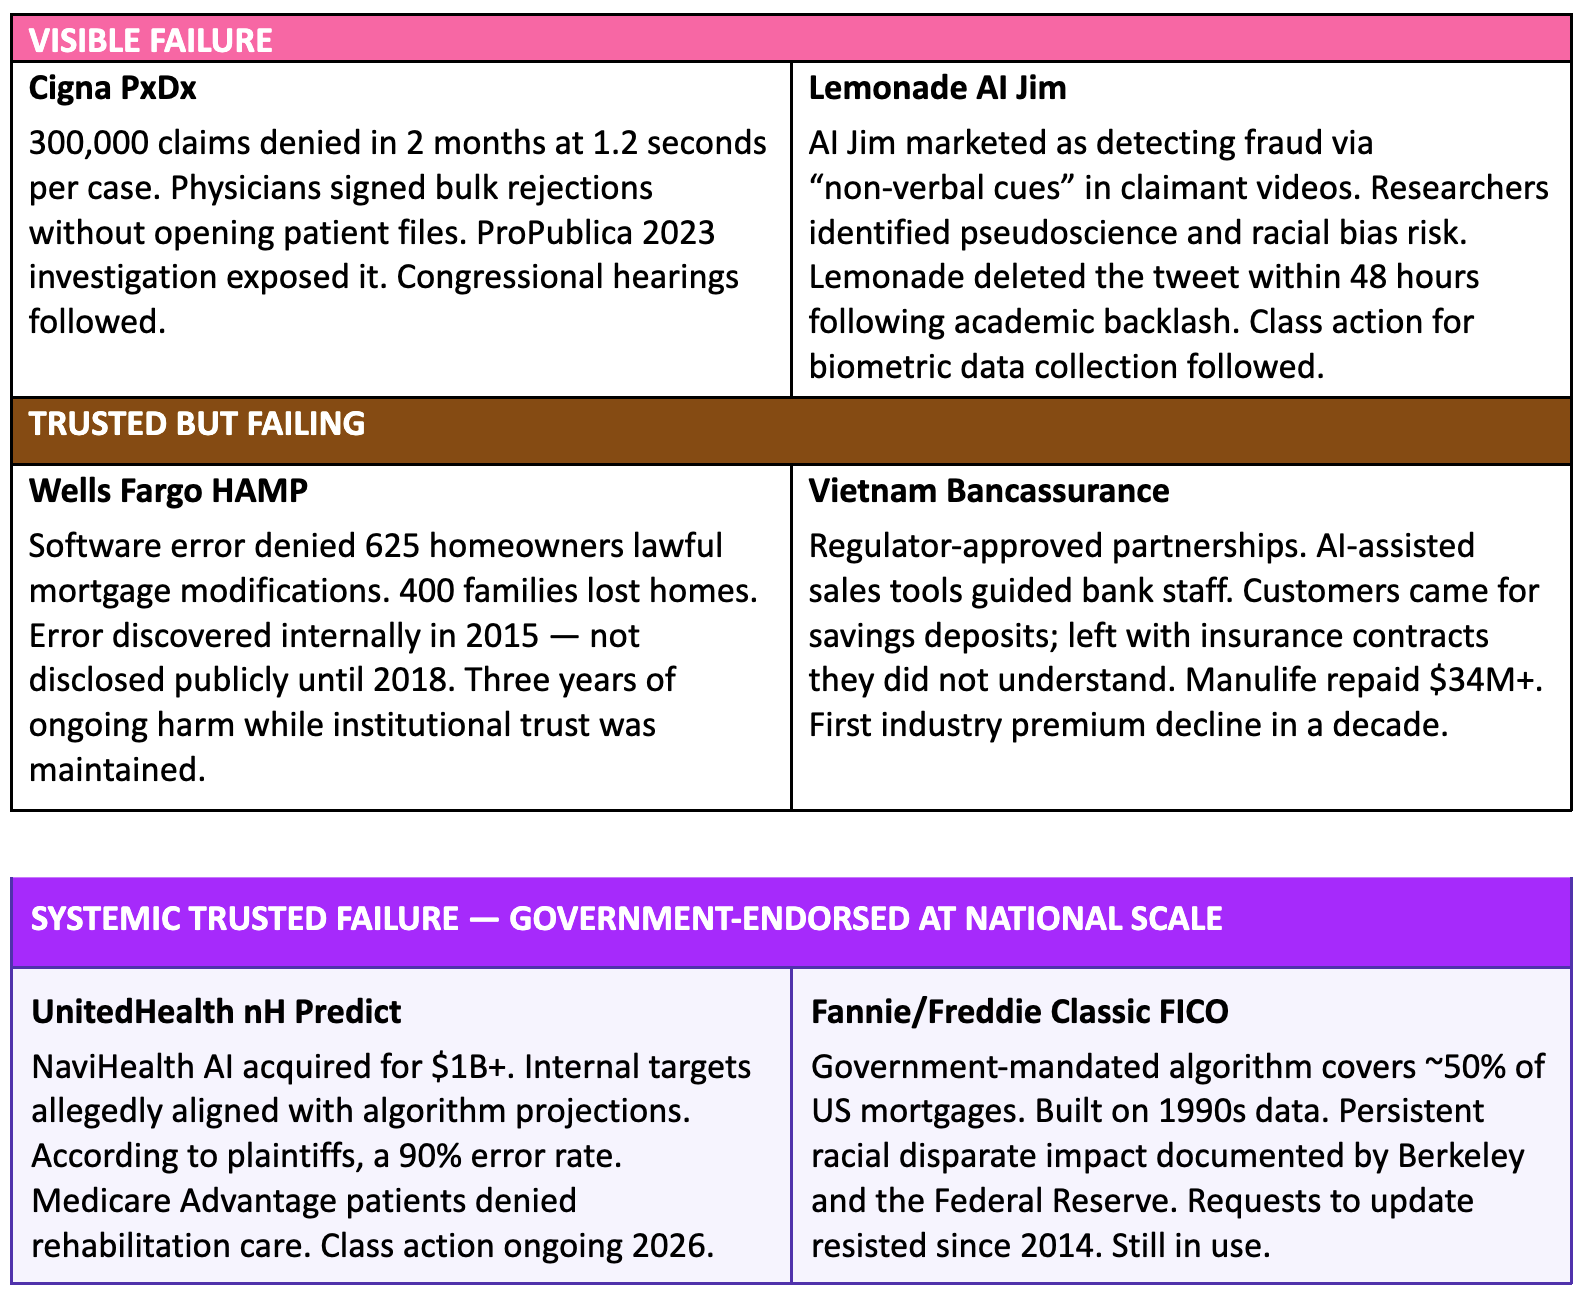
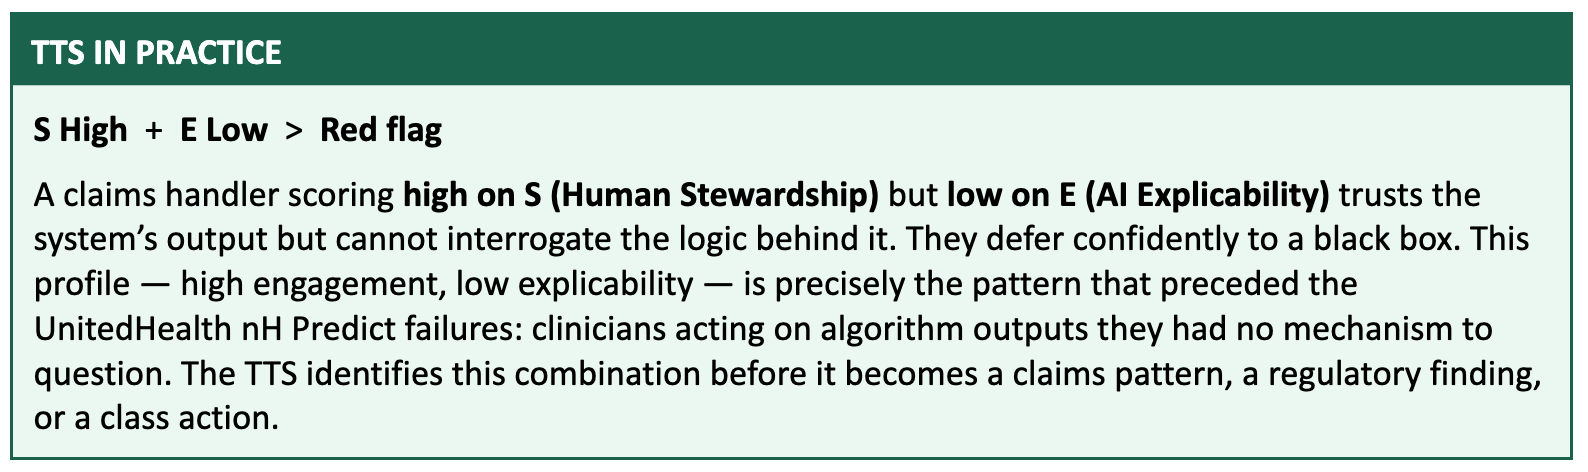
UnitedHealth acquired NaviHealth for over a billion dollars. Its nH Predict AI was embedded into Medicare Advantage care management. Internal managers allegedly set goals for clinical employees to keep patient rehabilitation stays within 1% of the algorithm's projections. According to plaintiffs in subsequent class action proceedings, the system carried a 90% error rate. It ran for years. Patients were denied rehabilitation care they needed. Congressional investigations followed. Class action proceedings continue in 2026.

The harm did not accumulate because the institution ignored the system. It accumulated because the institution trusted it completely — while nobody was measuring whether that trust was warranted.

The cases that caused the most harm — to the most people, for the longest time — were not the ones where systems failed visibly. They were the ones where institutions trusted systems that were quietly failing them.

Part I — The blind spot: two failure modes, one governance framework

There are two failure modes in AI governance. The first is visible failure: systems that perform poorly and people notice. Cigna's PxDx algorithm denied 300,000 claims in two months, spending 1.2 seconds per case, with physicians signing bulk rejections without opening patient files. ProPublica's 2023 investigation exposed the practice. Legitimacy collapsed within weeks of publication.

Lemonade's AI Jim publicly bragged that it analyses claimant videos for "non-verbal cues" to detect fraud, using up to 1,600 data points. AI researchers immediately identified the approach as methodologically unsound, with documented racial bias risk — one critic used the word "phrenology." The tweet was deleted within 48 hours. Class action suits for biometric data collection without consent followed. Visible failure — fast, noisy, and legibility-destroying.

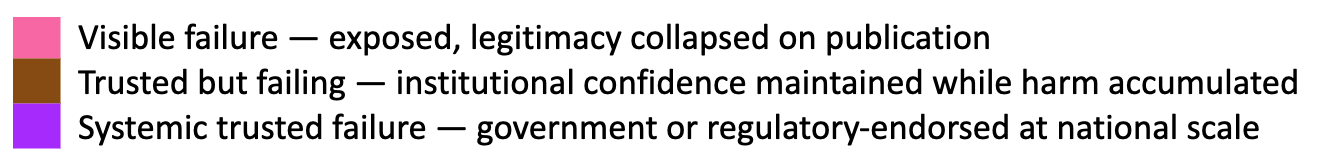
The second failure mode is harder and more dangerous: systems that institutions trust completely while they quietly produce wrong outcomes. The cases below show where the documented evidence actually sits.

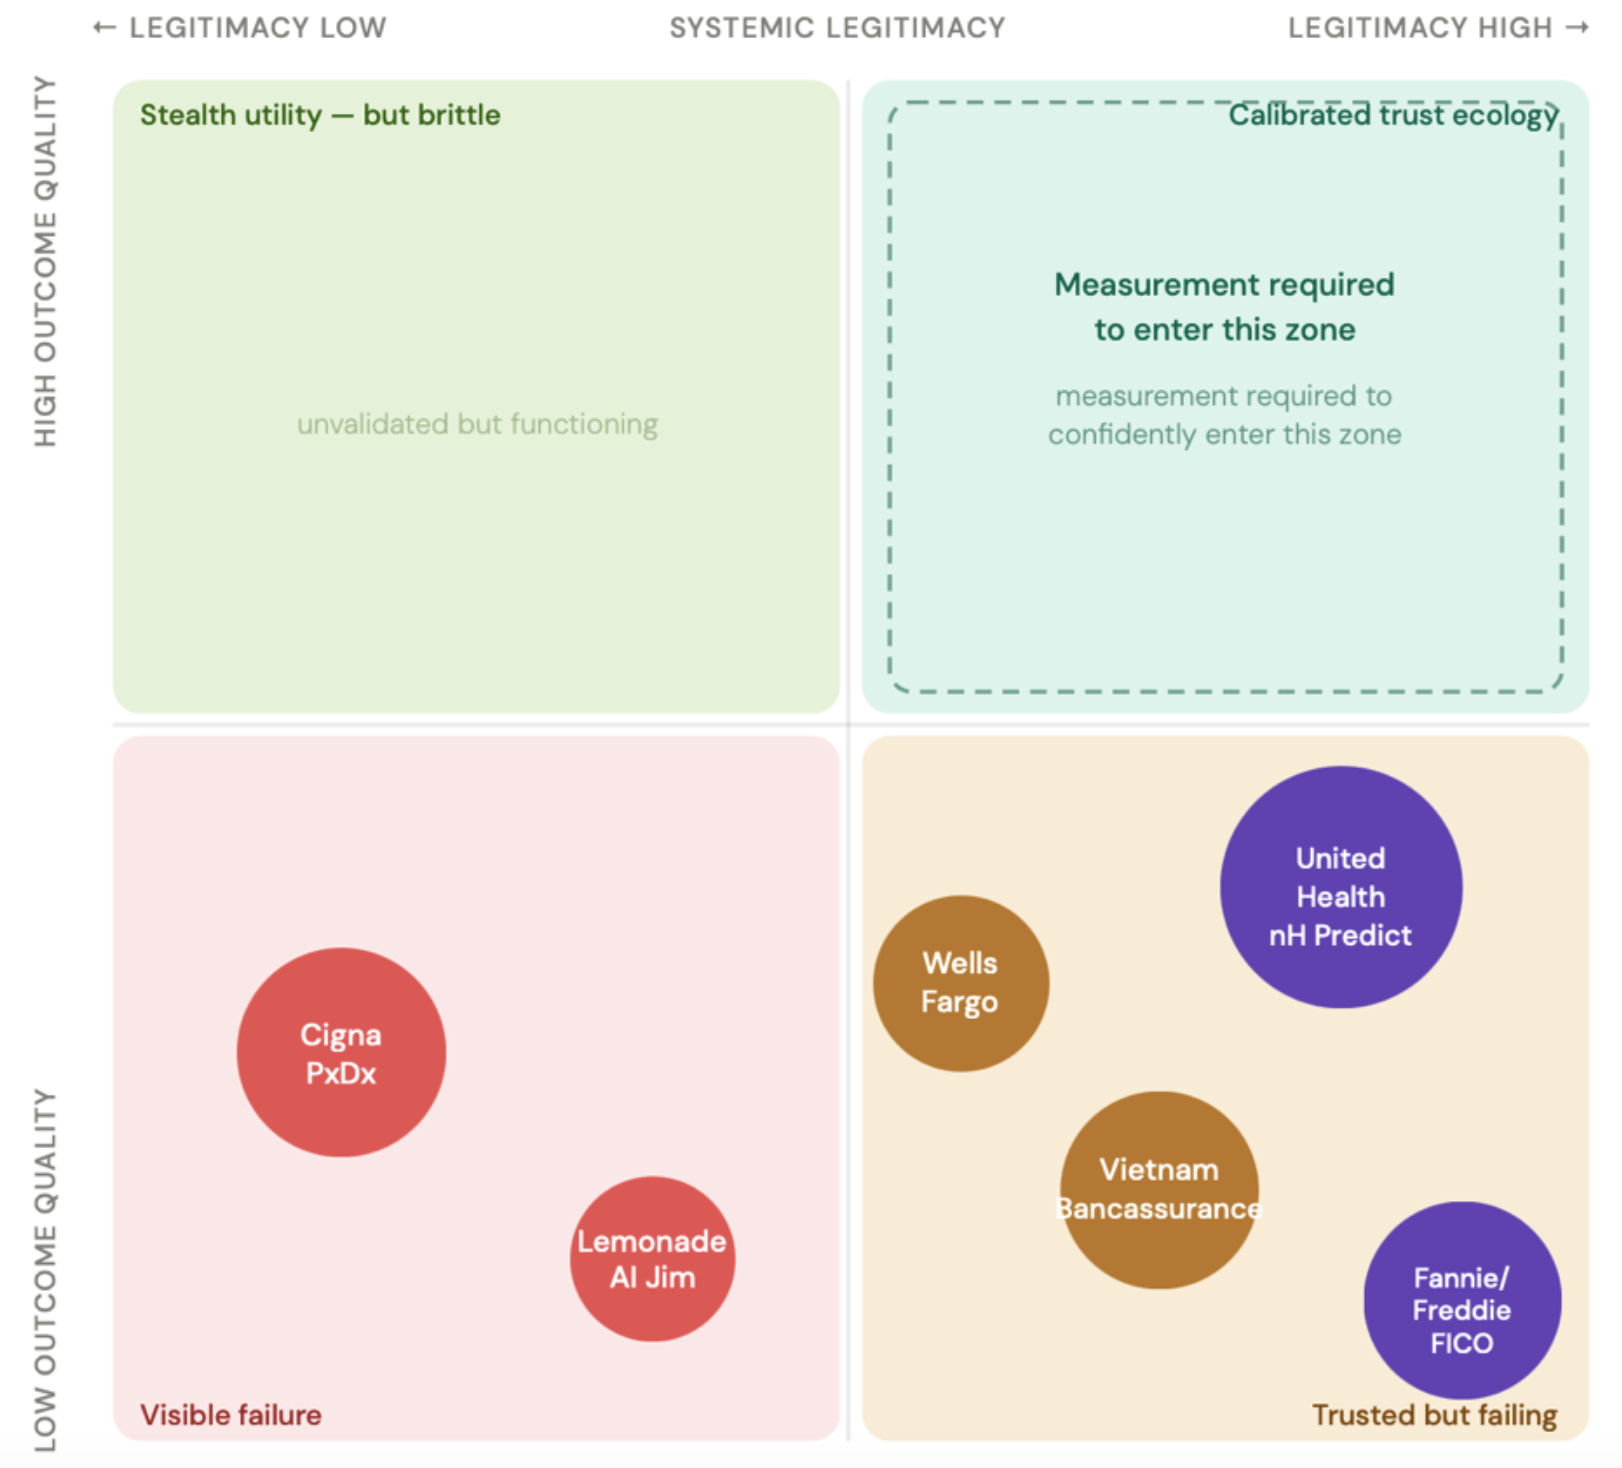
FIGURE 1 — SIX BANKING AND INSURANCE AI CASES: LEGITIMACY VS. OUTCOME QUALITY

Bubble size reflects the relative scale of harm. The top half — good outcomes — is largely empty across documented cases. The dashed boundary signals that entry requires measured evidence, not aspiration. Top-left is labelled "Stealth utility — but brittle": AI producing useful outputs without validated trust. Common for routine decisions; fragile under regulatory scrutiny.

Wells Fargo's proprietary software denied 625 homeowners the mortgage modifications they were legally entitled to under HAMP (the Home Affordable Modification Program). Four hundred families lost their homes. Wells Fargo discovered the error in 2015 and did not disclose it publicly until 2018. For three years, institutional trust was maintained while the harm continued.

In Vietnam, regulators approved bancassurance partnerships between major insurers including Manulife and banks including SCB (Saigon Commercial Bank). Digital sales tools guided staff through recommendations. Customers came for savings deposits and left having signed long-term insurance contracts they did not understand. Manulife alone repaid more than $34 million. The industry's first premium decline in a decade followed.

Fannie Mae and Freddie Mac mandate use of the Classic FICO algorithm for conventional mortgage eligibility across approximately half of all U.S. mortgages. Built on 1990s data. Persistent racial disparate impact documented by Berkeley, the Federal Reserve, and investigative journalism. Requests to update the model have been resisted since at least 2014. The algorithm remains in use — government-backed and regulatory-endorsed.

The calibrated trust ecology quadrant remains largely empty. This is not because it is unachievable. It is because few organizations have yet been required to measure whether their trust is calibrated.

Part II — The Trust Ecology Framework: diagnosing what current governance misses

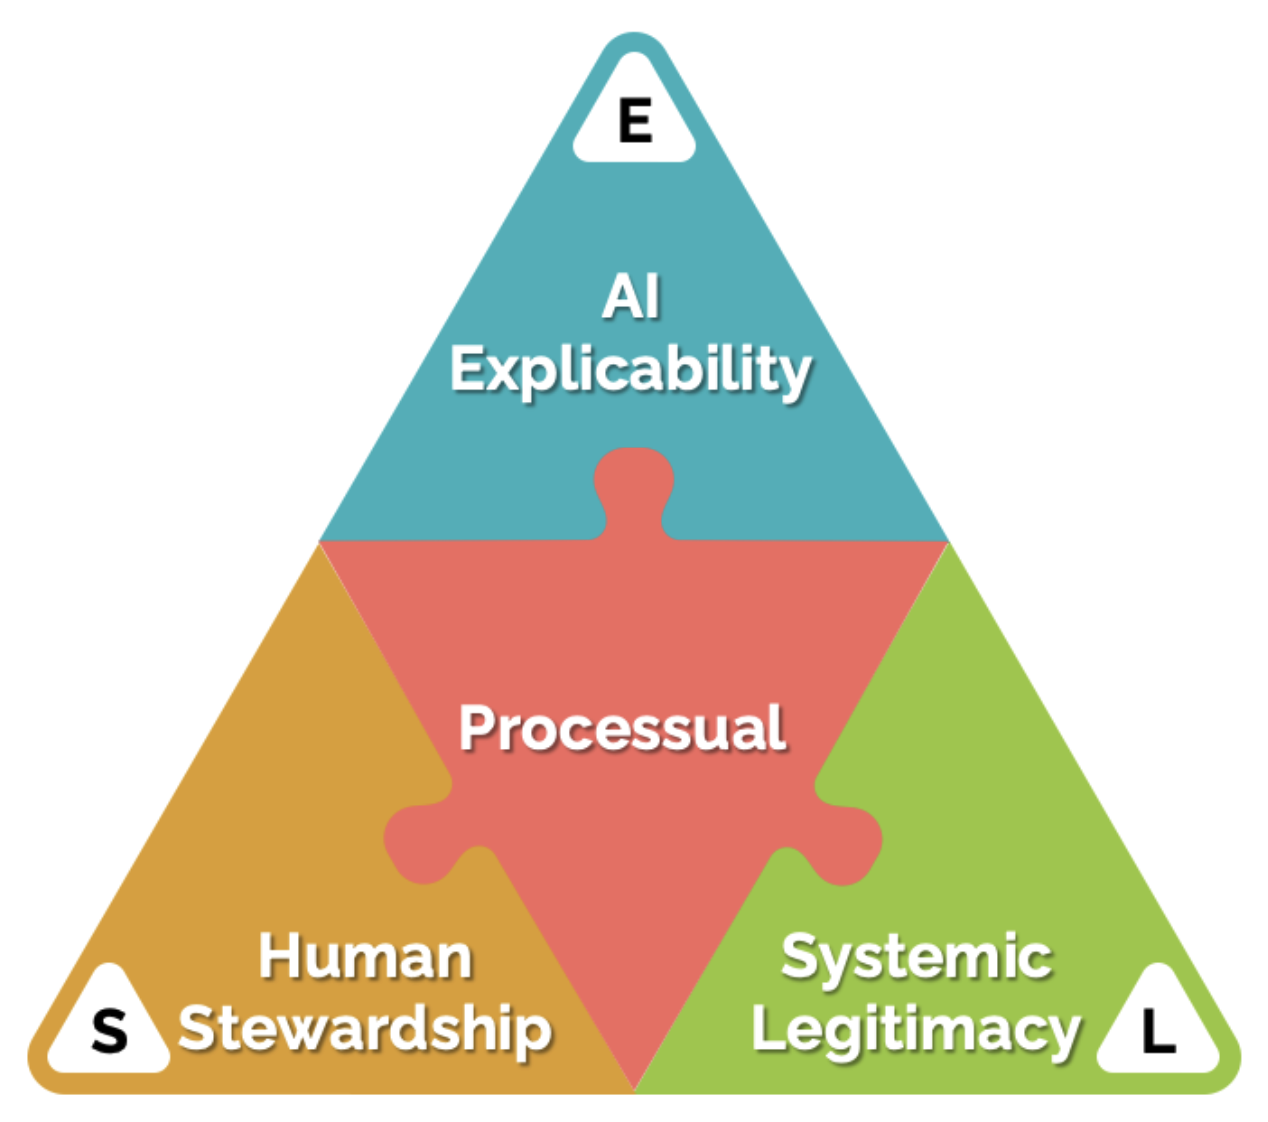
The Trust Ecology Framework (TEF) proposes that trust in AI-augmented decision systems has three interdependent dimensions. A failure in any one destabilizes the others.

FIGURE 2 — THE TRUST ECOLOGY FRAMEWORK: THREE DIMENSIONS (L, S, E)

The processual center represents trust as a continuing equilibrium rather than a state achieved and held. Each case in Figure 1 failed on a specific dimension: UnitedHealth on Human Stewardship (S), Vietnam Bancassurance on Systemic Legitimacy (L), Fannie/Freddie FICO on AI Explicability (E).

Systemic Legitimacy (L) asks whether the institutional and regulatory environment supports trust that is appropriate rather than merely convenient. High legitimacy is not the same as warranted trust. UnitedHealth, Fannie/Freddie, and the Dutch Toeslagenaffaire all carried maximum institutional legitimacy alongside significant undetected harm.

Human Stewardship (S) asks whether the people operating the system are engaging with it at the right level of reliance. This is the governance question that audit programs and model validation cycles rarely ask. It operates at the level of the individual claims handler on a Tuesday afternoon, not the quarterly risk committee.

AI Explicability (E) asks whether the system can support the continuing scrutiny that legitimate trust requires — not just at validation, but continuously in operation. A system can pass all validation requirements and still be trusted at the wrong level if its outputs cannot be interrogated when they should be.

WHAT THIS MEANS FOR YOUR ORGANIZATION
Part III — The Triadic Trust Scale: what it measures and when

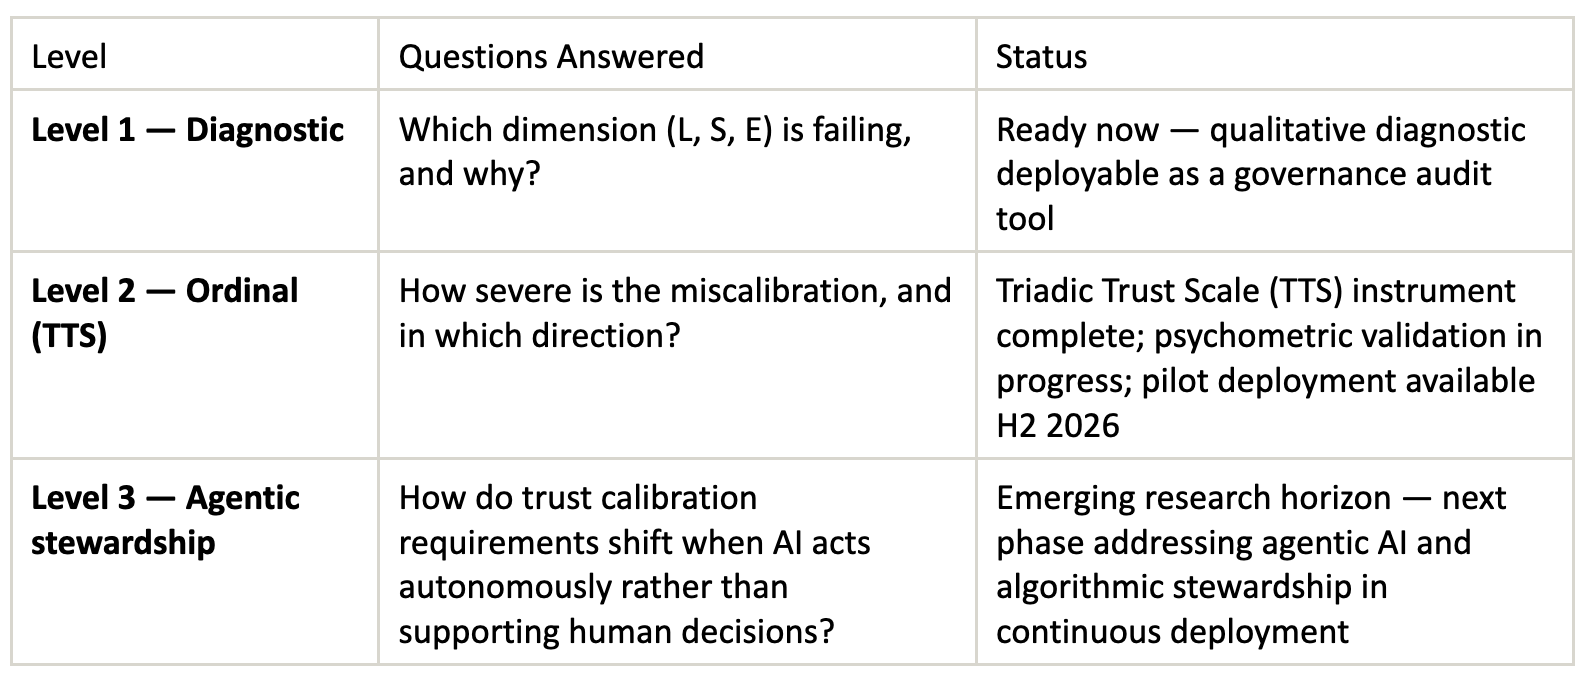
The Trust Ecology Framework operates at three levels. Being explicit about which level is currently available is itself a demonstration of rigor.

The Triadic Trust Scale (TTS) is a psychometric instrument that measures trust calibration across L, S, and E at the individual and institutional level. It distinguishes over-reliance from under-reliance, identifies which dimension is driving miscalibration, and produces a Trust Fidelity Index (TFI) score that creates a quantified baseline for monitoring over time. It does not replace model validation or bias testing — it measures the human-AI relationship that determines whether those validation results translate into appropriate operational behaviour.

Level 3 addresses a governance frontier that no current framework has mapped. As AI systems become agentic — routing claims without handler review, flagging fraud without adjuster involvement, pricing policies without underwriter sign-off — the question of trust calibration shifts from "are humans relying on this at the right level" to "should humans be in this loop at all, and how do we govern the ones who are not." That is a harder problem and an open research question. We frame it openly as an emerging research frontier.

Part IV — From diagnosis to action

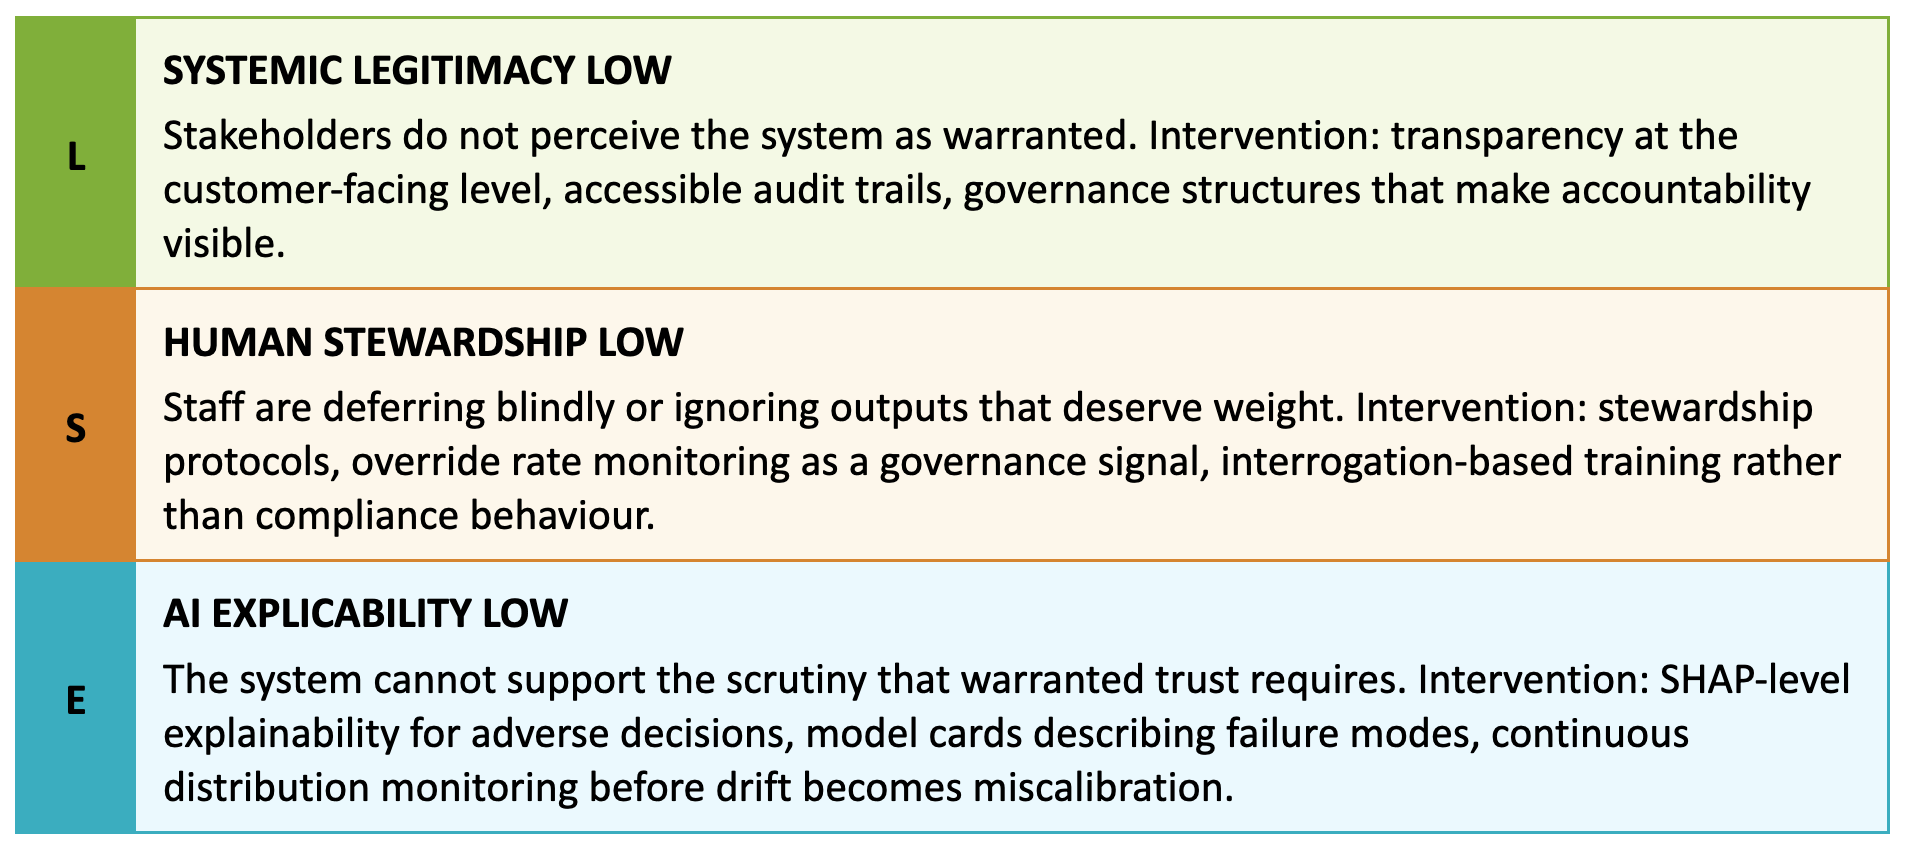
If Systemic Legitimacy (L) is low, the institution has deployed AI where stakeholders do not perceive it as warranted. The intervention is transparency: explainability at the customer-facing level, accessible audit trails, accountability structures that are visible. Vietnam Bancassurance failed here — the regulatory framework endorsed the partnership model without ever validating whether customers could trust the decisions being made on their behalf.

If Human Stewardship (S) is low, staff are either deferring blindly or ignoring outputs that deserve weight. The intervention is stewardship design: decision protocols that structure when override is appropriate, override rate monitoring as a governance signal, training that builds interrogation capability rather than compliance behaviour. UnitedHealth failed here — the algorithm became a target to hit rather than a tool to question.

If AI Explicability (E) is low, the system cannot support the scrutiny that warranted trust requires. The intervention is technical: SHAP-level explainability for adverse decisions, model cards describing failure modes, continuous monitoring that detects distribution shift before it becomes miscalibration. Fannie/Freddie FICO fails here — the algorithm resists the scrutiny its scale of impact demands.

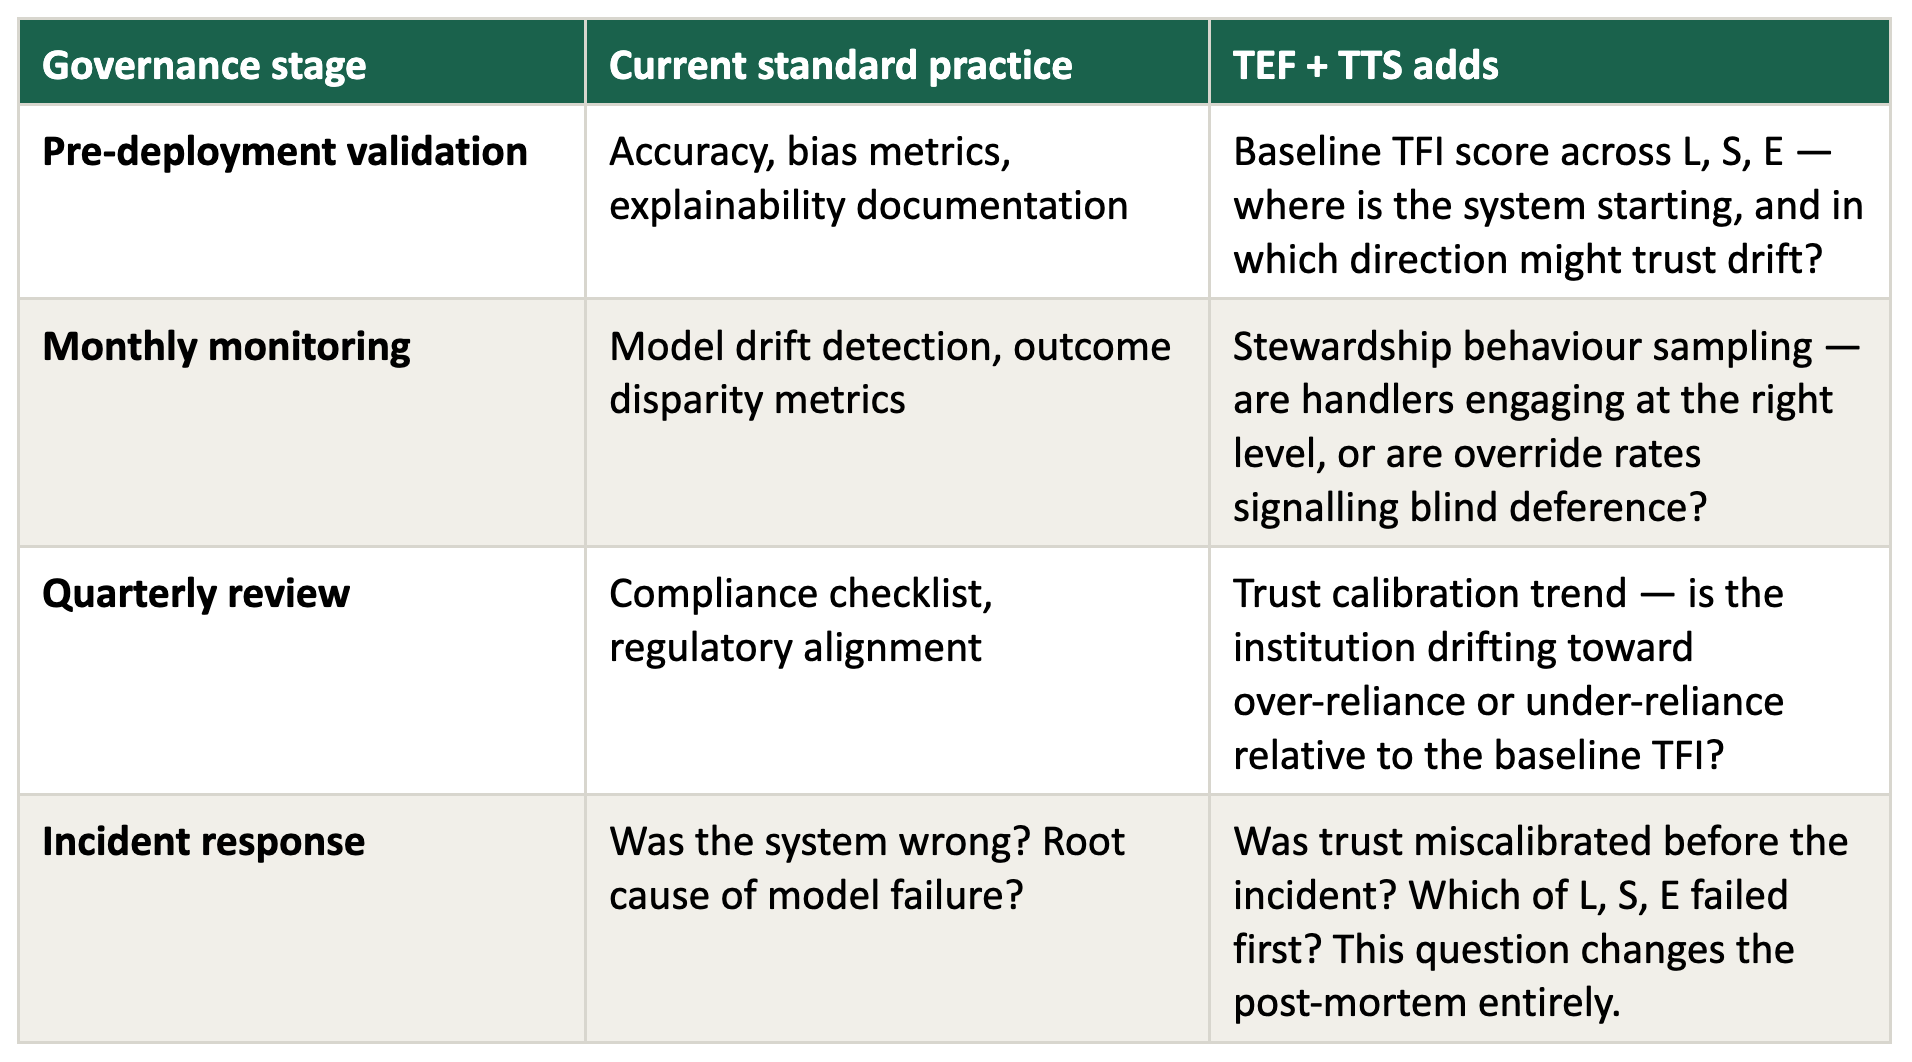
FIGURE 3 — FROM GOVERNANCE CHECKLIST TO TRUST AUDIT: WHAT TEF ADDS

TFI = Trust Fidelity Index, the composite score produced by the TTS. The incident response addition is the question that current post-mortems rarely ask — and the one that would have surfaced UnitedHealth, Wells Fargo, and Vietnam Bancassurance earlier.

The target quadrant is empty — and that is where the work begins

Calibrated trust ecology is not an aspiration. It is the absence of a known failure mode. Very few organizations have publicly demonstrated it, not because it is out of reach, but because the tools to measure it have not existed. The precedents for building those tools are in other high-stakes human-machine domains: aviation crew resource management, surgical checklists, nuclear control room protocols. In each case, the move from "the system is certified" to "the human-system relationship is calibrated" required a deliberate measurement program. Insurance and banking AI governance is at the same threshold.

The question is not whether your AI systems are performing. Your dashboards tell you that. The question is whether the trust your institution has placed in those systems is warranted — and whether the people using them are engaged at the right level to catch what the dashboards cannot show.

That question now has an instrument. The target quadrant is empty — and that is where the work begins.


Rachel Hor

Profile picture for user RachelHor

Rachel Hor

Rachel Hor is a doctoral candidate at Saint Mary's University, where her research focuses on how trust fractures when AI, human judgment, and institutional systems collide in insurance. 

She has nearly two decades of industry experience at IBM, Accenture, and Cognizant. 

DEMO: Higson

Higson is an ultra‑fast Business Rules Engine for configuring insurance products, pricing and rules without code changes with very low latency and high throughput.


 Watch Our Demo: 

Learn More

Are you interested in learning more about Decerto and about Higson?  Please visit these sites to learn more or to schedule a personal demo:

Why We Are the Right Solution For Your Needs

Most P&C insurers manage pricing, underwriting, claims, and compliance rules across separate systems - each governed by different teams and operating on different release cycles. When regulatory changes occur, organizations often end up running multiple parallel workstreams while hoping all outputs remain aligned.

Higson consolidates decision logic within a single rules engine, giving business users direct control over processes that are traditionally dependent on IT delivery queues.

Pricing analysts, underwriters, and compliance teams can author and deploy changes directly using decision tables, visual flows, and embedded scripting capabilities with full version control and auditability built in.

From a technical perspective, Higson executes rules with an average latency of 0.23 ms and supports up to 9,000 requests per second. A proof of concept can run on AWS at approximately $0.63 per hour, while CPU-based licensing ensures infrastructure costs scale with actual usage rather than user counts.

Three Main Benefits of the Product: 
  • Performance:  Higson executes rules with an average latency of 0.23 ms and supports up to 9,000 requests per second in a standard configuration. Thanks to the built-in ONNX runtime, trained ML models can run directly inside decision tables without requiring a separate inference layer.
  • Scalability:  Our CPU-based licensing model means you pay for actual production usage rather than user counts. A proof of concept can run on AWS at approximately $0.63 per hour, with infrastructure costs scaling predictably alongside transaction volume.
  • Business-Owned Decision Logic:  Pricing analysts, underwriters, and compliance teams can create and deploy rule changes directly using decision tables, Groovy and Python functions, as well as visual flows without relying on IT support or opening development tickets. The platform includes full version control, auditability, and simulation capabilities before deployment to production.
What Part(s) of the Insurance Industry Can Benefit From Our Product: 
  • Claims
  • Customer Experience
  • Customer Service
  • Distribution
  • Operational Efficiency

Decerto

Profile picture for user Decerto

Decerto

Decerto specializes in advanced IT solutions for the insurance and finance sectors. With 20 years of experience, the company provides custom software development, system architecture, data migration, and long-term maintenance.

Its flagship products include Agent Portal – 360 Agent’s Workplace (workflow automation), Higson (a Business Rules Engine/product configurator), and Claims AI (claims processing automation). 

Decerto serves global giants such as Allianz, Generali, Everest, Convex, and Sompo International

The company has been recognized by the Clutch 100 Fastest Growth and Insurtech 100 lists, and has received the European Insurance Technology Awards, among others.

The Growing Backlash Against AI

Amid all the talk about how intelligent AI can be and how to best implement it, many are missing the growing backlash among younger generations. 

Image
Frustrated Person

As long as everyone has been telling their Ted Turner stories in the wake of his recent death, I thought I'd tell mine, before getting on to this week's business: what I see as a growing backlash among younger generations toward AI that business leaders need to contend with.

My story comes from my friend Marc (a former managing director at Marsh McLennan, as it happens). He was at the helm in a multi-day sailboat race around Long Island in the 1980s and timed the start almost perfectly. In the chaotic way that these races start, you don't know when the horn will blow, so you circle as you try to be at full speed with a clear path to the starting line when the horn sounds. Marc had succeeded — but Ted Turner was bearing down on him, aiming for the same spot on the line that Marc was going to cross. 

Marc had the right of way, but this was Ted Turner, recent winner of the America's Cup, in a much bigger, faster boat, with a world class, steely glare as he steered his boat on a collision course with Marc. 

Marc never wavered, and at the last possible moment Turner bore off, did a 360, and crossed the starting line a minute or so later. Turner won the class among the biggest boats, while Marc and his crew just did well in his class of smaller ones. Finishing late at night, he and his crewmates headed to a bar to decompress. At 1am, they were getting ready to call it a night, when the bartender set a round of drinks in front of them and said they were sent with the compliments of the gentleman at the door. The gentleman was Ted Turner. He nodded respectfully in their direction. Then he gave them the finger with both hands and stormed out.

The bartender told Marc that Turner said he'd been scouring every bar on the waterfront in search of Marc and his friends. Whatever else you want to say about Turner, the man had style.

Now on to the backlash against AI that we all should be watching. 

I use my daughters, aged 32 and 29, as my antennae about attitudes among Millennials and Gen Z, and they started bristling about AI months ago. Initially, they complained about the huge amounts of water required for cooling. If I ever mentioned using an AI for something, one of them might make a snide remark — they're given to snide remarks with their father — like, “I guess the real prompt is: ‘Hey ChatGPT, could you please drain another reservoir for me?’”

Hyperscalers' wild need for electricity for their gen AI data centers led to concerns about what AI was doing to the environment. That my daughters' electric bills were climbing didn't help matters.

More recently, they've resonated with the concerns of those facing the prospect of having data centers built near them, each spanning perhaps tens of thousands of acres. To top it all off, my older daughter lost her writing job to an AI, as I mentioned last week. The girls have told me to turn off the AI summary that Google Search now offers.

A recent New York Times article reports on a Gallup survey that found Gen Z's attitude toward AI souring, and for reasons that go well beyond the sorts of environmental concerns that initially triggered my daughters. 

"Many respondents did acknowledge that A.I. might make them more efficient in school and the workplace," the article said. "But they were concerned about how the technology would affect their creativity and critical thinking skills.

"Young adults in the work force were especially skeptical. Close to half of those surveyed said the risks of artificial intelligence outweighed its potential benefits in the workplace, an 11-point jump from the previous year. Only 15 percent said they saw A.I. as a net benefit."

The Times also reported on a viral video (that my daughters had already made sure I saw) of a woman giving a commencement speech in which she declared that "the rise of artificial intelligence is the next Industrial Revolution" — only to be roundly booed by the students. 

“'What happened?' [she] stammered, looking over her shoulder, as if searching for an escape hatch," the Times reported.

She continued: 

"'Only a few years ago, A.I. was not a factor in our lives.

"The crowd erupted in cheers.

“'And now, A.I. capabilities are in the palm of our hands.' Boooooooooo.

"One might call it a 'read the room' moment."

Eric Schmidt, former CEO of Google, got booed even harder when talking about AI in his commencement address at the University of Arizona on Friday.

I'm not saying dissatisfaction among younger generations will stop the adoption of generative AI, any more than concerns by earlier generations could stop the internet or the smartphone. I'm also not saying Millennials and Gen Z are Luddites; they're extremely sophisticated about technology. 

What I'm saying is that younger generations seem to be taking a warier approach than those of us of a certain age, who've not only been through a few technology revolutions and have accepted their inevitability but whose views are perhaps softened by what all the AI investments are doing for our retirement accounts. 

And those younger generations get a vote. The discussions among business leaders may be about use cases for AI, about how to implement AI most effectively, about how to demonstrate ROI to shareholders, and so on, but your employees are going to be doing that implementing. If a big chunk of your work force dislikes or distrusts AI, they can provide a lot of silent resistance that may surprise you if you haven't made the effort to understand their concerns and to work with your employees to address them.

Cheers,

Paul

P.S. After writing this commentary last night, I wake up today to find that I'm not the only one thinking about the AI backlash. A New York Times columnist wrote: Why College Grads Are Booing Their Commencement Speakers. The Wall Street Journal led its website with: The American Rebellion Against AI Is Gaining Steam. Their reporting/reasoning differs a bit from mine, but my conclusion remains the same: Proceed with caution. 

P.P.S. It is with great sadness that I note the passing of Stephen Applebaum at age 81. Stephen was one of the earliest and dearest friends of ITL and was generous not just with me but with everyone he met in his decades of work in the insurance industry. I looked back through the 80-some articles Stephen wrote or co-wrote for us over the years to see if I might single out a few, but there are just too many sharp insights. I will point to one, which he wrote a year ago with his business partner, Alan Demers, because it's not only very smart but because Stephen always struck me as an empathetic man: "Re(Defining Empathy in Insurance." 

Here is a link to a brief obituary, to the funeral arrangements and to a way to donate to the Dragonfly Foundation, a favorite of Stephen's that focuses on pediatric cancer care.

May his memory be a blessing.

DEMO: Your Product Name

Demo Product Summary (25 words or less)


ITL Demo Logo
What Part(s) of the Insurance Industry Can Benefit From Our Product: 

(You may select any or all of these bullet points.  Just let us know which ones to remove.  IF you select Other, please provide us with that Category.  Maximum of 1 Other Category can be added.) 

  • Claims
  • Customer Experience
  • Customer Service
  • Distribution
  • Operational Efficiency
  • Other: 
Three Main Benefits of the Product: 
  • Point 1 (Max 160 characters, including spaces and punctuation)
  • Point 2 (Max 160 characters, including spaces and punctuation)
  • Point 3 (Max 160 characters, including spaces and punctuation)
Why We Are the Right Solution For Your Needs

General Description or Sales Pitch.  We recommend limiting this to 1 to 2 paragraphs, so the reader can quickly get to watching your Demo Video.  

 Watch Our Demo: 

Demo Video Placed Here.  Video must be hosted by ITL, so please provide us with a method to download the video.  

Learn More

Are you interested in learning more about <Company> and about this product?  Please visit these sites to learn more: 

(You can provide us with any or all the below links)

  • Website Link
  • Linkedin Link
  • X Link
  • Facebook Link


Organizations Must Plan for Climate Tipping Points

Organizations must incorporate climate tipping points into risk planning as scientific focus shifts from if to when they'll occur.

Melting Glaciers

Finding a route through extreme uncertainty from climate tipping points is now urgent for organizations. A pragmatic mindset and proven techniques can uncover your path.

Climate systems are moving toward abrupt, irreversible shifts. These tipping points include the collapse of the Atlantic Meridional Overturning Circulation (AMOC), the system of ocean currents in the Atlantic that plays a crucial role in regulating Earth's climate by transporting heat from the tropics northward.

The AMOC is likely weakening. Should it reach a tipping point, the impacts could challenge the historical wisdom that climate change unfolds gradually. Regional conditions could now flip quickly, bringing severe cooling to northern Europe, forcing storm tracks into new positions, shifting monsoons and altering coastlines.

The most recent Nordic Tipping Week saw researchers and policymakers treat AMOC tipping as a realistic planning case. When science moves from questioning if a tipping point might happen to focusing on when, an organization's planning expectations need to change.

It is critical that organizations and their stakeholders lift themselves out of the climate catastrophizing that tipping points may prompt. That's because doom can shut down action.

Instead, it is important to view tipping points through a constructive lens that focuses on "earthshots," not "moonshots." We're not talking here of hope over expectation but deploying disciplined techniques in which risk professionals are already well-versed.

Tipping‑point‑aware tools and techniques, such as enhanced scenario planning and strategic planning with advanced risk identification, can help you replace passive dread with active preparation. Incorporating tipping points into an organization's risk management and strategic planning will also help maintain credibility with the regulators, investors and insurers we can expect to ask tougher questions on business's readiness for extreme disorder.

The impact of AMOC tipping points

Should the AMOC cross its tipping point, we could see rapid and irreversible climate shifts, including:

  • Severe winter cooling across northern Europe
  • More intense storms and altered storm track behavior
  • Long-term agricultural disruption
  • Major changes in water and food availability.

Given measured weakening and converging scientific warnings, the most prudent approach for businesses, particularly those with UK or European exposure, is to incorporate the possibility of AMOC weakening into their risk register and scenario testing. The time has come to view AMOC tipping as a credible tail risk to which businesses need to prepare.

When a system approaches a tipping point, a business should prize preparedness over precision. An organization's role here isn't about beating scientists to pinpoint the exact moment of a shift but strengthening its ability to remain stable when uncertainty accelerates.

Organizations should start by identifying those areas where they are most dependent on climate stability; think agricultural inputs, logistics routes or water availability. How would abrupt cooling, extreme storms or rainfall shifts put pressure on the most climate-reliant nodes of their operations and supply chains?

Enhanced scenario planning for effective adaptation

Organizations can no longer assume risk mitigation will keep climate risk within more familiar limits. Ice melt, freshwater dilution in the North Atlantic, and shifts in rainfall belts are already building momentum, with some impacts locked in for decades. That means businesses should consider tipping-point-aware adaptation as part of their strategic decision‑making, calling on scenarios that extend beyond traditional pathways.

Severe-but-plausible scenarios, such as sudden cooling in Europe or major shifts in precipitation zones, will provide a clearer understanding of the future operating environment. Updated scenarios should be able to test the full chain of consequences, rather than the most familiar ones, investigating how physical risks and supplier reliability might change under tipping‑point conditions.

These scenarios may well feel uncomfortable, but they are also far from improbable.

Insurance AI Adoption Outpaces Governance

Rapid AI adoption in insurance is outpacing governance frameworks needed to ensure regulatory compliance and maintain customer trust.

Governance

While AI is moving quickly in insurance, trust is struggling to keep pace. Recent research found that 90% of senior insurance professionals in the UK and Europe expect end-to-end claims administration to be managed by AI within the next 24 months. Yet, 87% are concerned about bias or unfair outcomes, and 99% believe there should still be some level of human oversight.

This contradiction is at the center of conversations around deploying AI in insurance. Firms aren't reluctant to introduce the technology. That is happening. What they are less certain on is how to govern it.

Why insurance faces a unique AI challenge

Insurance may be similar to other industries in that it is exploring and actively deploying AI, but where it differs is regulation. By its very nature, insurance is a highly regulated industry, and for good reason. Each decision affects customer outcomes directly and must operate within strict expectations around fairness and transparency.
The key challenge for insurers deploying AI lies in its probabilistic nature. AI identifies patterns, generates outputs and makes predictions based on statistical inference. That is great in areas such as fraud detection and data extraction, but regulated claims decisions require something more rigid. Firms must be able to show and explain exactly how and why a decision was reached. Regulators will not accept "our AI decided" as a sufficient explanation, nor should customers. This is why 39% of the industry say that transparent algorithms and decision logs would help reassure them about the use of AI in insurance.

The issue facing insurance firms is whether they can deploy AI within these regulated processes without creating unacceptable operational, reputational or compliance risks.

The governance conundrum

Nowhere is this tension more obvious than in claims. The research found that the industry feels least comfortable automating claims submissions, with 40% identifying it as an area they would not feel comfortable handing over to AI, ahead of underwriting recommendations and customer interactions.

Claims decisions are among the most sensitive moments in the insurance workflow. They need to be consistent, transparent and capable of being mapped back to explicit rules and policy terms.

This doesn't mean that AI has no place in claims. Used properly, AI can extract structured data from unstructured sources, detect anomalies and flag potentially fraudulent claims, enrich claims data with external sources and prioritize cases for human or automated rules-based assessment.

But when it comes to claims decisions, the only compliant way to leverage AI is to use a rules engine. Because these are fully configured and controlled by the insurer, rules engines remove the unpredictability of machine learning models and instead apply deterministic, auditable business logic to every claim.

As a result, each decision is documented against explicit rules. This ensures transparency, compliance and reinforces customer trust in the fairness of the insurer and the industry.

The moment AI moves from assistant to judge, firms risk crossing a line that governance frameworks are not yet ready to support.

AI deployment with accountability

While the industry is keen to advance the use of AI, it's clear that compliance teams do have genuine concerns. This is driving a focus on how to make AI adoption viable in practice, which is showing up in procurement decisions.

Insurers are willing to compromise on cost to find the right AI solutions, prioritizing ease of integration and strong vendor support. In fact just 10% of senior professionals said cost would strongly influence their decision.

This is the sign of a necessarily cautious market. For all the noise around AI, insurers are becoming more discerning. They are not just asking only what a system can automate but whether it can be trusted in a regulated setting, whether it can integrate with existing workflows and whether it gives them enough visibility and control to stand behind the outcomes it produces.

Those firms driving genuine innovation in insurance won't be the firms making the boldest claims about total automation but those building systems that are fit for purpose within this highly regulated industry. In practice, that means combining AI with deterministic rules, strong oversight, clear escalation paths and audit-ready decision making. It means using AI to improve speed and efficiency without surrendering control over outcomes that need to remain consistent and accountable.

Insurance should absolutely embrace AI – the gains are too significant to ignore, and the appetite across the market is undeniable. The real contest is not whether the insurance industry can deploy AI quickly, it is whether governance can keep pace as it does.


Ross Sinclair

Profile picture for user RossSinclair

Ross Sinclair

Ross Sinclair is founder and CEO at EIP, an embedded insurance firm.

He spearheaded the rollout of mobile phone insurance across Europe in the 1990s as insurance managing director at Carphone Warehouse. He has launched insurance programs in over 30 countries.

The Wasted Effort in Commercial Insurance Renewals

Despite advances in AI and automation, commercial insurance still rebuilds the same risk information from scratch every renewal cycle.

View of Buildings from Street Level

Commercial insurance has become significantly more advanced over the past decade. Agencies and carriers now operate with better analytics, more data sources, improved workflows, and increasing levels of automation. Artificial intelligence has entered underwriting conversations, submission workflows are becoming more digitized, and the industry continues investing heavily in modernization.

Yet despite all of this progress, one core issue remains surprisingly unchanged: The insurance industry keeps rebuilding the same risk from scratch.

This becomes especially visible in commercial property and casualty insurance. A construction account, builder's risk placement, cyber renewal, or complex liability program may remain fundamentally similar from one year to the next, yet much of the underwriting process starts over every cycle. ACORD applications are updated again. Supplemental forms are rewritten. Loss narratives are recreated. Exposure schedules are reformatted. Questions that were answered previously are revisited through slightly different formats and requirements.

The account may already exist within the market ecosystem, but the information surrounding it often behaves as if it does not.

This is more than an operational inconvenience. It reflects a deeper structural issue in how commercial insurance represents risk.

The Reconstruction Problem

Today, most commercial risks are still communicated through fragmented documents, emails, PDFs, spreadsheets, broker narratives, and carrier-specific workflows. Information moves between insureds, brokers, underwriters, and carriers, but rarely in a persistent or standardized form. As a result, each renewal cycle becomes a reconstruction effort. The same account is repeatedly translated, summarized, reformatted, and re-explained across different systems and market participants.

Anyone working closely with commercial submissions sees this regularly. A builder's risk account may require project values, construction timelines, subcontractor exposure information, and prior loss explanations every time it approaches the market. Cyber renewals often revisit MFA protocols, vendor dependencies, incident response procedures, and operational controls even when much of the environment remains largely unchanged. Professional liability and construction liability submissions frequently involve recreating narratives around operations that have already been explained multiple times in previous underwriting cycles.

In many cases, underwriters are not evaluating risk immediately. They are first reconciling fragmented representations of risk before meaningful evaluation can even begin.

The industry has become very good at moving information.

It has not yet solved how to maintain risk information as persistent intelligence over time.

That distinction matters.

Why AI Doesn't Fully Solve the Problem

Much of the current conversation around AI in insurance focuses on workflow efficiency. AI tools can extract data from applications, summarize documents, organize submissions, and improve communication between market participants. These developments are valuable and will continue improving operational speed.

But AI can improve the workflow around the problem without fully solving the problem itself.

If the underlying representation of risk remains fragmented, inconsistent, or repeatedly reconstructed, then the industry is still operating within a document-centric model of underwriting. Technology may accelerate the process, but acceleration alone does not eliminate the underlying friction.

This also helps explain why submission quality continues to matter so much in commercial insurance. Two accounts with similar underlying risk characteristics can produce very different underwriting experiences depending on how clearly the risk is represented. A structured submission with coherent narratives, organized exposure data, and contextualized losses creates confidence. A fragmented submission introduces uncertainty, even when the underlying account itself may not be materially different.

In many ways, brokers and agents have quietly become the market's risk translation layer. They are not simply moving paperwork between insureds and carriers. They are reconstructing fragmented risk information into forms the market can evaluate, compare, and trust.

What Comes Next

As commercial insurance continues moving deeper into AI, analytics, and automation, this issue will become more important—not less.

Because the future competitive advantage may not belong solely to organizations that process information faster. It may belong to those that can represent risk more consistently, more persistently, and with less reconstruction across the insurance lifecycle.

The industry has spent years modernizing insurance workflows.

The next challenge may be modernizing how insurance itself represents risk.