Download

Wellness Vendors Keep Dreaming

Vendors claim a 230% decrease in the likelihood of claims by participants. News flash: You can't be 230% less likely than anyone on anything.

||||||
Alice laughed: “There’s no use trying,” she said. “One can’t believe impossible things.” “I daresay you haven’t had much practice,” said the Queen. “When I was younger, I always did it for half an hour a day. Why, sometimes I’ve believed as many as six impossible things before breakfast.” Six impossible things before breakfast?  The wellness industry would just be getting warmed up by believing six impossible things before breakfast. Wellness vendors believe enough impossible things all day long to support an entire restaurant chain: Consider the article in the current issue of BenefitsPro — forwarded to me by many members of the Welligentsia — titled: “Can the Wellness Industry Live Up to Its Promises?”  BenefitsPro interviewed US Corporate Wellness, Fitbit, Staywell and HERO. Each is a perennial candidate for the Deplorables Awards — except US Corporate Wellness, which already secured its place in the Deplorables Hall of Fame (see, Why Nobody Believes the Numbers) several years ago with these three paeans to the gods of impossibility. In case you can’t read the key statistic — the first bullet point — it says: “Wellness program participants are 230% less likely to utilize EIB (extended illness benefit) than non-participants.” Here is some news for the Einsteins at US Corporate Wellness: You can’t be 230% less likely to do anything than anybody. For instance, even you, despite your best efforts in these three examples, can’t be 230% less likely to have a triple-digit IQ than the rest of us. Here’s a rule of math for you: a number can only be reduced by 100%. Rules of math tend to be strictly enforced, even in wellness. So the good news is, even in the worst-case scenario, you’re only 100% less likely to have a triple-digit IQ than the rest of us. See also: 6 Pitfalls to Avoid With Core Systems   And yet, if it were possible to be 230% dumber than the rest of us, you might be. For instance, US Corporate Wellness also brought us this estimate of the massive annual savings that can be obtained just by, Seinfeld-style, doing nothing: Assume I spent about $3,500/year in healthcare 12 years ago, which is probably accurate. My modifiable risk factors were zero then and are still zero — no increase. So my healthcare spending should have fallen by $350/year for 12 years, or $4,200 since then. But that would be impossible, because I could only reduce my spending by $3,500. Do you see how that works now? To his credit, US Corporate Wellness’s CEO, Brad Cooper, is quoted in this article as saying: “Unfortunately some in the industry have exaggerated the savings numbers.” You think? I’m pretty sure this next one is impossible, too. I say “pretty sure” because I’ve never been able to quite decipher it, English being right up there with math as two subjects that apparently frustrated many a wellness vendor’s fifth grade teacher: 400% of what? Is US Corporate Wellness saying that, as compared with employees with a chronic disease like hypertension, employees who take their blood pressure pills are 400% more productive? Meaning that, if they controlled their blood pressure, waiters could serve 400% more tables, doctors could see 400% more patients, pilots could fly planes 400% faster? Teachers could teach 400% more kids? Customer service recordings could tell us our calls are 400% more important to them? Or maybe wellness vendors could make 400% more impossible claims. That would explain this BenefitsPro article. Fitbit We have been completely unable to get Fitbit to speak, but BenefitsPro couldn’t get the company to shut up. Here is Fitbit’s Amy McDonough: “Measurement of a wellness program is an important part of the planning process.” Indeed it is! It’s vitally important to plan on how to fabricate impossible outcomes to measure, when in reality your product may even lead to weight gain. Here is one thing we know is impossible: You can’t achieve a 58% reduction in healthcare expenses through behavior change — especially if (as in the 133 patients the company tracked in one study) behavior didn’t actually change. You can read about that gem, and others, in our recent Fitbit series here: Health Enhancement Research Organization (HERO) and Staywell I’ll consider these two outfits together because people seem to bounce back and forth between them. Jessica Grossmeier is one such person. Jessica became the Neil Armstrong of impossible wellness outcomes way back in 2013. While at Staywell, she and her co-conspirators told British Petroleum they had saved about $17,000 per risk factor reduced. So, yes, according to Staywell, anyone who temporarily lost a little weight saved BP $17,000 — enough to clean up about 1,000 gallons of oil spilled from Deepwater Horizon. See British Petroleum’s Wellness Program Is Spewing Invalidity for the details. Leave aside both the obvious impossibility of this claim, and also the mathematical impossibility of this claim given that employers only actually spend about $6,000/person on healthcare. Jessica’s breakthrough was to also ignore the fact that this $17,000/risk factor savings figure exceeds by 100 times what her very own article claims in savings. Not by 100%. By 100 times. Fast-forward to her new role at HERO. In this article, she says: The conversation has thus shifted from a focus on ROI alone to a broader value proposition that includes both the tangible and intangible benefits of improved worker health and well-being. Her memory may have failed her here, too, because HERO — in addition to admitting that wellness loses money (which explains its “shift” from the “focus on ROI alone”) — also listed the “broader value proposition” elements of their pry-poke-and-prod wellness programs. The problem is the elements of the broader value proposition of screening the stuffing out of employees aren’t “benefits.” They’re costs, and lots of them: When she says: “The conversation has shifted from a focus on ROI alone,” she means: “We all got caught making up ROIs, so we need to make up a new metric.” RAND’s Soeren Mattke predicted this new spin three years ago, observing that every time the wellness industry makes claims and they get debunked, the industry simply makes a new set of claims, and then they get debunked, and then the whole process repeats with new claims, whack-a-mole fashion, ad infinitum. Here is his specific quote: “The industry went in with promises of 3 to 1 and 6 to 1 based on health care savings alone – then research came out that said that’s not true. Then they said: “OK, we are cost neutral.” Now, research says maybe not even cost neutral. So now they say: “But it's really about productivity, which we can’t really measure, but it’s an enormous return.” Interactive Health While other vendors, such as Wellsteps, harm plenty of employees, Interactive Health holds the distinction of being the only wellness vendor to actually harm me. I went to a screening of theirs. To increase my productivity, they stretched out my calves. Indeed, I could feel my productivity soaring — until one of them went into spasm. I doubt anyone has missed this story, but in case anyone has… Interactive Health also holds the distinction of being the first vendor (actually their consultant) to try to bribe me to stop pointing out how impossible their outcomes were. They were upset because I profiled them n the Wall Street Journal. The article is behind a paywall, so you probably can’t see it. Here’s the spoiler: The company allegedly saved a whopping $53,000 for every risk factor reduced. In your face, Staywell! See also: What Is the Major Barrier to Change?   Here is the BenefitsPro article’s quote from Interactive Health’s Jared Smith: “There are many wellness vendors out there that claim to show ROI,” he says. “However, many of their models and methodologies are complex, based upon assumptions that do not provide sufficient quantitative evidence to substantiate their claims.” You think? Finally, here is a news flash for Interactive Health: Sitting is not the new smoking.  If anything is the “new smoking,” it’s opioid addiction, which has reached epidemic proportions in the workforce while being totally, utterly, completely, negligently, mind-blowingly, Sergeant Shultz-ily ignored by Interactive Health and the rest of the wellness industry. There is nothing funny about opioid addiction and the wellness industry’s failure to address it, a topic for a future blog post. The only impossibility is that it is impossible to believe that an entire industry charged with what Jessica Grossmeier calls “worker health and well-being” could have allowed this to happen. Alas, happen it did. And, as I write this post, breakfast hasn’t even been served yet.
Hurricane Harvey: A Moment of Truth

Insurers have a golden opportunity to justify the public’s trust. But they also run the risk of failing to live up to expectations.

The first major hurricane to make landfall in the U.S. since hurricanes Dennis, Katrina, Rita and Wilma in 2005, Hurricane Harvey will cause billions of dollars in economic damage and disrupt countless lives. In the wake of massive economic losses and untold human suffering, including loss of life, millions of individuals and businesses will turn to their insurers for help. This will be a make-or-break experience, a real moment of truth. Insurers will be presented with a golden opportunity to justify the public’s trust and earn the respect of policyholders, regulators, legislators and others in government. But insurers also run the risk of failing to live up to expectations and incurring the wrath of voters and their elected representatives. See also: Flood Risk: Question Is Where, Not When   The first test may well be distinguishing damage caused by wind from damage caused by flooding, as virtually all insurance policies exclude losses due to flooding (the exception being those policies issued by the National Flood Insurance Program). Insurers will need to be careful, thorough and fair when settling claims. Equally important, insurers will need to be perceived as having been so, and communication will be key. Insurers would be well advised to do what they can to make policyholders feel they have been treated with respect, dignity and compassion even when their claims must be denied or settled for some amount less than the claimant sought. Moreover, insurers would be well advised to settle claims as quickly as possible without unduly sacrificing sound loss adjustment and efforts to weed out fraud and abuse. Finally, with the media sure to draw attention to heartbreaking stories about human tragedy in Harvey’s aftermath, insurers might benefit from doing what they can to shine a light on their efforts to help individuals and businesses recover. Surely it is worth noting that, as others evacuate, insurers gear up to send large numbers of claim adjusters to work in extremely difficult conditions in hard-hit areas. Hurricane Harvey will also lead to many other moments of truth. For example, the devastation caused by Harvey may well prove to be the first real test at extreme scale of new insurtech created to improve loss adjustment. Will use of drones, aerial imagery, artificial intelligence, digitalization, big data, predictive analytics and the like prove as beneficial as hoped? Will insurtech entrepreneurs and insurers who have invested in these technologies be vindicated? And, on a more positive note, will experience coping with Harvey reveal new opportunities to use emerging technologies to increase speed, efficiency and fairness? Insured losses from Hurricane Harvey may also test reinsurance mechanisms, including catastrophe bonds, other insurance-linked securities and sidecars. And what about so-called hedge fund reinsurers, which sought to profit by investing insurance float using strategies like those typically employed by hedge funds? Will they continue to participate as claims mount, or will they instead seek to exit the business? Some past catastrophes triggered significant inflows of fresh capital, as investors sensed opportunities to profit from a turn in reinsurance markets. Such was the case following Katrina, Rita and Wilma in 2005. Will the “fast money” come rushing in again, and, if it does, will it prove to also be “smart money”? All of the above raises the question, “Will Hurricane Harvey lead to a reset of catastrophe models, pricing for hurricane risk and underwriting?” Some past storms, such as Hurricane Andrew in 1992, convinced insurers that they had previously underestimated hurricane risk and thus led to dramatic resets in coastal property insurance markets, with attendant price increases and availability problems. Whether Harvey brings about such a reset seemingly depends on whether current catastrophe models did an adequate job alerting insurers to the risk of an event like Hurricane Harvey. If so, changes in coastal property insurance markets may be muted. If not, expect price increases and availability problems. See also: Is Flood Map Due for a Big Data Make-Over?   Last, and let's hope least, Hurricane Harvey may test insurers’ enterprise risk management. Prior to Harvey, the property/casualty industry had ample surplus, and most insurers were well capitalized. But surplus was not evenly distributed across insurers, and only the surplus of those insurers that wrote policies covering properties struck by Harvey is available to cover claims from Harvey. If an insurer only wrote risks in Oregon, its surplus won’t be called upon to cover claims from Harvey. Bottom line, insurers that covered properties affected by Harvey, that were aware of potential losses and that have ample financial resources to cover claims and continue operations can give themselves good grades for enterprise risk management. On the other hand, Insurers that covered properties affected by Harvey, that were surprised by their losses and that lack the resources to cover claims must give themselves failing grades for enterprise risk management. And then there is a gray area: insurers that intelligently judged the risk of insolvency to be acceptably small, took a calculated risk and then lost that bet. Though such insurers will fail, it cannot be said that their enterprise risk management failed. Eliminating even the most remote chance of insolvency is not practical. Neither is it economically viable. Sound enterprise risk management consists of: 1) understanding risks; 2) making conscious, intelligent decisions about which risks to take, which risks to avoid, which risks to mitigate and which risks to transfer; and, 3) enforcing controls that keep operations within the bounds established by an enterprise’s appetite for risk.

Michael Murray

Profile picture for user MichaelMurray

Michael Murray

Michael Murray is a University of Chicago-trained economist passionate about providing decision-quality information and insight that helps others profit from deep understanding of both the big picture and subtle nuances.

IoT: Collaboration Is Now Mandatory

"Collaboration" actually does not begin to convey the looming and enormous demand for working together that IoT will require of all participants.

sixthings
The definition of collaboration is the action of working with someone to produce or create something. That seems far too simplistic a way to describe the many types of collaboration already at work in the insurance industry and moreover does not begin to convey the looming and enormous demand for working together that will be required for success in implementing the Insurance Internet of Things (IoT). Historically, the insurance industry has had to use a wide variety of collaboration tools to succeed as data, information, consumer behavior, products and regulations changed with increasing velocity. These tools included e-mail, texting, instant messaging, content management systems, enterprise social platforms and formal enterprise collaboration software. Insurers have even begun to leverage the use of digital technology and web-based collaboration tools such as Slack to empower employees, enhance user experiences, improve internal communication and strengthen agent and broker relationships. See also: Insurance and the Internet of Things   Looking beyond insurance companies themselves, we note the emergence of insurtech accelerators and incubators, both independent and captive. What is becoming apparent is that there is a convergence taking place between these entrepreneurial startups and the traditional carriers, sparking collaboration between the new, small and fast market entrants with the old, big and slow incumbents. Much more of this kind of collaboration will be required for the insurance industry to survive and thrive in tomorrow’s world. New forms of collaboration are emerging in the insurance ecosystem, some more formal than others. Strategic alliances and partnerships are being announced daily, as are vendor-vendor and carrier-carrier arrangements. Recent examples are plentiful; CoreLogic joined the Guidewire PartnerConnect program to deliver more accurate property risk pricing and residential estimating more efficiently to Guidewire’s property insurance customer base, and Insurity collaborated with Allstate Business Insurance to quickly deliver a new self-service quoting app with convenient data pre-fill. Co-opetition is a more innovative form of collaboration that has been gaining traction. Former competitors work together to leverage a common, defined opportunity that yields better results for each company than either could have achieved on its own. In the world of insurance IoT, of which the connected car is a major subset, we increasingly see original equipment manufacturers (OEMs) participating in programs with auto insurers with telematics data exchanges and with each other in developing vehicle-to-vehicle (V2V) communication standards. In other areas of insurance IoT, we are seeing a rapidly increasing number of health and property insurtech partnership announcements with insurers delivering innovative new risk-management products and services to consumers (e.g. Vitality-John Hancock, Roost-Liberty Mutual, True Motion-Progressive, etc.). As the number of connected things expands exponentially, so, too, will the frequency and velocity of data generated by these sensors and devices. The ability to receive, normalize, manage and use all of this digital data will quickly exceed the capacity and expertise of even the largest insurers, so collaboration with a new generation of information management and data science providers will be mandatory. See also: 12 Issues Inhibiting the Internet of Things   For insurers and others to successfully navigate this burgeoning ecosystem, access to relevant knowledge and competitive information will also be mandatory, and one effective way to gain these insights is participation in subject-specific industry conferences where expert speakers and industry thought leaders share their experiences and insights. One such event is the Insurance IoT USA Summit taking place in Chicago on Nov. 30 and Dec. 1. So critical will be effective collaboration in the future that it is conceivable that formal courses, certifications and degrees in collaboration will be offered by business schools in response to the exploding demand for this set of business skills and expertise driven by IoT proliferation and adoption. In any event, participants in the insurance ecosystem that best master the art of collaboration are sure to be the market leaders of the IoT future.

Stephen Applebaum

Profile picture for user StephenApplebaum

Stephen Applebaum

Stephen Applebaum, managing partner, Insurance Solutions Group, is a subject matter expert and thought leader providing consulting, advisory, research and strategic M&A services to participants across the entire North American property/casualty insurance ecosystem.

Lemonade: World’s First Live Policy

Up until now, changing a deductible or coverage amounts or adding a valuable meant contacting customer support. Not any more.

We've just announced a first-of-its-kind insurance policy. One that puts the power formerly reserved to brokers and agents in the hands of all Lemonade customers!

When we entered the insurance industry, we knew one of the biggest problems with traditional insurers was the endless amounts of red tape and long wait times. That’s why we committed to "instant everything" since day one.

From the world’s first 90-second sign-up to our world-record-setting claims process, we’ve hit some pretty exciting milestones, but they were just a preview of what we’ve got cooking.

See also: A Risk-Free Life Insurance Policy? (No)  

The Old Paper Policy

Up until now, if a customer wanted to change the deductible or coverage amounts or add a valuable that was just bought, the customer had to contact the insurer’s customer support and explain the issue. Then, customers would need to pay for some changes, and probably get a new policy sent to them in the mail (snail mail, of course). That’s where the red tape and long wait times come in, and where the industry, new or old, startup or multibillion-dollar corporation, is right now. But our customers can now make those changes on their own.

As far as we know, no other insurance company allows its customers to modify their coverages or even cancel their policy on their own.

The new release is a great example of the reason behind our decision to take the longer, harder path in becoming a full stack insurance carrier, rather than a reseller. It also explains why we bet on building our own technology instead of taking the easy path of buying old-school IT systems (the ones that run most insurance companies in America today, and the startups that resell their insurance).

Introducing Lemonade’s Live Policy

Even if you buy renters insurance directly from the likes of GEICO or Progressive, the only part that’s direct is taking your money and sending you a policy. Everything else requires customers to contact customer service — which we all know can be… painful.

That sucks. So, in the last couple of months we’ve been working hard on the second phase of our policy, turning it into a "live" document that can easily be modified without involving an agent!

With Live Policy, Lemonade customers (existing and new) can make changes to their coverages and more, whenever and wherever they are! It’s actually easier to change your Lemonade coverages than it is to pay for your latte. Just open our app, go to your policy and start playing with stuff!

Here’s a list of things you can now do with your existing policy:

  • Change deductible
  • Change personal property limits
  • Change liability limits
  • Change loss-of-use limits
  • Change limits for medical payments to others
  • Add/remove your significant other
  • Add/remove spouse
  • Add/remove landlord
  • Add/remove property manager
Why are we the only ones doing this?

Moments like these are the reason why we chose the hard way - becoming a real insurance company. It would have been a walk in the park to slap on some pretty UX over a centuries-old insurance carrier.

But we started from square one and built an insurance company from the ground up to address the very issues that turn people away from insurance. Doing so takes more than changing the way we market insurance, or even changing the very business model of insurance. It requires a dynamic focus on the issues our customers - and every insurance customer - face every day. It requires a commitment to tackling pain points, even (and especially) when it means questioning precedent.

See also: The Most Effective Insurance Policy  

This exciting new update is a part of a series of new features we’ll be releasing in coming months that will make insurance even more enjoyable, affordable and instant.

This post was originally posted on the Lemonade Blog


Shai Wininger

Profile picture for user ShaiWininger

Shai Wininger

Shai Wininger is a veteran tech entrepreneur and inventor, who most recently co-founded Lemonade, a licensed insurance company powered by artificial intelligence and behavioral economics. He previously founded Fiverr.com, the world’s largest marketplace for creative and professional services.

6 Pitfalls to Avoid With Core Systems

Good executives and project managers minimize the risk of failure by going into implementations with eyes peeled for problems.

In spite of the fact that shiny insurtech objects have distracted some insurers from strategic core system (policy, billing, claims) replacement projects, many are moving forward with planned large-scale modernization initiatives. If the implementations were not complex enough already, the rip-and-replace of aging core systems must extend insurers’ capabilities toward full digital transformation and open the door to integrations with insurtech innovations, as well. Good executives and project managers minimize the risk of failure by going into implementations with eyes peeled for problems. These individuals plan for overcoming implementation pitfalls, because such risks can lengthen timeframes, create cost overruns or even derail the entire initiative. Here are six pitfalls to watch for: The Talent Crisis While insurance companies employ talented people who know the business and the company’s products intimately, many are not prepared for large projects, such as core system replacements, which typically occur only every 10 to 12 years depending on budget, company culture and the organization’s need for change. The significant time between such projects allows for turnover in key insurer team members and means that remaining, inexperienced insurer employees are often caught off guard by the project’s complexity. Clearly defining roles, responsibilities and time or additional resource requirements in the project planning process is critical for insurers’ success. See also: Change Accelerates in Core Systems   Documentation Deficiencies Documenting project requirements and specifications and gathering form examples can be very time-consuming, so, when it comes to documentation, shortcuts are often taken or the process is rushed. Even though most vendors have templates to aid in the process, insurers’ employees must aggregate all existing forms, notices, reports, rating algorithms, billing plans, dropdown boxes or picklist values, file formats for interfaces and a list of user permissions, as well. While the impulse to skimp on upfront documentation can be tempting (and understood), as the user acceptance testing process begins, the payback for a job done well here will become apparent. Extended Project Parameters Core system replacements are complex and touch virtually every area of insurers’ organizations, and, unfortunately, the duration of the project is typically long enough that business requirements can change during the implementation. An insurer’s necessary product refresh adds additional scope and risk to the replacement. Designing a new product, validating it, acquiring department of insurance approval and developing new integration points that may require additional contracts are some of the risks that can add cost and time to a core system replacement project. Resources may be required to manage these new, but needed, items, and new requirements may compete with other project priorities or strategic company objectives. It is hard to predict the domino effect caused when one change inevitably provokes another. That said, insurers may want to consider planning to undertake such changes to existing lines of business after the first line has been put in place and the new business processes have been vetted. This will help keep project momentum going and keep the timelines in check. Third-Party Integrations The ability of modern systems to seamlessly interact (interface or integrate) with third parties is a key business driver for updating core systems. Insurers often use implementation projects to introduce integration with new third-party solutions to improve operational efficiency and automation. The risk of doing this is when it takes longer than expected to finalize the relationships with the third parties. The delays hurt the project timeline and jeopardize related downstream project dependencies. Insurers can benefit by building extra time into the project plan for firming up any new third-party relationships. Data Conversion Conversion of historical policy data is an important aspect of core system replacement projects, which, in theory, seems simple. In practice, however, data conversion is a complex process that can be approached from innumerable directions and can cause as many problems as it solves if not done correctly. Many smaller companies opt to manually convert data, but larger insurers usually require an automated conversion as part of the project specifications. An insurer’s historical data requires verification and cleansing before it is usable for an accurate conversion, and the effort is successful based on the quality of the original data and the ability to make decisions about how to handle anomalies. Once the data is cleansed, it needs to be normalized or formatted to the new system specifications, and this usually involves some manipulation. At the end of the day, no insurer ever says data conversion was easier than originally thought. But this may be a result of vendors ensuring the data going into the replacement system is well validated and of high quality, which ultimately requires more effort on everyone’s part. The Customization Curse With data conversion running a close second, the biggest risk to a core system replacement project is extensive customization. All projects require some level of customization, but the impact of heavy customization can be catastrophic today, as well as down the road. Modern systems are developed to deliver preferred workflows and best practices. Customization inevitably leads to scope creep (for insurer and vendor alike), which hurts project timeframes and adds cost. Customization has another potentially negative side effect as deviations from standard configurations often make future upgrades more complex or impossible. Often, insurers find the cost and effort to upgrade highly customized systems unjustifiable. If an insurer requires extensive customization, it might be because business processes are out-of-date, or are in place due to legacy system limitations (paved cowpaths). So, actually accepting the ways the new system was designed to handle critical processes could save a lot of future pain if the insurer in question is willing to manage some level of process change. See also: Core Systems and Insurtech (Part 1)   It bears mentioning here that there are natural traps into which vendors or solution providers can fall, as well, and that will affect the potential of project success. However, if a vendor has performed multiple implementations successfully, there should be an efficiency inherent to that experience that will help avoid bad consequences. While it is not possible to foresee all of the challenges associated with a major IT initiative such as a core system replacement, it is worth understanding the basic tenets of the most common implementation pitfalls and taking measures to mitigate the associated risks. Taking precautions will go a long way in helping a core system implementation come in on-time and on-budget.

Scott Hinz

Profile picture for user ScottHinz

Scott Hinz

Scott Hinz is the director of sales and marketing for Innovative Computer Systems, developer of the Finys Suite for property and casualty insurance organizations writing personal and commercial lines.

Why Buy What You Don’t 'Get'?

A key question is emerging: “How can we illustrate and model insurance value to generations that may not grasp insurance?”

||
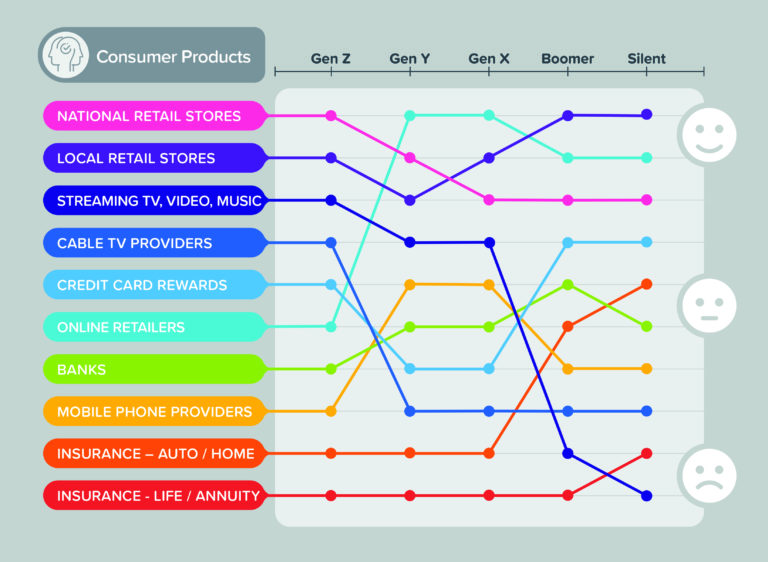
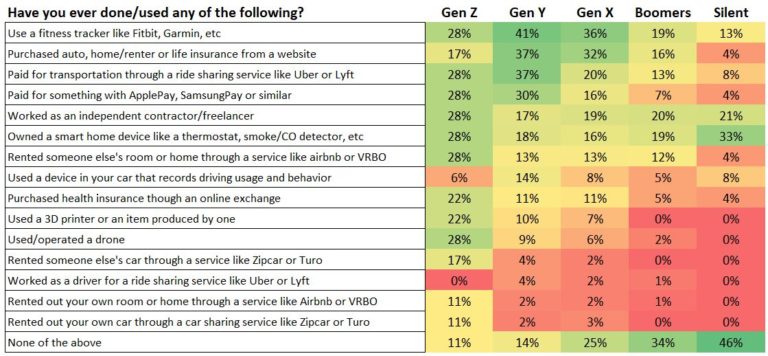
It sounds like a riddle, and in some ways it is. When it comes to insurance customers: If they don’t “get it,” they won’t get it. If they don’t see the need, they won’t need it. We can’t value our experience if they can’t experience our value. Let’s dig a little deeper. Much has been said recently about the customer experience. It’s a board-level topic. Everyone knows that it is important. We are busy transforming experiences, journey mapping and “digitizing” our organizations. Too much of what we are doing, however, is a frenzied reaction to a market scare instead of a thoughtful reaction to reality. We are afraid that new generations aren’t interested in insurance, and we are petrified that if they do see the need they won’t reach us through our pre-digital age channels. This is all true and valid. But if we operate solely upon these premises, we’re going to miss the meat of the issue. The customer experience is important, but it works hand in hand with a general understanding about the need for insurance and how insurance works. As attention spans narrow, demographics shift and insurance needs morph into new risk areas, the customer experience must include thoughtful ways of injecting insurance precepts into new methods for consumers to research and learn about what insurance does. If they “get it,” they’ll get it.  If they see the need, they’ll need it. And they will value our experience if we can help them experience the value. Because technology now plays a role in all facets of insurance experience and education, it may be helpful for insurers to have their own deeper understanding of the shifting nature of insurance researching, buying and servicing. For our lesson, we’re going to turn to the customer so that we can grasp the customer perspectives on purchasing insurance within the context of the full customer experience. As we step into the digital age, we want to be walking in their shoes. See also: Is Insurance Like Buying Paper Towels?   Perspectives Majesco conducted some primary research last year with consumers and small to medium-sized businesses, to find out where the insurance industry stands in their eyes. The goal was to document their perceptions so insurers could use the insights to craft new experiences that would meet and exceed expectations. One of our key findings was that insurance is perceived as too confusing. Did insurance just become confusing, or did we lose sight of the customer? Who moved? Insurers’ primary focus has been on the product.  Services were those things we did to support the product, such as underwriting, billing, and claims. A few services might be offered with the product, like roadside assistance, but for most products that has been rare.  As a result, insurance is an intangible, and, to the customer, intangible can be unintelligible. In insurance, customers pay for a protective concept, not a physical asset. Traditionally, the agent or broker’s job was to explain and reinforce the value of insurance to the insured, helping him to “get it.” Peace of mind was sold as an actual product. You could have peace of mind that insurers would make you “whole” if your home was damaged, you were in an accident or if a death occurred, to help cover the needs of the family. Majesco found in its survey that the greatest understanding in insurance was among those in the Silent Generation – many who bought into the traditional “peace of mind” product. But confusion rapidly grew in the younger generations. Many have predicted the demise of the agent and broker channel. Many other industries have eliminated that layer and are seeing success. Retail sales, for example, are shifting and thriving online. Banks are still relevant, driven by apps that keep customers in touch with their money. But insurance, the way it was designed, sold, serviced and understood by the Silent generation, doesn’t resonate with Millennial and Gen Z — generations that may value the concept of insurance protection but don’t understand how it works or why it is so difficult to research, buy and service. Businesses and insurance have their own corresponding issue. Small and medium-sized businesses (SMBs), increasingly led by Millennials and Gen X, don’t necessarily see or understand how insurance companies can best serve them. They also see the insurance process as confusing and lacking in value. For both individuals and businesses, there is a double-whammy — they are legally bound to carry home, auto and property insurance (and other lines in the case of SMBs). Right or wrong, they may resent being forced to pay for intangibles that provide little perceived value and have a not-so-great experience. A successful claims experience can change that perceived value, helping them grasp the benefits of adequate protective cover. But that may not happen for a long time … so the quest for value and relevance stays alive. Today’s customers are looking for organizations that give them a product that makes sense in light of the measures that they may take to protect themselves. In both cases, consumer and SMBs, business models, products, processes and systems were built for earlier times – for the Silent and Baby Boomer generations. But the generations coming up behind them need something that is relevant in the digital age, where there is a vast difference in needs, demographics and expectations. Improving the experience — What goes around, sometimes falls off The cycle of insurance, where we met each new generation with a simple variation on the products of the last generation isn’t going to work. Majesco found that none of the three categories (Researching, Buying & Renewing and Service) could claim to produce great insurance experiences across the industry. See also: Are You Buying the Wrong Leads?   The goal, then, is to build compelling customer experiences and to let some of the old fall off. There will be parts of the customer experience and process chain that will no longer be needed. There will be others that you cannot live without. In the coming weeks, we are going to have multiple blogs on customer journey improvement. You’ll want to listen in on these because they come from some of Majesco’s top experts on insurance experience. But for now, we’ll leave you with four overarching themes.
  1. As you answer the technical questions of customer experience development and digital transformation, don’t forget to ask the basic questions, such as, “How can we illustrate and model insurance value to generations that may not grasp insurance?” Remember, when they “get it,” they’ll buy it.
  2. Make sure all the different parts of your company that serve the same customer work together to create an experience that is easy, compelling, consistent and satisfying across all of the components. It requires a shift to journey thinking … not functional thinking and will require new teams and collaboration.
  3. Younger generations may not understand insurance, but they definitely understand technology. Don’t just meet them where they are, but speak their language. They are living with a new set of experiences across an alternate universe of risks. Use the technology to instruct and protect, and you’ll be reinforcing the value of the relationship, not just the value of the product.
If you want to get a glimpse into the use of technology within age groups, see the generational chart below.
  1. You can’t rebuild your customer experiences in a day. Review your customer satisfaction data to find the parts of your experience that are high in importance but lower in performance to help you prioritize where to begin. Then work on these areas, but make sure you have a plan for improving all of the other parts of the experience as well.
For a deeper look at consumer and SMB perceptions regarding insurance, download the Majesco’s research reports, The Rise of the New Insurance Customer: Changing Views and Expectations and The Rise of the Small-Medium Business Insurance Customer: Changing Views and Expectations.

Denise Garth

Profile picture for user DeniseGarth

Denise Garth

Denise Garth is senior vice president, strategic marketing, responsible for leading marketing, industry relations and innovation in support of Majesco's client-centric strategy.

Finding Data’s Proper Role in ERM

Increasingly, leaders are looking at other risks, which have not been measurable or predictable in the past, but are becoming more so.

As we collect more data, and become more sophisticated within our use of analytics, we can understand, manage and mitigate more emerging risks than ever before. In turn, our better-informed outlook changes how we approach risk. Instead of considering individual incidences, we now have the data to think about and build new approaches to understanding overall risk – including mitigation and management strategies. Enterprise risk management (ERM) provides a framework for understanding and responding to business uncertainties and opportunities with relevant insights that are delivered through common, integrated risk identification, analysis and management disciplines. Approaching ERM with analytics can provide a more strategic approach to holistically identifying, managing and mitigating risks. As a result, business leaders are not only looking at specific elements of risk anymore. It’s not just about single claims, like medical malpractice, which can be easily priced from an insurance perspective. Increasingly, leaders are looking at other risks, which have not been measurable or predictable in the past, but are becoming more so. When assessing the risk of, for example, property damage, risk managers have decades of data to draw on, data like incidence rates or average claim size, which helps model exposure profiles. Emerging risks, precisely because they are new, do not have this data. Emerging, big picture risks such as cyber security, damage to brand and reputation and supply chain are among the most pressing concerns that risk professionals face today. Few industries exemplify this better than healthcare. In Depth Why Healthcare? In healthcare, data has been critical in the education of practitioners and the treatment of patients – it has provided the necessary information needed to establish best practices and clinical protocols and provided the metrics that help increase the quality of care provided. Data can also predict, and even affect, medical costs. Across the globe, medical costs are rising. In the U.S. alone, healthcare costs are around $3 trillion – accounting for 18% of national GDP. These costs are only set to rise as the effects of aging populations and changing lifestyles make themselves felt. Luca Franzi De Luca, vice president, Aon Italy, says: “The state of healthcare is a truly global concern. More than ever, care providers need new ways to manage the costs – and risks – that coming years will bring.” Data will be key in addressing these issues. See also: The Current State of Risk Management   The Data Revolution and a Better Understanding of Risk The more parts of a system that you can observe – such as cost, quality, exposures to loss and population health – the more you can predict. And the more you can predict, the better you can understand, and price, risk. As such, ERM is becoming more of a possibility than ever before.
  • Risk control and traditional operational risks: From malpractice claims to workers’ compensation costs to property exposures, the healthcare industry now has decades of historical data that enables it to better manage and price risk. However, emerging risk poses a more severe problem: relatively new threats such as cyber attacks do not have the historical data behind them to give organizations a proper understanding of their exposure. And as healthcare – both data and actual care itself – becomes increasingly digitized, whether through back-end services like databases or digital infrastructure, or through frontline services like robotics and smart health devices, cyber will become more and more important. This is already happening. In 2016, healthcare was one of the most attacked industries because of the value of patient records. And as with malpractice or workers’ compensation, as more data is gathered for cyber risk, we are better-equipped to build risk models to address this emerging enterprise risk.
  • Population outcomes: One way for healthcare organizations to control their risk burden is to minimize the amount of illness in the world beyond their walls, and data is helping them to achieve this. For instance, big data, machine learning algorithms and better integration between public services is allowing more and more sophisticated forms of epidemiology and can help measure and control incidence rates in populations at large. This means a reduced risk profile for front-line care providers. “There’s a connection between keeping people healthy and enterprise risk. For example, malpractice claims will decrease if more and more individuals are healthy and not hospitalized,” De Luca explains. “Furthermore, analytics is enabling us to focus on 20% of the population that is driving 80% of the cost of care.”
  • Quality of care: Medical malpractice is estimated to cost around $55 billion cost in the U.S. alone. Improving the overall quality of care that individuals receive could reduce related costs. Data has enabled organizations to better understand their processes and eliminate the inefficiencies and errors that can lead to litigation.
  • Costs: Better data modeling processes can also give deeper insights into an organization’s total costs. For a hospital, keeping track of operating costs may be relatively straightforward. But other costs, such as those generated by supply chain risk, fluctuations in pharmaceutical or technology prices or business interruption from a cyber attack or pandemic, may be more difficult to grasp. Advanced data tools can give healthcare providers a better understanding of their total financial burden.
Data tells us about the world. The better we are at collating and analyzing data, the better we are at predicting how the world will behave. The use of data in the healthcare sector is providing greater visibility into all potential channels of risk – and also, new opportunities. Instead of looking at potential risks on an item-by-item basis, risk managers, senior management and the C-suite can start thinking about risk in macro terms. What is our organization’s total risk-bearing capacity? How does our current risk profile fit within that? And what strategies can we pursue to mitigate or finance those risks? Data technologies and methodologies are evolving all the time. Using these developments to gather and analyze more and more data around emerging risks is essential. This isn’t just important in the medical industry, but something that all industries can and must do. Only then will their strategies be able to deal with emerging, enterprise risk. “Organizations will be able to focus holistically on enterprise risk management, rather than focusing on specific liabilities as in the past,” De Luca says.

Dominic Colaizzo

Profile picture for user DominicColaizzo

Dominic Colaizzo

Dominic Colaizzo is responsible for managing and providing strategic direction as the chairman of Aon’s national healthcare practice and for directing and coordinating Aon resources for the development, implementation and servicing of alternative risk financing programs and broking for healthcare clients on a national basis.

How to Assess Municipal Threats

Start by putting the threats on a grid, with one bar being the likelihood of the exposure and the second being the potential severity of the risk.

At the 2017 PRIMA Annual Conference, a session discussed development of a municipal risk assessment program. The speakers were:
  • Dan Hurley – risk manager, City of Chesapeake, VA
  • Marilyn Rivers – director of risk and safety, City of Saratoga Springs, NY
A threat assessment is designed to determine vulnerabilities of employees to physical harm. Public employees are particularly vulnerable due to a variety of exposures. Understand Internal and External Threats When it comes to workplace violence, most people think this is primarily internal and involves a disgruntled co-worker. However, particularly with public entity employers, the main threats are external. Someone is disgruntled about something and acts out violently against the public entity employee. Domestic violence is also a significant source of workplace violence. The violence can spill into the workplace and affect not only the domestic partner but others around them. Among the public entity employees at greatest risk for violence are:
  • Public works/utility workers
  • Inspectors
  • Social workers
  • Home health aids
  • Animal control
  • Anyone handling money
  • Recreational staff
  • Emergency response
  • Law enforcement
  • Risk management
Any public situation that can be confrontational or stressful has the potential to escalate into violence. See also: IT Security: A Major Threat for Insurers   Identify Threats You should develop a threat committee to help assess potential threats for violence against your employees. Members of this should include:
  • Police
  • Fire
  • Social services
  • Human resources
  • Library
  • Public works
  • Public utilities
  • Recreation
  • Finance, risk and safety
  • City attorney
  • Code and licensing
  • Collective bargaining units
It can be challenging to bring all these different people together on the same committee as they have such a wide variety of experiences and interests. It is important that everyone feels they have a voice on the committee and that their views are heard. Each group on your committee has their own specific risk factors. For example, libraries are in a variety of neighborhoods. They are not heavily staffed, and they are open late into the evening. If there are homeless in the area, there is a tendency for them to look to libraries as a place of refuge. The leading cause of workplace homicide for women is domestic violence, with 32% of killings related to a domestic partner. Only 2% of men killed were due to domestic violence. This leads to the question of whether you should require your employees to notify you if they have a restraining order against another individual that would escalate the threat of violence. Prioritize Threats As threats are identified, the next step is to prioritize them. Start by putting the threats on a grid, with one bar being the likelihood of the exposure and the second being the potential severity of the risk. If you have threats that are high likelihood and high potential severity, those are your priorities. Potential priorities include:
  • Active shooter training
  • Emergency evacuation plans
  • Building security plans and building design for security
  • EAP
  • Work-alone procedures for both the office and field
  • See something, say something
  • Internet resource page
These priorities assist you in developing training and prevention programs to address your biggest risks. Active Shooter Training The standard now for active shooter response is RUN, HIDE, FIGHT. The first priority is to try and escape the situation. RUN Employees should be trained to think of what their escape path would be if faced with a shooter. People should have multiple options. You need an assembly point that is safe where employees can go and you can figure out who is missing. HIDE Train employees on places to hide. Can it be secured? Does it have good air circulation? An office with lots of cubicles can create very limited options both in terms of run and hide. FIGHT When you have no other options, be prepared to fight. Think of potential weapons you could use. Should you provide mace or tasers to certain employees who work alone and could be attacked? The stampede effect works best, as a shooter cannot target multiple targets at the same time. If one person attacks, others will usually join in. Announcing a police presence can also be useful, as many times active shooters kill themselves as police are closing in. Other Issues Building floor plans are a very important element of your active shooter program. You should provide building plans to local police and make sure those plans are updated as modifications are made to the building. See also: Protecting Institutions From Cyber Risk FEMA has online active shooter training programs that are very detailed and can be downloaded. Other Security Issues
  • Periodically do walk-around inspections of your secured locations to make sure they are properly secured. Too often, employees prop doors open, especially around loading docks, cafeteria rear doors and smoking areas. The easiest way into your secured building is usually the back.
  • Another area to check is the lighting around your building. Lights go out. Trees and bushes may grow to block lights or security cameras.
  • Keypad locks can be a problem, as you need to change the combination every time you have employee turnover. Card swipes are much better.
  • Police vehicles are a deterrent. Just parking their vehicles in a visible place aids in discouraging violence.
  • Open access counters are necessary for public access, but they sometimes lack a retreat barrier. Make sure you have cameras in the area and ample panic buttons for employees.
  • Having a security camera with a big screen facing outward can be a deterrent. People see themselves on camera, which can deescalate the situation, as they know they are being watched.
  • Safe rooms need to have the ability to withstand time. Perhaps have water available in case people have to shelter in place for an extended period.
  • Work-alone people are vulnerable not only to violence but a personal medical emergency or serious workplace injury. Have a way to track those people.

Is Talent the Best Defense?

While staying ahead of innovation is a mantra for the tech sector, many industries have not ranked innovation slowdowns as a threat – yet.

Little wonder why so many CEOs have restless nights. Europe and the U.S. are facing unprecedented political uncertainty, technology is developing at a breakneck speed and even the world’s biggest corporations are not safe from social media backlash. Against this backdrop, Aon’s 2017 Global Risk Management Survey (GRMS) found that brand damage, economic slowdown, increasing competition and changing regulations were the top four risks. Meanwhile, disruptive technologies, failure to innovate and lack of talent are the threats projected to increase in severity in the coming years. Are businesses prioritizing the right risks? According to the survey, the tech sector is most aware of the threat posed by failure to innovate, and other industries can learn from their industry’s risk rankings. More and more industrial sectors are getting swept up in the “Fourth Industrial Revolution” – where everything from machinery and household appliances to robots are being connected to the Internet of Things (IoT). The tech sector’s current concerns are important: What is affecting it today will likely affect almost every other company in the years to come. In Depth The need to innovate – together with disruptive technology – are high priorities for the tech industry, according to the GRMS. While staying ahead of the innovation curve is a daily mantra for the tech sector, many industries have not ranked innovation slowdowns as such a prominent threat – yet. The failure to innovate and disruptive technology, coupled with attracting and retaining top talent, increasing competition and brand risk, will maintain the Top 5 status for the technology sector for the foreseeable future. These factors will also increase for other industries that are going through digitization and digital disruption. Innovate or Fade Away So why are other industries ranking innovation slowdowns as a lower priority? As regulators scrutinize the "sharing economy" and "peer to peer" businesses like Airbnb and Uber, perhaps companies in more established sectors believe it’s just the disrupters that are vulnerable to new legislation. Could the low ranking also be a symptom of the complacency among established firms that inadvertently enable disruptive organizations to flourish in the first place? After all, many big brands – from Kodak to Borders – have disappeared partly because they failed to see the bigger picture. Borders, the established book retailer, according to Time magazine moved in a different direction despite consumer trends: late to the web, invested in CD sales as downloads were gaining popularity, and more physical stores emerged as consumers moved to e-commerce. Additionally, Kodak, the firm that invented the first prototype digital camera, thought photo sharing was going to help the printing business. As it turned out, digital photo sharing was the new business, the Harvard Business Review says. See also: 3 Major Areas of Opportunity   Established businesses can fail to anticipate disruptive risks because they are too focused on protecting market share – even if they recognize the importance of adapting to newer consumer trends. And while these companies may understand the theory of disruption – identifying and anticipating customers’ needs and responding to them in new and more efficient ways – they can lack the skills to identify the most effective ways to turn theory into practice. Failure to innovate and meet customer needs has been ranked 6th in the last four Aon surveys, but is predicted to rise to number 3 by 2020. In just a few short years, this risk is projected to be the top risk in Asia Pacific, and number 2 in North America, as these regions continue to compete for top talent in everything from consumer electronics to renewable energy technologies. Understanding the Core of Innovation and Disruption Disrupters are shaking up traditional business models by meeting customer needs in a more efficient and responsive way. From taxis and hotels to the music industry and newspapers, established businesses in almost every sector are at risk from mavericks who have found better ways of doing things. These revolutionaries can be start-ups like Airbnb or Spotify, or blue-chip firms muscling in on a new endeavor, like Apple and Google joining the race to develop driverless vehicles. At the heart of this is data and analytics. The growing commercial value of data describing a user’s online behavior – the core concept set to revolutionize the way the world works – is also core to the rapid rise of players like Snap. But where tech firms excel at gaining insight into customer needs from detailed data analysis, not every company has yet to find out how to gather, interpret and successfully apply data to help enhance, or even transform, their own business models. This is why businesses should closely monitor the tech sector’s forward-looking concerns. Those who understand and anticipate emerging risks will have a stronger chance of overcoming them. The rest risk being overtaken by up-and-coming rivals who better understand both consumers and the rapidly changing business landscape. A failure to innovate and respond to customer needs can directly impact an organization’s bottom line. In the last 12 months, it led to a quarter of firms reporting a loss of income, more than from cyber crime and hacking (reported by 10 percent), or political risk (reported by 23 percent). Companies also report less preparedness to remedy the problem. Today only 59 percent report ‘readiness’ for dealing with this risk, down from 64 percent in 2013. All this shows that perceptions of risk are changing. With this change in perception comes a need for new approaches to overcome such emerging threats. And to develop those new approaches requires the right people. Talent: The Ultimate Solution? In 2011 Apple overtook Exxon Mobil to become the world’s most valuable firm. And now four of the top five companies in terms of market capitalization – Apple, Alphabet/Google, Microsoft and Amazon – are from the tech sector. Investors have put their faith in ideas and creativity as much as natural resources and physical assets. Meanwhile, Microsoft’s $26 billion acquisition of LinkedIn shows the enormous value of a company which had quickly become a dominant talent and recruitment networking tool. Since innovation reflects forward-thinking , attracting and retaining the right talent to implement such strategies might be a company’s best bet to stay ahead. And potential recruits need more than competitive salaries: They are after a strong brand with a good reputation and workplace flexibility that recognizes good work. For those with skills in fields like cybersecurity, big data and predictive analytics, it is a seller’s market as demand outstrips supply. There has been a global skills shortage in these areas for the last few years, and this remains a serious challenge. Add to this a tightening labor market as unemployment falls in major economies, and the potential strengthening of borders in the U.S. and the U.K., which limits talent supply even further, accessing top talent becomes a greater challenge. Despite an appreciation of the rising challenge of skills shortages, failure to attract and retain talent dropped from 5th in 2015, to 7th in the 2017 survey results. But again, technology firms – who tend to be ahead of the curve – rate it at number 3. Talent Beyond Tech Skills shortages are not just an issue for tech companies, even if other sectors may not yet fully appreciate the importance of talent in their business plans. For instance, failure to attract and retain talent did not appear in the Top 10 for the energy sector in this year’s survey. “From my point of view, this makes it an underrated risk for the sector,” says Bruce Jefferis, CEO Energy & Mining, Aon. “Historically, talent retention coupled with innovation has been a key driver for the energy sector and it will continue to be a key risk in the longer term.” See also: 4 Hot Spots for Innovation in Insurance   With the Fourth Industrial Revolution likely to affect almost every sector, other industries should start to take note. With talent pipelines increasingly needing to be planned as much as 10 years out, failure to start planning today could lead to even greater disruption in years to come.

Eric Boyum

Profile picture for user EricBoyum

Eric Boyum

Eric Boyum serves as a managing director and national leader of Aon’s technology and communications industry practice. This industry practice serves more than 1,400 clients representing over $1 billion in annual premiums. The ARS U.S. technology practice is one of our largest and fastest growing industry groups. In this role, Boyum leads Aon’s research, strategy and alignment of Aon core competencies in risk, health talent and retirement to meet the current and future needs of technology companies.

How to Determine Your Cyber Coverage

My advice is to lead from the top. Organizations' boards of directors need to ensure risk assessments are thorough and up-to-date,

Public agencies and organizations around the world are making cyber risk their top priority. North American policyholders dominate the market, but Europe and Asia are expected to grow rapidly over the next five years due to new laws and significant increases in targeted attacks, such as ransomware. Various experts predict the $3 billion global cyber insurance market will grow two-, three- or even four-fold by 2020. Deciding how much cyber insurance to buy is no inconsequential matter, and the responsibility rests squarely with the board of directors (BoD). Directors and executives should have the highest-level view of cyber risk across the organization and are best-positioned to align insurance coverage with business objectives, asset vulnerability, third-party risk exposure and external factors. See also: New Approach to Cyber Insurance   So, how much does your organization stand to lose from a supply chain shut down, a web site outage or service downtime? Recent data points from breach investigations help frame the discussion around risks and associated costs. Following a variety of high-profile breaches helps ensure that your projected coverage requirements match up with reality. Be sure to follow older cases for deeper insight into the full expense compared with insurance payout; related costs and losses are often incurred for years afterward due to customer and market response as well as legal and regulatory enforcement actions. In 2013, Target suffered a very public breach that resulted in the resignation of the CEO, a 35-year employee. Target had purchased $100 million in cyber insurance, with a $10 million deductible. At last count, Target reported that the breach costs totaled $252 million, with some lawsuits still open. Home Depot announced in 2014 that between April and September of that year cyber criminals stole an estimated 56 million debit and credit card numbers – the largest such breach to date. The company had procured $105 million in cyber insurance and reported breach-related expenses of $161 million, including a consumer-driven class action settlement of $20 million. These cases illustrate the need for thoughtful discussion when deciding how much breach insurance to buy. Breach fallout costs depend on multiple factors, are not entirely predictable and can rise quickly due to cascading effects. Cases in point: the bizarre events surrounding Sony’s breach and the post-breach evisceration of Yahoo’s pending deal with Verizon. Organizations need to review their security posture and threat environment on a regular basis and implement mechanisms for incessant improvement. The technology behind cyber security threats and countermeasures is on a sharp growth curve; targets, motives and schemes shift unpredictably. Directors may find it useful to assess risk levels and projected costs for multiple potential scenarios before cyber insurance amounts are decided upon. Most policy premiums are currently based on self-assessments. The more accurate the information provided in your application, the more protected the organization will be. Most policies stipulate obligations the insured must meet to qualify for full coverage; be sure to read the fine print and seek expert advisement. A professional security assessment can pinpoint areas in need of improvement. If you claim to be following specific protocols, but a post-breach investigation finds they were poorly implemented, circumvented or insufficiently monitored, the insurer may deny or reduce coverage. Notify your insurance provider immediately about significant changes to your security program. Review policy details regularly to ensure they match prevailing threats and reflect the evolution of crimeware and dark web exploits. Cyber insurance carriers continually adjust their offerings based on risk exposure and litigation outcomes. See also: Promise, Pitfalls of Cyber Insurance   As the industry matures, cyber insurance policies will become more standardized. For now, it’s an evolving product in a dynamic market; boards and executives need to keep an eye on developments. Simultaneously, they must maintain a high degree of visibility across their security program. Checking off compliance requirements, writing policies and purchasing security software isn’t sufficient. My advice is to lead from the top. Organizations need to ensure risk assessments are thorough and up-to-date, policies are communicated and enforced and security technology is properly configured, patched and monitored. Turning a blind eye to cyber threats and organizational vulnerabilities can have disastrous consequences. Cyber insurance may soften the financial blows, but it only works in conjunction with an enterprise-wide commitment to security fundamentals and risk management.

Greg Reber

Profile picture for user GregReber

Greg Reber

Greg Reber is the founder and CEO of AsTech Consulting, a leading information security consulting firm. As a pioneer in the information security field, Reber was among the first to recognize and address the risks presented by consumer-facing applications.