Download

'It’s Life, Jim, but Not as We Know It' (Part 3)

Don’t just copy other life insurers; learn from the best-in-class companies outside your own sector and apply these principles to your own business.

The article below has been based on a keynote presentation delivered at the Euro Events Life Insurance & Pensions Conference in Amsterdam on Nov. 16, 2017. This is part 3. The previous parts can be found here and here. Summary of Parts 1 and 2 In the previous parts, we discussed that customers do not buy insurance because they like it, but because they have to or there is no better alternative available. We started by asking how you can turn a subject like insurance into something that customers actively engage in? Can, for instance, a pension become an urgent, relevant, integral part of our daily life? We discussed two options. The first option is to offer a broader, more relevant solution with insurance as a component. The insurance product becomes part of a larger, more relevant value proposition. Examples include integrated solutions for risk management and safety, health, housing, mobility or personal financial planning. The second approach to turn insurance into a product customers actually want to buy, is to reconnect with your customers. There’s still a big engagement gap between insurers and their clients. We touched upon a number of relevant concepts, including the Theory of Planned Behavior, the dynamics of inertia and financial anxiety. In this third and final part, we bring the insights from the previous parts together and wrap things up. The relationship between redefining and reconnecting Now, we know that current relationships between insurers and their customers can be improved. We’ve covered two different approaches to make life and pensions more attractive. We started off by investigating how insurance solutions can become better connected to the daily life of your customers. This is all about extending the value proposition with products and services. Logical themes are health, safety, housing, maintenance, mobility and personal financial planning. With these broader solutions in mind we then addressed the need to overcome inertia and financial anxiety to reconnect with our customers. This may give the impression that these approaches were distinct, separate activities. But they are in fact closely related. Consider this: if you successfully redefine your value proposition, you create new and meaningful customer touchpoints that help you finding better ways to reconnect with them. And as your ability to understand your customers grows, you learn more about preferences that help you to in turn to develop better value propositions. See also: Thought Experiment on Life Insurance There is work to do! These considerations will undoubtedly trigger a lot of questions among insurers. Are we going to be in the business of selling and administering policies or are we going to transform towards becoming a risk & income management expert? What will be our position in the value chain, what role are we going to play in this new extended eco-system? How can we develop these new concepts into a viable business model? And what kind of capabilities do you need to thrive in this new world of continuous change? Some key capabilities from existing insurers, like the ability to design and manage complex policy products, may become less relevant in a world demanding attractive risk management solutions. Similarly, having a true customer focus embedded in your organisational DNA is going to bring you further than having just a regulatory imposed customer orientation. Building these skills in an environment that is still dominated by different types of legacy is not easy. This is one of the reasons we see a rise in partnerships between existing insurers and Insurtechs. Organizing the transformation - the 7 habits of effective insurers So let’s assume that first thing tomorrow you plan to start to rethink how to design and implement a wider service proposition around your insurance core. What are some key principles to keep in mind when organizing the transformation? I am not going to try to summarize the many excellent books available on how to foster a culture that embraces organizational change and innovation. Let me just highlight a number of points from my own experience:
  1. Be very aware of internal bottlenecks and when increasing agility. Organizations have a tendency to become more complex and bureaucratic - not fit for purpose in the digital world. This could mean that to move fast, you first have to shed some weight and find a solution for your closed books or other legacy infrastructures.
  2. Start talking, not just with your customers but also with employees, distributors, partners, regulators, etc. It’s not just insurers that increasingly recognize the need for change – a full range of companies in the value chain are co-depending on a model that is increasingly under pressure. New business concepts will have impact on insurance value chain partners, and service and IT providers just as much (or possibly more!) as they will affect the insurers themselves.
  3. Don’t make the mistake of copying concepts from your fiercest insurance competitor, but learn from the best-in-class companies outside your own sector and apply these principles to your own business. Traditional industry boundaries and barriers to entry are rapidly shrinking, and the proper response is to enjoy and learn from the emerging panorama.
  4. I’ve always found that the scope and intensity of R&D within Financial Services is quite low, compared to other sectors. Now is the perfect time to change that. The rise of innovation labs is a step in the right direction but now we need to learn how to organize innovation at different speeds and for different aspects of a business model.
  5. While I perfectly understand why many insurers choose differently, my conviction is that insurers should organize innovation at the heart of their organization. I’ve heard many arguments why insurers choose to set up innovation in labs or outposts but there are serious limitations and issues when it comes to reconnecting with the main organization. That will be subject of another article. For now my summary is: get back in the building!
  6. Invest in your capabilities not just to start up but to scale up a new value proposition – that’s where it becomes really complex. Everybody can create a small scale working model, a MVP or a pilot project. But turning it into a large scale operation that contributes to revenues, that’s something else.
  7. And most importantly: If you’re 80% sure that your current business model is future proof (which means you are pretty confident about it!) you should still spend 20% of your change budgets on more fundamental, radical or disruptive types of innovation. Just make sure you’ve got all possible scenario outcomes covered!
In closing The time to repair the roof is when the sun is shining. Has that window of opportunity already passed by or will incumbents be able to adjust their course in time? It is only now, when we see rising costs of doing business, signs of diminishing returns and demographics putting pressure on existing products that we see emerging initiatives. Solutions for managing risks should become urgent, relevant, top of mind and connected to the daily life of customers. Insurers rethinking their value propositions have the opportunity to design a new generation of solutions beyond a singular insurance policy that will transform their relationship with customers. These solutions will have to overcome the key psychological challenges relating to certain or possible events that may be far off in the future. Applying advanced insights and techniques (from the fields of behavioural science, neuromarketing, and applied psychology, etc.) to reconnect with customers ensures that the future is becomes increasingly something that is clear and present and to be dealt with right now. If insurance becomes the means to an end as part of a broader customer need, you need to organize this transformation. It’s not just a product gap – it’s a gap between capabilities present and capabilities needed on different levels: organization, technology, application landscapes, culture: e.g. how do you combine a solid long term investment management function with short term entrepreneurial activities and innovation? See also: This Is Not Your Father’s Life Insurance   Corporate innovation and strategic change initiatives should fix a number of key existing internal challenges and create the right fundamentals to enable more disruptive types of innovation. The traditional product development scope needs to be enhanced to facilitate the creation of hybrid forms of products and services. Addressing these aspects will enable insurers to design solutions and services that bring us closer to their original marketing promise to provide more security and peace of mind.

Onno Bloemers

Profile picture for user OnnoBloemers

Onno Bloemers

Onno Bloemers is one of the founding partners at First Day Advisory Group. He has longstanding experience in delivering organizational change and scalable innovation in complex environments.

Cyber: No Protection Against Complacency

While data is considerably safer these days in the cloud, no cyberinsurance policy can substitute for active vigilance.

Cybersecurity insurance appears to be enjoying a heyday. While it’s been around for some time, the perceived need for it has never been greater, as DDoS attacks and major hacks grab headlines and fray nerves. As recently reported in The Hill, Lloyd's of London approximates that “average cloud service events of varying severity range from $4.6 billion in total damages for a ‘large’ attack to $53.1 billion for an ‘extreme’ one. In the vulnerability example, the average costs range from $9.7 billion for a large event to $28.7 billion for an extreme one.” Lloyd’s suggests that we ought to insure cyberattacks as we do natural disasters. Ransomware imposes its own sort of multiplier effect, measured in business loss, damage to reputations and (customer) privacy and, of course, in out-of-pocket outlays paid handsomely in Bitcoin. But in treating cybersecurity insurance as an essential check-off item for organizations, the last thing underwriters, businesses and consumers need is complacency. We rightly regard insurance as protection; we pay for it, and may or may not alter our behavior to actually diminish the threat of the event itself. And that’s the risk that insurance doesn’t mitigate against; indeed, it can aggravate it, by conferring on businesses a false sense of, pardon the term, security. Cloud security isn’t like filling out a job application; it’s not a matter of checking boxes and moving on. Piecemeal approaches to security never work. Patching a hole or fixing a bug, and then putting it “behind” you – that’s hardly the stuff of which effective security policies are made. Because security is a moving target, scattershot repairs ignore the hundreds or even thousands of points of vulnerability that a policy of continuing monitoring can help mitigate. And that insurance can address only after the fact of potentially catastrophic loss. See also: 2018 Predictions on Cybersecurity  Cloud security policies must be in place before, during and after the ink is dry on any cybersecurity insurance policy. Any cloud provider worth its salt brings to the task a phalanx of time-tested tools, procedures and technologies that ensure continuous uptime, regular backups, data redundancy, data encryption, anti-virus/anti-malware deployment, multiple firewalls, intrusion prevention and round-the-clock monitoring. So while data is considerably safer in the cloud than beached on equipment under someone’s desk, no cyberinsurance policy can substitute for active vigilance – accent on active, because "vigilance" is definitely a verb. Absent both the right mindset and proper policies and guidelines, cybersecurity insurance can prove pointless. About that mindset: Sound security planning requires assessing threats, choosing tools to meet those threats, implementing those tools, assessing the effectiveness of the tools implemented – and repeating this process continually. Security is a process, not an event. On the premise that the best defense is understanding the real nature of the offense – or, in this case, offenses, because cybersecurity insurance addresses a multi-front battleground – it may be helpful to think in terms of a basic four-tier model that defines the broad steps businesses can take to maximize their safety. With that model, it’s possible to match the level of protection to the class of threat a given organization faces. Users need to be familiar with online threats and at least somewhat conversant with tools to arrest them; no single system can circumvent vulnerabilities that haven’t been patched. Below, this prototypical four-level gauntlet: First line of defense: The first line consists of a firewall supported by intrusion detection and prevention technology, along with anti-virus and anti-malware software, which is limited to blocking items downloaded over unencrypted protocols. Second line of defense: The second line centers on the trained, educated user – someone sufficiently cognizant of threats to think before executing a link or downloading an attachment: a user, in other words, who is attuned to the real and present danger inherent in viruses and malware, and who acts accordingly. Third line of defense: The third line is composed of patch management and locally installed anti-virus and anti-malware software, working together to effectively block attacks. Proper implementation of third-line defense means fewer bugs and optimized performance. See also: How to Eliminate Cybersecurity Clutter   Fourth line of defense: In the event that malware or ransomware hits a system, it’s possible to restore the server via application-consistent snapshot technology on a storage area network, a rollback process that takes just minutes and restores the server to its exact state prior to the attack. It may be helpful to treat these lines as concentric circles. Remember that the human element remains the most important social engineering piece of this construct. It’s always best to stop a problem early, before it festers and productivity suffers; think smoke detectors vs. sprinkler systems. And just as regular brush clearance in fire zones is a necessary precursor to maintaining fire insurance coverage, so these measures prepare businesses for cybersecurity insurance – and underscore the wisdom of making that purchase.

Adam Stern

Profile picture for user AdamStern

Adam Stern

Adam Stern, founder and CEO of Los Angeles-based Infinitely Virtual, is an entrepreneur who saw the value of virtualization and cloud computing. Stern’s company helps businesses move from obsolete hardware investments to an IaaS [Infrastructure as a Service] cloud platform, providing them the flexibility and scalability to transition select data operations from in-house to the cloud.

Formula for Creating a Positive Risk Culture

It makes sense that insurers should be excellent at managing their own strategic, financial and operational risk. But is that always the case?

The insurance industry is all about understanding and taking risk prudently. In other words, it is about assuming risk from individuals or organizations for the right return. Thus, it makes sense that insurers should be excellent at managing their own strategic, financial and operational risk. But is that always the case? Regulators and rating agencies have done a great deal to require robust enterprise risk management at insurance companies and to consider how well they are implementing it in evaluating them. However, their focus is decidedly on capital risk management and to a much lesser extent on other risk categories. Yet, other risk categories can certainly affect financial stability. Are insurers being asked to show regulators and rating agencies how they have measured their risk culture? Are they asked to explain to what extent their strategies have been influenced or revised based on risk-related input? Likewise, is there inquiry into how deep within the insurers’ ranks the risk-identification process goes to gather input? Is there much questioning about how financial targets are set, such as whether non-management or field input is gathered before setting these targets? If the answer is no, then some vital evaluative data is being missed. That is because risk culture, and the things that strongly influence it, can make a huge difference in the financial success or failure of an insurer. What Is Risk Culture? There are various definitions for it, but the best I have found is the one suggested by the Institute of International Finance, “‘Risk culture’ can be defined as the norms and traditions of behavior of individuals and of groups within an organization that determine the way in which they identify, understand, discuss and act on the risks the organization confronts and the risks it takes.” See also: Building a Risk Culture Is Simple–Really   The prevailing risk culture can be one explanation for why some insurers have more negative surprises than others, or why some have a poor track record for reserve increases whereas others do not. or why some experience adverse results from significant growth whereas others can do so profitably. What Influences Risk Culture The things that influence risk culture and help to create a risk-aware culture are:
  • Message from the top – board, CEO, senior team
  • Behavior at the top
  • Existence of board and management-level risk committees
  • Existence of risk appetite, risk tolerances that are well-communicated
  • How far down in the organization risk identification methods delve
  • How unauthorized/excessive risk-taking is handled by management
  • Whether there is a risk reporting hotline
  • Whether goals are aligned with risk appetite and risk tolerances
  • Whether incentives are aligned with risk appetite and risk tolerances
  • Whether risk culture is measured
How Management Behavior Can Create Risk and Block Risk Culture There are many ways that management can contribute to a poor or non-existent risk culture. Below are just a few examples. By setting unreasonable goals, management creates obstacles for a healthy risk culture. There is a difference between stretch goals and unreasonable ones. Good managers know this and know how to set a proper goal. Unreasonable goals beget unreasonable behavior, e.g. risky behavior. Such behavior might play out in underpricing business to meet a premium growth goal; it might play out in bad faith claims to meet an average paid loss goal. These things can happen in any environment but are more likely when goals are set too high and the risk associated with that is ignored. Another management action that can produce risk is developing a strategy without input from the field. A strategy that is based only on the ideas in the corporate suite can lead to the risk of failure or the risk of producing negative or unintended consequences. For example, field staff may have more insight about how a change in compensation practices or local contacts may be reacted to by agents and brokers than home office strategy pundits. Getting field input might avoid losing business, losing agents or brokers or some equally undesirable business result. In a study sponsored by the Casualty Actuarial Society, the authors Shaun Wang and Robert Faber state, “In running an enterprise, it is essential to recognize both global and local views: Without inputs from the field, any development of business strategy lacks a solid footing; while the strategic directions are set at the company level, the success and failure of the strategy depends on the local business execution.” Insurers are introducing many types of innovations into their operations to stay relevant in today’s digital world and sharing economy. If it is perceived that management is not taking into account the risks inherent in any new way of doing things, then a strong signal is being sent to the rest of the organization. The signal is that managing risk is not always important. Taking risk into account should never stop forward movement. Instead, it should ensure that innovations are optimized. Management should be able to point to the risks that were identified and how they were addressed, regardless of whether those risks pertain to cyber security, system integration, scalability, customer or distributor satisfaction and any number of other matters. See also: A New Paradigm for Risk Management? How Management Can Create a Positive Risk Culture Management’s behavior becomes the model for the rest of the organization. Generally, each level of management tends to mimic the approach of the level to which it reports. Even when such cascading is not perfectly distributed, the overall tone and modus operandi of top managers tend to influence most employees of the organization over time. Thus, management must be continually aware of what message it is sending about risk awareness by its own actions as well as by designed communications. Where a risk-aware culture is nurtured, there will be many ways in which management reinforces it:
  • Rewarding staff when risks are handled well and holding staff accountable when risks are not handled well
  • Ensuring that risk is discussed during decision-making not after decisions are made
  • Treating those who report a risk as a team player rather than a naysayer or trouble seeker - encouraging the person to become a problem solver by being asked to help address the risk
  • Discussing risk and the status of risk mitigation plans in staff meetings or whenever appropriate.
In risk-aware cultures, risk is considered as part of every key decision or action. Thus, the bottom line is improved.

Donna Galer

Profile picture for user DonnaGaler

Donna Galer

Donna Galer is a consultant, author and lecturer. 

She has written three books on ERM: Enterprise Risk Management – Straight To The Point, Enterprise Risk Management – Straight To The Value and Enterprise Risk Management – Straight Talk For Nonprofits, with co-author Al Decker. She is an active contributor to the Insurance Thought Leadership website and other industry publications. In addition, she has given presentations at RIMS, CPCU, PCI (now APCIA) and university events.

Currently, she is an independent consultant on ERM, ESG and strategic planning. She was recently a senior adviser at Hanover Stone Solutions. She served as the chairwoman of the Spencer Educational Foundation from 2006-2010. From 1989 to 2006, she was with Zurich Insurance Group, where she held many positions both in the U.S. and in Switzerland, including: EVP corporate development, global head of investor relations, EVP compliance and governance and regional manager for North America. Her last position at Zurich was executive vice president and chief administrative officer for Zurich’s world-wide general insurance business ($36 Billion GWP), with responsibility for strategic planning and other areas. She began her insurance career at Crum & Forster Insurance.  

She has served on numerous industry and academic boards. Among these are: NC State’s Poole School of Business’ Enterprise Risk Management’s Advisory Board, Illinois State University’s Katie School of Insurance, Spencer Educational Foundation. She won “The Editor’s Choice Award” from the Society of Financial Examiners in 2017 for her co-written articles on KRIs/KPIs and related subjects. She was named among the “Top 100 Insurance Women” by Business Insurance in 2000.

How to Improve 'Model Risk Management'

An essential starting point for insurers initiating an MRM program is to develop an inventory of their models.

Model risk management (MRM) continues its rapid growth in the insurance sector. More insurers are adopting MRM programs and are looking to increase the efficiency and effectiveness of existing programs. Developing and using an effective MRM system will promote better MRM performance. A basic MRM system should provide a platform for managing MRM activities, in particular tracking and managing validations. As insurers accumulate information about their models through scoring and validation processes, we believe that they can enhance their systems to gain beneficial insight across their model inventory, especially commonality of components and interactions between models. Based on recent client work and recent industry surveys, we share below some thoughts on the key characteristics of an effective base platform, cross-inventory opportunities, and how risk managers can enhance MRM processes and systems to take advantage of these opportunities. Basic characteristics of an MRM system An essential starting point for insurers initiating an MRM program is to develop an inventory of their models. Because MRM programs typically encompass all of an insurer’s models (not just actuarial or risk or financial ones), the inventory can be quite large. A survey we conducted early last year indicated that more than half of respondents had more than 150 models in their inventory; a quarter had more than 450. Another survey we conducted later in the year found that MRM systems’ primary task at all insurers is to catalogue all these models. Once catalogued, an obvious next step is to populate the system with information that helps manage the MRM process. Typically, we see the following functionality in effective systems: 1. Model documentation repository. Model documentation is the starting point to conducting a validation. Providing access to that documentation is important for validation and continuing risk management of the model. Sometimes (typically for older models undergoing their first validation), comprehensive documentation is not available and needs to be developed. Sometimes validations point out the need for documentation to improve. Keeping track of the need to update validation either because it is inadequate or because the model has changed also should be a part of the systems’ functionality (see item 4 below). 2.  Model validation document repository. This is the most self-evident functionality. Ninety percent of respondents in our survey who had a multifunction system (i.e., systems that do more than just catalogue models) reported that it was a repository for validation or model documentation. Also of importance, as programs mature, the system needs an appropriate mechanism to update the repository with documentation from subsequent validations (presumably without losing earlier versions). See also: Changing Business Models, ‘New’ ERM   3. Model risk scoring repository. Though not as universal as documentation storage, storing model risk scores and the details about the model that were used to develop its score is a feature present at about two-thirds of surveyed respondent companies. Model risk scores are often used to prioritize and sequence validations, so the first score is likely developed before the model is validated. Not surprisingly, validations often shed new light on a model and can often lead to a change in score. Also, we have found some insurers have begun to revisit their earlier scores and scoring algorithms, often placing greater emphasis on models that permanently affect cash flow. The system should be capable of tracking the development of the model’s risk score because it may change over time. 4. Tracking findings needing attention and due dates for that attention. Managing hundreds of models is likely to lead to an extensive list of findings needing attention. Keeping track of these, the party responsible for addressing them and their expected completion dates seems a natural choice for an MRM system feature. As models are being built or undergoing significant modifications, the system can be used to keep track of their progress and validation needs. 5. Emailing notification to model owners and others of coming or missed tasks. It seems a short step from tracking as we describe above to emailing notifications and follow-ups, as required. Our survey showed that only slightly more than half of the multifunction systems have this functionality. 6. Reporting. As with any process, reporting on MRM activity, particularly the progress of validations and issue resolution, is a necessary antecedent to managing the process. About three-quarters of the respondents have this functionality built into their system. Though only a few have developed this as a real-time reporting dashboard, the rest are working on this or planning to do so. Cross-inventory commonalities and connections Recognizing that MRM is still a relatively new program at many insurers, early emphasis has been on developing a system that supports initial validation efforts. However, as programs mature and systems’ basic functionality has been established, insurers should consider enhancements that could increase the overall value of their MRM program. We believe these enhancement opportunities come from better using the information in the system. In particular, they come from working across the inventory rather than one model at a time. Different models are likely to have many assumptions in common. The system could compare assumptions across models in the inventory. If two models use different values for the same assumption, for example different values for future interest rates, it would be instructive to investigate the sources and implications of these differences. Potentially, differences are not appropriate and, if not corrected, could cause increased risk across the model inventory. A single-source model for this assumption could apply to all cases, thus reducing overall modeling costs. Different models frequently use common parts. For example, both stress testing and ALM models may use common cash flow projection engines. Although both models should undergo their own validations, some elements of the work can be reused. In particular, with proper safeguards, multiple replication of the same calculation algorithms would be unnecessary. Often, the replication element of a validation is one of the most resource-intensive and costly aspects of the work, so avoiding duplication here could meaningfully improve efficiency. Few if any models exist completely on their own, isolated from others in the inventory. Typically, models are fed some input from upstream models and often send some output downstream to other models. This web of connectivity can be hard to visualize, but the raw material for doing so could be available from the MRM system. Typically, systems will need some enhancement to allow insurers to mine this material, however. Enhancing the system to enable cross-inventory gains The next significant step in MRM’s development can come from a holistic look at the whole model inventory. Some process and system enhancements that can enable cross-inventory perspective include: 1. Model documentations standards. Most insurers have developed a playbook or template that they expect validators to follow in conducting validations and completing validation documentation. It is not often though that we find the same attention to standards in documenting models. Standardization can benefit both the model documenters and MRM cross-inventory analysis. 2. Terminology standards. Because many different model owners and users have developed models independent of each other over several years, it’s not surprising to encounter inconsistent terminology. Different terms often describe the same thing, and sometimes the same term describes something else. As the MRM system becomes more densely populated, a thorough review can identify inconsistencies and enable greater standardization. 3. Upstream and downstream precision. Many validation report guidelines (and presumably good model documentation guidelines) require identification in input and output of upstream and downstream models. It would seem a modest step to require that these identified models are cross-referenced to their place in the inventory, presumably using the same model number identification tag. See also: Top 10 Insurtech Trends for 2017   Next steps for insurers Insurers should bring their MRM systems up to baseline capabilities by enabling the functionalities we describe above. As validations and model risk management activities populate the MRM system, insurers should use that information to standardize model documentation formats and develop consistent terminology. Model and validation documentation should reference upstream and downstream models using the system’s identifiers. Insurers can then mine information contained in their MRM system to:
  • Ensure consistency where required,
  • Eliminate duplicative validation tasks and,
  • Map their model web, eliminating unused models, improving models that need updating and carefully nurturing and managing the models that are of greatest value to the organization’s success.

Michael Porcelli

Profile picture for user MichaelPorcelli

Michael Porcelli

Michael Porcelli is a director in PwC’s life actuarial services practice. He has 24 years experience as a life actuary spanning global banks, life insurance companies, reinsurers and consulting firms. At PwC, Porcelli’s main focus is risk and capital management and insurance capital market transactions. He joined PwC after serving as the head of model governance at a major multiline insurance company.


Henry Essert

Profile picture for user HenryEssert

Henry Essert

Henry Essert serves as managing director at PWC in New York. He spent the bulk of his career working for Marsh & McLennan. He served as the managing director from 1988-2000 and as president and CEO, MMC Enterprise Risk Consulting, from 2000-2003. Essert also has experience working with Ernst & Young, as well as MetLife.

How to Scout and Draw the Best Talent

Without modern technologies, you can’t court the best possible talent -- and you will see your bench strength continue to weaken.

The cycle of doing more with less is starting to catch up with the insurance industry. This year, 25% of insurance professionals are expected to retire, says David Coons, SVP of the Jacobson Group. Further, by 2020 the industry will need to fill approximately 400,000 positions to remain fully staffed. Even among the largest insurers, talent is a problem. Brian Duperreault, who joined a struggling AIG as CEO in May, drew a sports analogy to mind when he noted during the company’s Q2 2017 earnings call in August that he wanted to focus on rebuilding the insurer’s formerly deep bench of talent. “There is no question AIG lost talent, but it was also blessed with a strong bench,” Duperreault said. “The job now is to rebuild that bench.” To me, the “bench strength” analogy speaks to insurance leaders today from companies large and small who are responsible for keeping their “players” engaged, and ensuring every position on their team is filled or ready to be filled at any given point with capable talent, despite players dropping off the team for whatever reason. See also: 10 Insurtechs for Dramatic Cost Savings  February has been designated the 3rd Annual Insurance Careers Month, and it serves to remind us that, before we can fortify our benches with talent, we face a couple of uphill battles. First, the industry continues to suffer from false yet pervasive negative perceptions. People mistakenly tend to think that the typical insurance company’s value proposition is to take advantage of policyholders with premium spikes while finding ways to negate or reject legitimate claims. And because many insurers continue to struggle with inadequate systems to facilitate top-notch customer service, that perception continues. Negative perceptions contribute to another mistaken belief: that insurance is a boring industry. Therefore, young and vibrant talent avoid it in favor of other industries such as banking. These negative perceptions tend to have the largest impact in IT, where many workers are retiring from key technology positions, leaving those remaining without the necessary legacy systems knowledge to “keep the lights on.” This is especially critical for smaller insurers with older or outdated legacy systems, because young, innovative technology workers want to be challenged with new technologies, not outdated ones. The dynamic in IT reinforces the need to evaluate your current technology platform and related policy management systems. Moving to a Software as a Service environment is cost-effective, fast, secure and reliable. Consider your underwriting program or customer service efforts—are they best served with outdated technology? What about your distribution network—are your agents able to communicate with you in real time using portal technology, or are they forced to conduct business manually? Are you in a position to employ analytics to improve your business outcomes? See also: Solving Insurtech’s People Challenge   As we move into the next generation, it’s becoming very clear that our industry is anything but boring. Insurtech disruption is affecting companies of all sizes, and our business models are changing as a reflection of the ever-evolving needs of the customer. To best respond to these changes, insurers need to adopt current technologies that will improve the business operations that allow for accurate and agile responses. That same attitude toward modern technology adoption will attract the right talent in all of your organization’s functional business areas. You don’t have to be a company the size of AIG to realize that, without modern technologies, you can’t court the best possible talent. And without the best possible talent, your bench strength will weaken, making it even more difficult to rebuild and successfully compete.

Jim Leftwich

Profile picture for user JimLeftwich

Jim Leftwich

Jim Leftwich has more than 30 years of leadership experience in risk management and insurance. In 2010, he founded CHSI Technologies, which offers SaaS enterprise management software for small insurance operations and government risk pools.

Recognizing exponential innovators

Here are seven companies we believe are Exponentials. These are the companies most likely to produce growth measured not in percentages but in multiples.

sixthings

Revisiting research we published on the 54 companies we cited as Innovators to Watch during 2017, we've identified seven we believe are Exponentials. These are the companies most likely to produce growth measured not in percentages but in multiples. 

Guy Fraker, our chief innovation officer, and Paul Winston, our chief commercial officer, file this report on the Exponentials drawn from our Innovator's Edge platform, which tracks 40,000 companies with some direct link to risk or risk management:

Each of the seven, selected from those that have completed profiles on IE and were recognized in 2017, best meet these criteria:

  • It produces an original solution by leveraging a "domain technology," one that can result in a redefinition of the nature of risk.
  • It states a bold, inspirational mission describing a transformation for an industry or even for humanity.
  • It achieved an exponential outcome in 2017.

The 2017 Exponentials are, in alphabetical order:

AppBus, founded in 2014, integrates in a single environment all the enterprise applications that an insurer might use. The approach makes it easier for employees to securely access the information tools they need while avoiding duplicate data entry. AppBus can combine standard business applications like CRM software with tools being created by insurtech innovators. AppBus augments those services with a library of key content and information to make users more productive. Users can create role-based interfaces to provide the specific tools that individuals need, especially when in the field. 

The firm has a mission that is relatively easy to summarize but that embodies stunning ambitions: increasing security while simultaneously enhancing productivity, ease of access and transparency across business units. That may seem like the natural state, but the world has actually been evolving in the other direction. Insurers have added layers upon layers of new capabilities, but they have largely reinforced existing structures. Insurers may have increased the availability of information, but that has generally not led to greater shared understanding.  AppBus, by enhancing access and security simultaneously, is a quantum leap forward. 

In 2017, the insurance industry became one of the fastest-growing verticals for AppBus. 2017 also saw AppBus achieve a 4X increase in funding and continue their string of technology awards, including a "Best in Show" at PACT Phorum 2017.

Aquaai has a mission to "save the seas by providing intelligence under the surface." It has never been short on inspiration. The robotics firm, founded by Liane Thompson and Simeon Pieterkosky in 2014, never figured risk management would be their first adopter, but in 2017 they agreed to provide robotic fish to a farm that is the lead source of salmon for Whole Foods. The farm uses the robotic fish to assess the integrity of their containment facilities, as well as the health of the salmon, without causing stress for the fish. 

Firms often invent the equivalent of a hammer and then view everything in the world as some sort of nail, but Aquaai adapts its technology to whatever is out there. It creates robots modeled on biology that can be customized to the requirements of the customer. Aquaai's designs can, for instance, perform loss-mitigation tasks routinely associated with flying drones, in conditions far more hazardous. So, risk-management opportunities should abound, from the very small and specific to the very broad and aspirational. 

ClearCut Medical minimizes cancer patients' pain by mitigating repetitive procedures while improving diagnosis, sharply reducing critical treatment timeframes and improving patient survival. Initially focusing on breast-conserving cancer surgery (BCS, or lumpectomy), the team at ClearCut aims to reduce the number of repeat surgeries by at least 75%. The company, founded in 2010 in Rehovot, Israel, has developed a mobile MRI that a surgeon uses in real time to establish that all cancerous tissue has been removed, rather than having to rely on pathological confirmation weeks after surgery.

In 2017, Clearcut made the jump from theoretical to the first stages of commercialization, after clinical trials in 2016 and 2017 that resulted in multiple, well-received publications in medical journals. ClearCut, which has raised roughly $6 million, estimates the total available market to be $1.2 billion for their initial target market of breast cancer patients. One can readily identify additional treatment protocols and opportunities that could benefit from ClearCut's technology, with implications for both health insurers and life insurers.

elevateBenefits tackles a major problem: that navigating healthcare and other employee benefit choices has become, let’s say, confusing over the past few years. Founded in Alpharetta, GA in 2016, elevateBenefits was born from the belief that employee benefits are of profound importance to employers and employees—but that employers often know little about what value their company and employees receive from their benefits.

But even identifying keen frustration doesn't necessarily mean there is a market. elevateBenefits initially found acceptance in the market to be frustratingly slow. It made a major pivot, developing SHRM Broker Finder, which provides simple tools that employers can use to find a broker that is right for them. Brokers signed up because the tool gives them visibility with potential clients. elevateBenefits had found the Holy Grail: a so-called two-sided market. A series of significant alliances and partnerships ensued, with Northern California Human Resources Association, then Citrix, followed by Great Place to Work, culminating with adoption by Society for Human Resource Management. In less than six months, elevateBenefits went from a few new users a month, to around 40 a month, to more than 400 every 60 hours.

GeneYouIn, founded in 2012 out of Toronto, identified a job to be done with such profound implications that quantifying them would be an AI exercise of significant proportions. GeneYouIn has developed a genome analytics and reporting platform called PillCheck. It interprets a patient’s genetic variants to help clinicians better understand how that patient may tolerate a medication in advance of making the prescription decision. In addition to improving the effectiveness of healthcare, including among mental health patients, this technological platform holds promise for aligning pain management treatments with propensities toward addiction. If successful at scale—admittedly a big if for an effort this ambitious—GeneYouIn holds promise for reducing healthcare-related class action lawsuits, for sharply reducing prescription costs and for speeding the development cycle for new pharmacological treatments. Because the firm uses a direct-to-consumer model, patients have the results for their use as they see fit for their healthcare decisions.

Jamii could easily top this list if it weren't in alphabetical order. It aspires to provide a mobile platform for micro-health insurance to African families earning less than $70 a month. Providing such coverage by networking more than 400 hospitals, while partnering with telecom providers for delivery, at a premium of $1 per month stretches the imagination. Jamii was founded in 2015 by Lilian Makoi, out of Tanzania, after a close friend lost her husband, who could not afford medical care following an accident. Tanzania alone has a population of 47 million earning less than $70 per month, and statistics published by Jamii state that approximately 4.2% of the population has health insurance. 

Makoi began with a long series of one-on-one conversations that gave her a deep dive into the problems and insights into possible solutions. She then formed partnerships with established insurer Jubilee and telecom provider Vodafone, and built a cashless and paperless healthcare management platform enabling enormous reductions in cost. 2017 was a breakout year. Jamii won entry to accelerators including Barclay’s Techstars and Disrupt Africa, won the Efma-Accenture Insurance Innovator of the Year award and captured support from the Bill and Melinda Gates Foundation. In mid-2017, Jamii secured their first round of funding, of $750,000, after growing adoption to more than 20,000 users. By the end of January 2018, Jamii had an estimated user base approaching 700,000. 

RiskGenius takes a sort of meta approach to innovation in insurance: Its innovations help the innovators innovate. When the insurance industry embraces a breakthrough technology, it accelerates improvement at a societal scale, but, for all of the insurtech activity, actual product innovation is dfficult, given the matrix of regulatory models, mix of tort law models and complexity of policy language. Creating new products, services and markets and enabling new industries would be significantly easier if tested policy language could be categorized, made searchable and made accessible. Such a capability would enable an exponentially faster policy development cycle.

Enter Chris Cheatham, Doug Reiser and the team at RiskGenius of Overland Park, KS. Chris and Doug launched in 2011 with a better claims management system. In 2014, user feedback during a specific claim raised the idea of a policy forms library. 2015 was the year of exploration, development and leveraging artificial intelligence and machine learning to provide policy analysis. In 2016, RiskGenius launched, then quickly followed with a seed round of funding. By 2017, growth was on an exponential growth curve; highlights included presentations at the World Economic Forum.

A closing observation: After we selected these "2017 Exponentials," we took one last look to better understand what they have in common. It wasn't location: The seven firms are located in the U.S., Israel, Tanzania and Canada. It wasn't technology: The seven span artificial intelligence, machine vision, networking and distribution and human genome sequencing. We found one, only one, aspect in common: Seven of the seven firms have women on their senior-most leadership teams or were founded/co-founded by women, even though only 7% of venture capital in 2017 went to firms launching with gender diversity and even though roughly 17% of all tech startups include women on management teams. 

Hold that thought. ITL is finalizing a free addition to the Innovator's Edge platform: the ability of individuals to join groups for discussion, feedback and collaboration. "Women in Leadership" will be among the first groups to launch. Given the importance of the team when vetting opportunities with early-stage firms, we at ITL want to support the role of women. We'll provide more details shortly.

Have a great week.

Paul Carroll
Editor-in-Chief


Paul Carroll

Profile picture for user PaulCarroll

Paul Carroll

Paul Carroll is the editor-in-chief of Insurance Thought Leadership.

He is also co-author of A Brief History of a Perfect Future: Inventing the Future We Can Proudly Leave Our Kids by 2050 and Billion Dollar Lessons: What You Can Learn From the Most Inexcusable Business Failures of the Last 25 Years and the author of a best-seller on IBM, published in 1993.

Carroll spent 17 years at the Wall Street Journal as an editor and reporter; he was nominated twice for the Pulitzer Prize. He later was a finalist for a National Magazine Award.

PPOs and the $444 Box of Kleenex

Healthcare providers set astronomical, arbitrary prices, and employers and insurers have few options. But a solution is emerging. #PPOGate

|
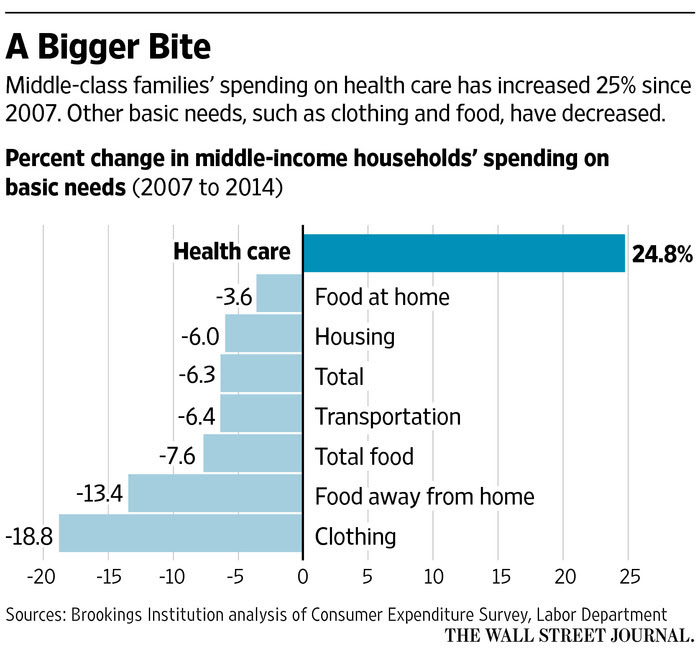
#The Affordable Care Act requires every health plan to offer benefits free from most annual and all lifetime dollar limits. If you have a self-insured plan, you may feel the direct impact of this a little more immediately (although many employers still do not recognize it). Even employers that are fully insured should realize they are the insurance company anyway. The only benefit those employers get is delaying the impact of employees' healthcare spending until their next renewal date. But employers pay dearly in the form of a complete lack of information on exactly how that money is being spent. As a result, companies should start to look at the health plan ID card as an unlimited corporate credit card. Which then raises the question: Who is monitoring that spending? That unlimited credit card rings up charges like a $444 box of Kleenex (described on the hospital bill as a mucus collection device) and $1,000 toothbrushes, and those are the trivial problems, the ones that can draw a chuckle. Those trivial things need to draw attention to a much broader problem, such as $10,000 surgeries that employers blindly pay $180,000 for. With the majority of the workforce having a high-deductible plan, every day that goes by it's less and less "other people's money" and more of the employee's, so we're starting to see legal activity -- even before a formal declaration from the Department of Labor that health benefits must be managed by employers with the same level of scrutiny as retirement benefits. [For more detail, you can download “ERISA Fiduciary Risk Is the Largest Undisclosed Risk I’ve Seen In My Career” -- a chapter that was added to the recently released new edition of the CEO's Guide book.] Most employers use networks as their primary strategy to control that spending. Carrier networks love to tout their average discounts. “We save plans 60% on average off billed charges!” Well, there are two major problems with networks. First, what is that discount off of? Generally it is off the “ChargeMaster” rate. What is the ChargeMaster, you ask? The ChargeMaster, also known as charge description master (CDM), is a comprehensive listing of items billable to a hospital patient or a patient’s health insurance provider, with highly inflated prices -- several times that of actual costs to the hospital. The ChargeMaster typically serves as the starting point for negotiations with patients and health insurance providers of what amount of money will actually be paid to the hospital. It is described as “the central mechanism of the revenue cycle” of a hospital. We have seen a billed charge of $1,000 from a hospital for a manual toothbrush. 60% off that is still one expensive toothbrush. We found a $444 charge for a “mucous collection device” later found to be a box of tissues. Not to mention, the billed charges vary so dramatically, even within the same facility that a finite percent off an infinite number has zero credibility. While one ex-hospital CEO describes the ChargeMaster as archaic fiction, it does play into the general obfuscation designed to keep healthcare costs growing. [Please add your comments below if you have other real-world examples like the $1,000 toothbrush, $444 box of tissues, etc. Or share on social media articles and examples with the hashtag #PPOGate, which people are using to highlight how blind faith in PPO networks has inflicted pain on the working and middle class.] You might think that all hospitals have similar Chargemaster prices. Nothing could be further from the truth. The Huffington Post did a story when treatment costs were first made publicly available from a federal database in 2013, in which they found the cost to treat COPD (chronic obstructive pulmonary disorder) in the New York City area can range from $7,044 to $99,690. Herein lies the fundamental problem: Back when we had richer health plans, patients didn’t care about the cost, as long as insurance covered it. Now that we are being left with these crazy-high deductibles, we are blaming the insurance company for the plan design (and the cost thereof) that leaves us with this exposure. See also: Medicare Set Asides: 10 Mistakes to Avoid   Every facility that participates in Medicare and Medicaid is required to file their actual cost, all in, with the Centers for Medicare and Medicaid Services (CMS), and anyone can access this data for a subscription fee. In Charlotte, N.C., the two largest hospitals systems file their cost for a CT scan as being between $75 and $90. Their average billed charge to a health plan? Between $1,800 and $2,700! The hospitals claim they have to charge higher prices to private insurance plans because of the below-cost care they provide to Medicare and Medicaid patients and the “free” care they provide to the uninsureds through the emergency room. Well, uninsured ER rates have dropped significantly under the ACA (and actual ER usage has gone up), and ER rooms are highly profitable to the hospitals for those who have insurance, so shouldn’t there be a positive overall impact on the private insurance pricing? Also, if I go a buy a car, and get a super deal from the dealership, will you be OK being the next customer in the door and being told you have to overpay because the dealer gave some stranger before you a really good price? I think not. The second problem with PPO networks is that nearly every network contract prohibits the plan (and the employer, by extension) from auditing a bill. The contract actually prohibits the plan from even requesting an itemized bill! All they can get is what’s called a UB, or a universal bill. You can see the form here. Other than the information on who the patient is and whom to pay, the UB only shows total charges and diagnosis. As long as the diagnosis is a covered condition under the plan, the discount gets applied, and the bill gets paid. Bills on this form can easily be hundreds of thousands of dollars. When we have asked for an itemized bill (that the insurance company can’t ask for), we have found pregnancy tests on men and charges for 16 surgical screws when only four were used, just to name a few “errors.” We have heard firsthand stories where an insurance executive sat down with hospital executives and said, “We need a bigger discount from you guys,” and the execs said no way. So the insurance exec said, “I don’t think you understand…you can bill us more, and it can even net out to more than we pay you now, we just need to say we have a bigger percent off.” Another perverse incentive to be aware of that came as a result of the ACA is called the medical loss ratio. Under this provision, insurance companies must spend between 80% and 85% of the premiums they receive for medical care for the insureds. If they spend less than that, they must provide a refund. Prior to this law, carriers could keep the difference for profit, so they had stronger encouragement to keep costs down. Now, the only way they can charge their customers more, and thereby boost profits, is if the underlying cost of care also goes up. We're not blaming the insurance companies. They had to bow to the pressure of their customers (employers) because, if that big local hospital system left their network, they thought customers would leave in droves. (Pittsburgh schools are proving that assumption wrong with a good plan design and collaboration with their teacher union -- details are in the CEO's Guide book that you can download free.) The insurance companies are in a tough spot. If they try to “manage” the care -- i.e. pre-certification, tiered drug formularies and narrow networks -- their customer base gets ornery. And employers are loath to be seen as getting involved in their employees’ healthcare. I bet most employers don’t want to tell employees where to sleep or what car to drive, either, but I imagine they nonetheless have parameters around how much can be spent for rental cars and hotels when traveling on the company dime. Fortunately, there are employers all over the country that have wised up and tamed the out-of-control healthcare cost beast. They are spending 20% to 55% less than a typical employer on a per capita basis. Paradoxically, they are finding the best way to slash healthcare costs is to improve health benefits. There are several examples in the CEO's Guide book that range from school districts in the Rust Belt to a municipality in the Midwest to a small manufacturer in the heart of oil country to a hotelier in Florida. Another statistic carriers love to tout is their auto-adjudication rates (in other words, automatic and prompt payment of claims as they come in). After all, higher auto-adjudication means the providers get paid quicker. And that means fewer headaches for providers and employees. But that also suggests that a 94% auto-adjudication rate means that 94% of the time no one is looking at the bill even to the limited level the contract permits. The same company will reject an expense report submitted by an employee missing a $62 restaurant receipt and then blindly pay a $100,000 medical bill without any detailed review. So let’s review:
  1. Although carrier networks have some influence over the discount, they have little over the starting price.
  2. Hospital charges are filed on a UB (universal bill), and the plans are contractually prohibited from asking for an itemized bill.
  3. If the plan requests any audit at all, they are required to pre-pay the claim, often at 100%, and are then subject to the hospital’s own audit procedures.
  4. Networks are forced to accept these terms, or their customers will leave because they do not have a broad network.
See also: Healthcare Data: The Art and the Science   Sounds like the fox is watching the henhouse. The abuses that can and do exist under this model are egregious (see Chapter 6 from the book, PPO Networks Deliver Value -- and Other Flawed Assumptions Crushing Your Bottom Line). Different strategies are just starting to take shape and mature that expand whom your employees can see by removing the network completely and letting them go wherever they want. When the network contract is gone, the plan sponsors can deploy much more aggressive strategies to not only reduce the fraud and abuse but significantly reduce costs on the legitimate charges. Some employers are contracting with providers directly and, more often than not, with a local hospital looking to compete against the behemoth health systems. Under ERISA, plan sponsors (the employer) have a fiduciary responsibility to protect plan assets. Because many network contracts prohibit the plan from auditing the bill, and the few that do require 100% of the allowed charges to be paid before an audit can begin, how can a plan sponsor meet its fiduciary requirement under ERISA to be good stewards of plan assets? Old-line benefits brokers continue to advise their clients to sign such egregiously one-sided contracts -- those benefits consultants are going the way of the dodo bird but leave their clients exposed in the meantime. I can say with 100% certainty that plaintiffs' attorneys are gathering their ammunition for these ERISA cases. When you combine the fact that healthcare's hyperinflation has been the overwhelming driver of 20-plus years of wage stagnation and decline and look at the impact on household spending in the graph, the pain inflicted on the working and middle class is palpable. Smart employers and their benefits consultants are avoiding having a target on their back by taking action now. By applying the best practices captured in the Health Rosetta and various other tools that will be highlighted in the forthcoming book CEO's Guide to Restoring the American Dream - How to deliver world class healthcare to your employees at half the cost, there are many tools to provide employees a world-class health benefits package without giving a blank check to the healthcare industry. Written with David Contorno, President, Lake Norman Benefits

Dave Chase

Profile picture for user DaveChase

Dave Chase

Dave has a unique blend of HealthIT and consumer Internet leadership experience that is well suited to the bridging the gap between Health IT systems and individuals receiving care. Besides his role as CEO of Avado, he is a regular contributor to Reuters, TechCrunch, Forbes, Huffington Post, Washington Post, KevinMD and others.

How Risk Produces Financial Success

The implementation of enhanced risk management practices represents a tremendous opportunity, while lowering D&O premiums.

sixthings
The evolving environment across economics, demographics and geopolitics, paired with the continuing pace of technological change, is creating an increasingly complex risk landscape for all types of businesses. We are continuing to witness increased connections of potential risk impact on organizations. Never has it been more critical for organizations to consider the relationship between building sustainable competitive advantages and adopting risk management best practices. It is incumbent on organizational executives and key leaders to take steps to increase their understanding of the risks they face to adapt to the changing environment. In addition, technology offers tremendous growth opportunities in the form of operational performance, automation, new products and services, new and enhanced distribution channels and improved business intelligence. However, the use of technology also increases exposure to cyber risk, which is a key concern. The impact of connected risk has been felt by many organizations. Increasingly, boards are being obligated, in the case of regulated entities, or challenged to be acutely aware of and understand the key risks their organizations face and how they are being managed. The ability to understand, manage and develop effective organizational governance and processes that encourage improved risk-based decision-making is imperative to an organization’s financial and operational well-being. In pursuit of the strategic objective to deliver value back to stakeholders, most organizations seek to grow their revenue or drive operational performance and efficiencies within their operating model. Invariably, in today’s complex and evolving environment, there is a level of uncertainty created in the tactical pursuit of such initiatives. Understandably, a greater level of uncertainty equates to a greater level of volatility in financial performance. See also: How to Use Risk Maturity Models   Researchers at Aon continue to identify correlations between advanced risk management capabilities and higher stock price performance for publicly traded organizations. Reducing volatility via the implementation of robust risk management practices should be a core objective for organizational leaders, as research repeatedly shows that higher levels of risk maturity correlate to lower stock price volatility. Factors That Distinguish Organizations With Higher Levels of Risk Maturity Risk professionals have long recommended a structured enterprise-wide risk identification and assessment process for organizations to tackle current and emerging risks. The Aon Risk Maturity Index Insight Report, developed by Aon in close collaboration with the Wharton School of the University of Pennsylvania, identifies three key factors to successfully understanding and managing risk:
  • Awareness of the complexity of risk
  • Agreement on strategy and action
  • Alignment to execute
Increasing performance along these dimensions requires a robust process that focuses on:
  • the identification of strengths and weaknesses
  • strong communication of risks and risk management across functions and at all levels of the organization
  • building consensus regarding the steps to be taken
Having different functions and levels involved and integrated into an organization’s risk maturity assessment process provides the foundation for determining an organization’s current status along these dimensions and provides the foundation for identifying continuing improvement activities. Aon and Wharton researchers found continued positive impacts on stock price performance and company profitability from higher risk maturity, underscoring the positive internal and external benefits that a robust and sustainable risk management program can deliver. In addition to a cross-functional understanding of risk, the use of sophisticated quantification methods is another key characteristic exhibited by organizations with advanced risk maturity. Aon and Wharton research shows that organizations with higher levels of risk maturity successfully integrate the use of advanced risk quantification techniques and the utilization of those outputs in the risk decision-making process. The Relationship Between Risk Maturity and Directors and Officers (D&O) Insurance Premium Reductions in insurance premiums are another potential financial benefit from more mature risk management processes. This can occur through two channels. First, insurance providers are likely to lower insurance premiums for firms they view as less risky, as reflected in lower volatility. Second, better understanding of risk exposures and their drivers, together with the consistent development and application of risk appetite and risk tolerance concepts to decision-making, provides the information needed to make more informed decisions about which risks to avoid, mitigate or accept and which risks to insure. By optimizing their insurance portfolio through more mature application of risk management processes, firms can potentially reduce premiums by avoiding or mitigating the most costly risks, choosing only the level of coverage that is necessary given the firm’s risk appetite and tolerances, and improving its bargaining position with insurers. See also: Why Risk Management Certifications Matter   What’s more, Aon and Wharton research finds that firms with higher overall risk maturity scores paid significantly lower premiums for D&O insurance. Just a 10% increase in overall risk maturity scores is associated with D&O premiums that are 2.6% lower than the premiums paid by similar firms. This direct benefit does not take into account the indirect premium benefits that also arise from lower volatility -- and thus lower premiums in firms with higher risk maturity. When we calculate the total effects of higher risk maturity on D&O premiums, including the benefits from lower volatility, the premium reduction associated with a 10% improvement in risk maturity scores increases to 3.9%. Conclusion The implementation of enhanced risk management practices represents a tremendous opportunity for all types of businesses to reduce the volatility associated with the evolving risk landscape while also leveraging the associated benefits to their D&O insurance programs.

Kieran Stack

Profile picture for user KieranStack

Kieran Stack

Kieran Stack leads and oversees the combined Aon Global Risk Consulting U.S. growth teams and initiatives and approach to innovation. He also has global project lead responsibility for the Aon Risk Maturity Index co-developed with Wharton School of the University of Pennsylvania.

How to Innovate With Microservices (Part 1)

The microservices approach to IT systems provides great flexibility, addressing the issues of monolith architectures that inhibit digital business models.

||
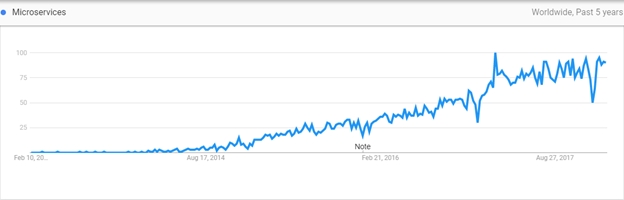
Whether you are part of building a modern digital enterprise platform for mid-sized to large insurance companies or part of a startup that distinguishes itself through innovative technologies, you are likely to be hearing about microservices. Microservices architecture has increasingly become popular and often associated with benefits such as scale, speed of change, ease of integration, fault tolerance and ability to adapt to changing business demands and models. Commitment from digital giants such as Amazon, Netflix, PayPal, eBay, Twitter and Uber, which built and scaled their platforms based on microservices architecture, has galvanized adoption across many industries. [caption id="attachment_30424" align="alignnone" width="570"] Source: Google Trends[/caption] A crucial question is, “How will microservices help insurers design open platforms for building sustainable competitive advantage?” This four-part blog series will share our views based on our experience in building a modern digital platform using microservices. This first blog will provide a general primer about microservices. The second will share our view on the applicability and strategic potential of microservices for insurance. The third will illustrate best practices and applied principles of designing a microservices-based platform. The final blog will share how our innovative Majesco Digital1st platform will help insurers simplify and accelerate the development of microservices apps. Let’s start with the basic question, “What are microservices?” You can find the answer through a simple Google search, but let’s explain it in simple terms. Think of a microservice as a micro application that enables a specific granular business function like payment, issue, policy documents, first notice of loss (FNOL), etc.  The micro application can be independently deployed and can communicate with other micro applications serving other business functions through a well-defined interface. This approach is in stark contrast to “monolith applications,” such as policy management systems, billing systems and claims systems that work as an aggregation of multiple business functions tightly woven together and must be deployed as a large, monolithic unit. See also: It’s Time to Accelerate Digital Change   An architectural pattern called self-contained-service (SCS) is often discussed along with microservices but does not provide the full benefits of microservices. The SCS pattern recommends putting cohesive services together as a self-contained, individually deployable unit. Because the individual services are no longer self-contained and individually deployable, they cannot be considered microservices. While this approach is better than the monolithic application, it is instead building multiple small monoliths! So why does anyone advocate the microservices approach? Simply put, it addresses the issues of monolith architectures that inhibit digital models. Even after functional decomposition and the use of several deployment artifacts with monolith architectures, they are still part of a single code base that must be managed as a single deployment unit. In contrast, a microservices architecture has the following advantages when done well:
  1. Velocity and Agility – Maintenance and evolution of monolith applications is expensive and slow due to inadvertent side effects, because they affect other functions and services. Dealing with the side effects requires additional work, including vital tasks such as impact analysis, elaborate and expensive testing and forcing changes into large and infrequent releases to optimize testing efforts. In contrast, a microservice is a low-impact, single-responsibility business function that performs its own individual tasks, manages its own data and communicates with other microservices through a well-defined interface. It allows you to make and deploy changes reliably, incrementally and more quickly, in contrast to monolith architectures.
  2. Scale – Microservices allow easy monitoring that can predict seasonal or unique business demands on a business function. Because each microservice runs in its own process, it can easily be scaled with elastic containers, which efficiently scale up and down. In comparison, a monolith architecture runs multiple business functions under a single process, making it harder to orchestrate the feeding of resources to targeted business functions.
  3. Decentralized Governance and Teams – The separated code base of microservices allows different parts of an organization to build business functions as opposed to a centralized large team. Each team can manage different microservices with full DevOps (development and operations) responsibility and accountability. This gives insurers the freedom to choose the technology best-suited for the business function.
  4. Self-Contained and Sustainable – With monolithic applications, when introducing a new business capability that requires the upgrade of external dependencies (OS, shared libraries, etc.) the entire application must be tested. In contrast, microservices are self-contained from OS down to the actual code required for implementation. This enables microservices to separately and individually upgrade without affecting unrelated application functions based on business/operational needs. This keeps the application stack relevant and avoids the risk of running applications on an obsolete technology stack.
  5. Hypothesis-Driven Development – The advantages outlined above lead to a completely different way of contemplating software development. The focus and conversation shifts from managing projects and defect backlogs to emphasizing new opportunities, experimentation and observing the application usage. Experimental software changes can be built and deployed quicker in small increments into production. When errors happen, they can be fixed in minutes and hours, rather than days or months. For major problems, the incremental functionality upgrade can quickly and easily be rolled back without loss of major functionality or downtime.
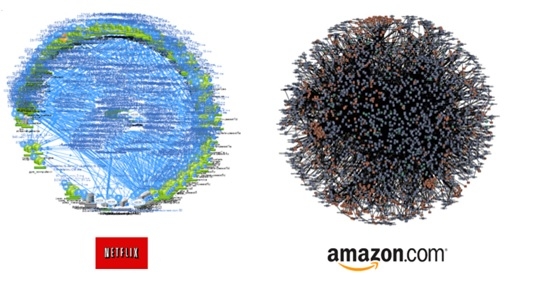
As with all innovation, there is a flip side to the coin. Unfortunately, not all organizations are ready to adopt a microservices architecture immediately. In particular, if a company cannot build a well-designed monolith, then building a microservices platform will be much harder. Microservices architecture is inherently complex to develop as well as operate, but the rewards of the complexity are worth the hurdles, because microservices will give the reconstructed organization far greater efficiency and capabilities focused on the future. Fundamentally, microservices require organizational change, not just adoption of a technology pattern. Organizations must rethink end-to-end DevOps by thinking in terms of small business functions, distributed teams, decentralized governance and continuous delivery. In addition, the organization must embrace multiple technologies suited for a business platform rather than a single technology platform, which is a significant change for organizations schooled in building applications using traditional software development processes. Even success stories like Amazon and Netflix did not start with a microservices architecture; rather, they evolved overtime as they matured. If you are building a MVP (minimum viable product) as a startup, it may not be advisable to delay market launch due to the large up-front effort of establishing microservices. However, startups should consider that at some point they’ll have to invest and migrate to microservices to support scalability and changing business models. Operating a platform made of hundreds or thousands of microservices, while enabling scalability and growing business demands, does create tremendous complexity for deployment, auto-scaling, monitoring, logging and many other DevOps aspects. Microservices deployment at Amazon and Netflix (Images by AppCentrica) show the complexity of managing a reliable business operation with millions of continuing deployments within an ecosystem of microservices — often written using different languages and databases. Companies like Amazon and Netflix deal with this complexity through a high degree of automation and significant investment into sharing and automating the infrastructure to build resiliency. Despite the complexity in managing microservices, separation of responsibilities across microservices offers organizations significant benefits in today’s platform economy. We outline these in our thought leadership report, Cloud Business Platform: The Path to Digital Insurance 2.0. The constant pivoting of business priorities requires a continuous and high degree of system changes that enable new strategies. Microservices can bring great value to agility, velocity, availability, scalability and accountability across both technical and business organizational dimensions. See also: A New Way to Develop Products   We believe that every organization should exercise patient urgency, which author and futurist Chunka Mui describes as "the combination of foresight to prepare for a big idea, willingness to wait for the right market conditions and agility to act straight away when conditions ripen.” We look forward to covering our views on the role of microservices in insurance in Part 2. Please share your views on this exciting topic in the comments section. We would enjoy hearing your perspective. This article was written by Manish Shah and Sachin Dhamane.

Denise Garth

Profile picture for user DeniseGarth

Denise Garth

Denise Garth is senior vice president, strategic marketing, responsible for leading marketing, industry relations and innovation in support of Majesco's client-centric strategy.

What if Your Insurer Won't Pay?

Here are the things to do legally if you’re having problems with your insurance company paying out.

Disclaimer: If you have problems with insurance payouts, the following information only works as general guidance as to the legal process. It does not, however, function as actual legal advice about the matter. To further understand the legal aspect of insurance payouts, it’s best that you approach a licensed attorney who has experience in insurance claims lawsuits similar to yours. When you’ve been in an accident, the next big thing to do is to file your insurance claims with your insurance company. In fact, you’re somehow relieved because you are hoping that you’ll be paid for all your financial losses as a result of the accident. You’ve submitted your claim on time -- only to find out that you’re having a difficult time getting your insurance claims paid by your insurer. You’re now behind on your bills and don’t want to ruin your credit score or, worse, need to file for bankruptcy. So, here are the things to do legally if you’re having problems with your insurance company paying out. Reasons Why You’re Having Trouble Getting Your Insurance Claims It’s difficult to think that your insurance company can deny your claim or decline to pay the amount you’re expecting for. Below are some of the reasons why your insurance provider can refuse or does not pay the whole amount you’re asking for:
  • Check if you’ve stated the facts in your documentation properly. Remember, insurance companies may conduct their own investigation on your application, so it’s best that you provide them with documents that are valid and up to date.
  • Make sure you follow the right processes in terms of filing your claims. If you’ve skipped a step or missed a requirement, you may end up going back to square one.
  • It’s important to see if you’re up to date with your payments for your insurance. Sometimes, insurance companies disregard applications for claims because applicants have failed to complete their payments.
See also: Distribution: About To Get Personal   Things to Do Legally When You Have Problems With Your Insurer Paying Out These are the things to do legally when you have problems with your insurer paying out: 1. Know What Insurance Claims Your Policy Covers
  • Make sure that what you’re asking for applies to your active and existing insurance policy.
  • Ensure that your insurance claims are not included in the exclusion clause of your policy
2. Keep All Your Communications and Documents Intact
  • Note the procedures you have to go through to file an insurance claim. If you can get information as to how long a particular process can take and if there are specific deadlines, do so to get a general idea on the timetable of your claim.
  • Remember that keeping documents can save you from any accusations your insurance company may throw at you.
  • Note the requirements and other documentation you need to comply with. If you have these documents, make sure you have copies and don’t lose the original versions. These can be useful if ever you have to present these to experts, or if you have to take your claim to the court.
When you’re beginning to experience problems with your insurance applications, take a deep breath and try to be more persistent regarding your follow-ups and inquiries. If you think you need to learn more about your particular issue, you may want to consider hiring an experienced lawyer. 3. Get a State Insurance Regulator or a Lawyer: When problems arise with your insurance provider, it’s essential that you settle the dispute among yourselves in a calm and patient manner. However, if you still end up having difficulties, you may ask the assistance of a state insurance regulator or a lawyer.
  • When hiring a state insurance regulator or a lawyer, note their particular specialization and make sure they’re appropriate for the kind of issue you’re tackling. Try to inquire if they are aware of certain policies in your state, as some laws vary depending on where you reside.
  • If you get a state insurance regulator or a lawyer, use this opportunity to get to learn everything you can about your particular issue, to avoid encountering the same problems in the future.
4. File a Lawsuit: Your last remedy could be the filing of a lawsuit. The things to keep in mind are:
  • Hire a licensed lawyer who has experience in insurance lawsuits.
  • Prepare for the deposition (under oath) and trial, where you have to present documentation to validate your claim.
  • Wait for the final judgment – The jury will resolve the case in one party’s favor. If the result does not favor your side, speak to your lawyer for a possible appeal. Remember, just because the decision doesn’t favor your side, it doesn’t mean it’s too late for your insurance payment.
See also: ‘It’s Life, Jim, but Not as We Know It’   If you feel that your legal rights have been violated by your insurer, don’t hesitate to practice your rights under the law. Check your state laws and initiate the appropriate course of action.

Eugene Umbridge

Profile picture for user EugeneUmbridge

Eugene Umbridge

Eugene Umbridge is equipped with more than 20 years of experience as a businessman. He is currently writing informative pieces for Bankruptcy Attorney Las Vegas and hopes his pieces will impart vital knowledge to his readers.